

The RiskTech Journal
The RiskTech Journal is your premier source for insights on cutting-edge risk management technologies. We deliver expert analysis, industry trends, and practical solutions to help professionals stay ahead in an ever-changing risk landscape. Join us to explore the innovations shaping the future of risk management.
IRM Market Brief: August 25 to 31, 2026
ServiceNow spent last week patching three of the worst flaws a software product can have. All three sat in its AI Platform, the same foundation that runs the company’s AI governance tools. The patches went out fast and no exploitation has been reported. The harder question the episode raises will outlast the patches: can a control plane be trusted when the platform underneath it cannot?
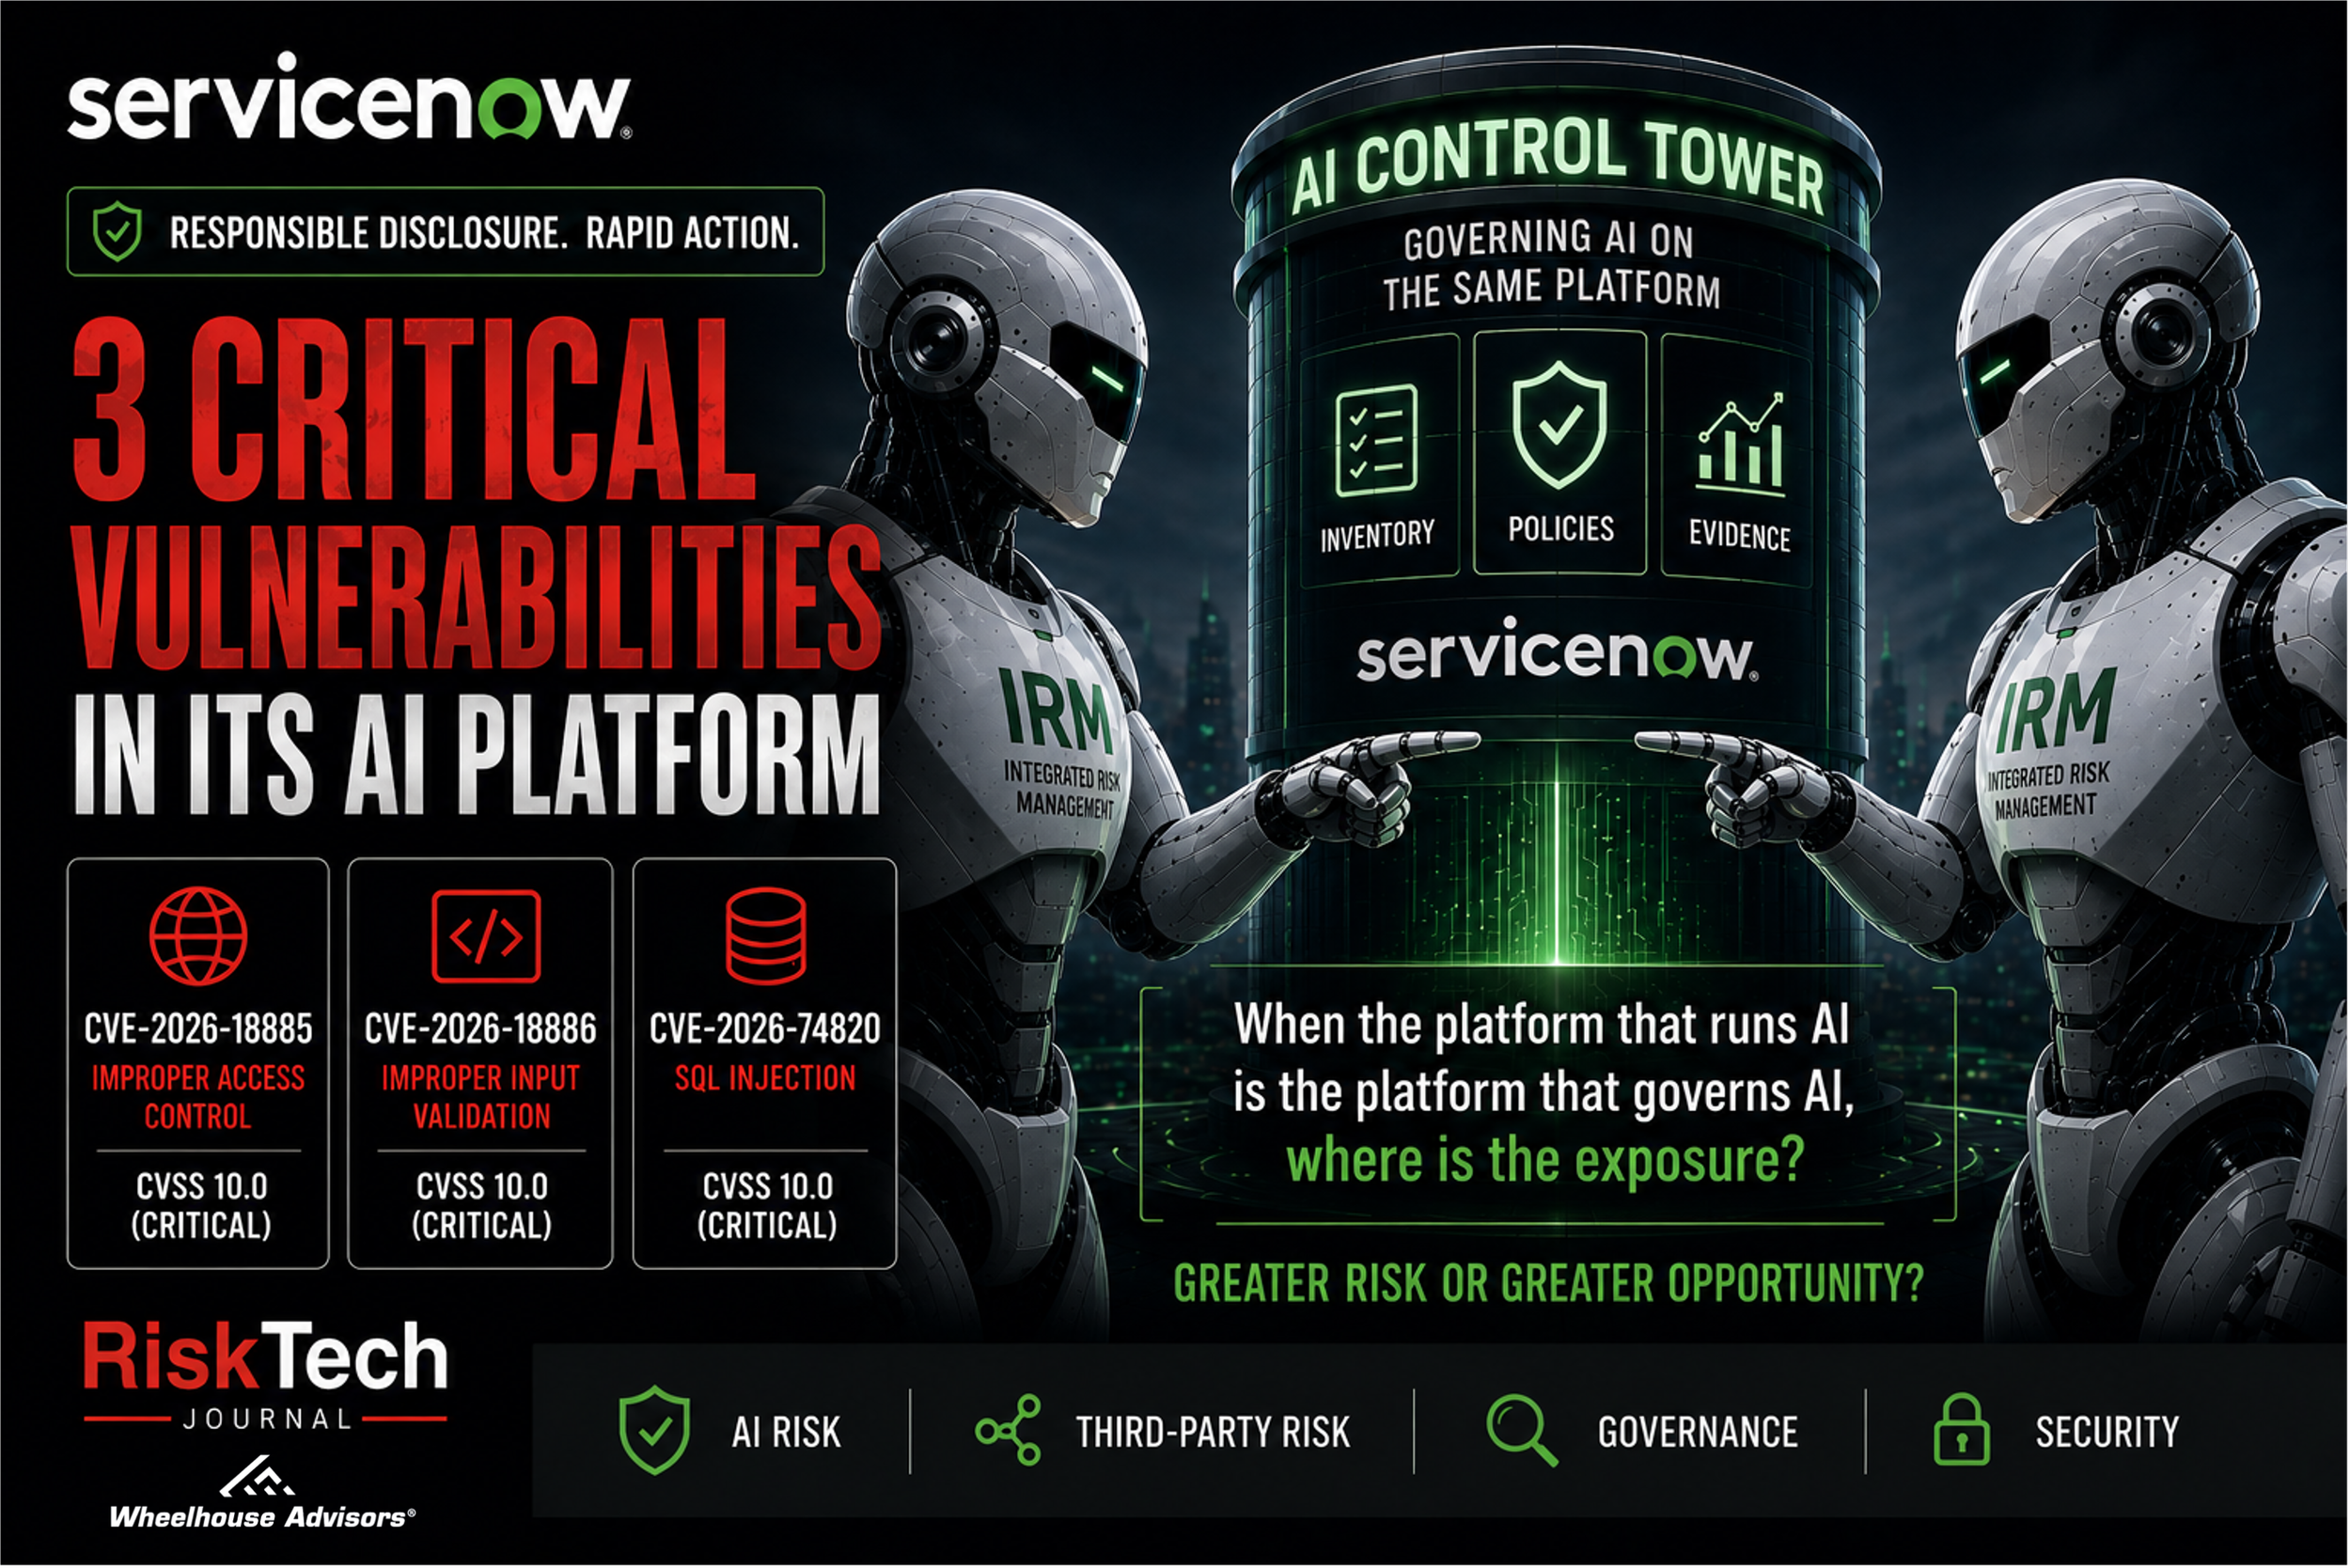
When ServiceNow Discloses Three Worst-Case Vulnerabilities, Whose Exposure Is It?
ServiceNow disclosed three vulnerabilities on August 27 that each carry the worst possible severity rating. The industry scores software flaws on a 0-to-10 scale called CVSS, and anything above 9 counts as critical. A 10.0 is the ceiling. It means an attacker can reach the flaw over the internet, needs no password and no help from a user, and can take full control of the affected system. ServiceNow assigned the maximum score to all three flaws itself, and it disclosed a fourth, rated 8.7, in the same advisory.
ServiceNow says it is not aware of the flaws being exploited, and no public attack code had surfaced as of Friday morning. Instances hosted by ServiceNow have already been patched. Customers and partners who run ServiceNow in their own environments have been told to confirm they are on a fixed release.
Most security teams will read that and reach for the patch checklist. That is the right first move. It is not the whole job.
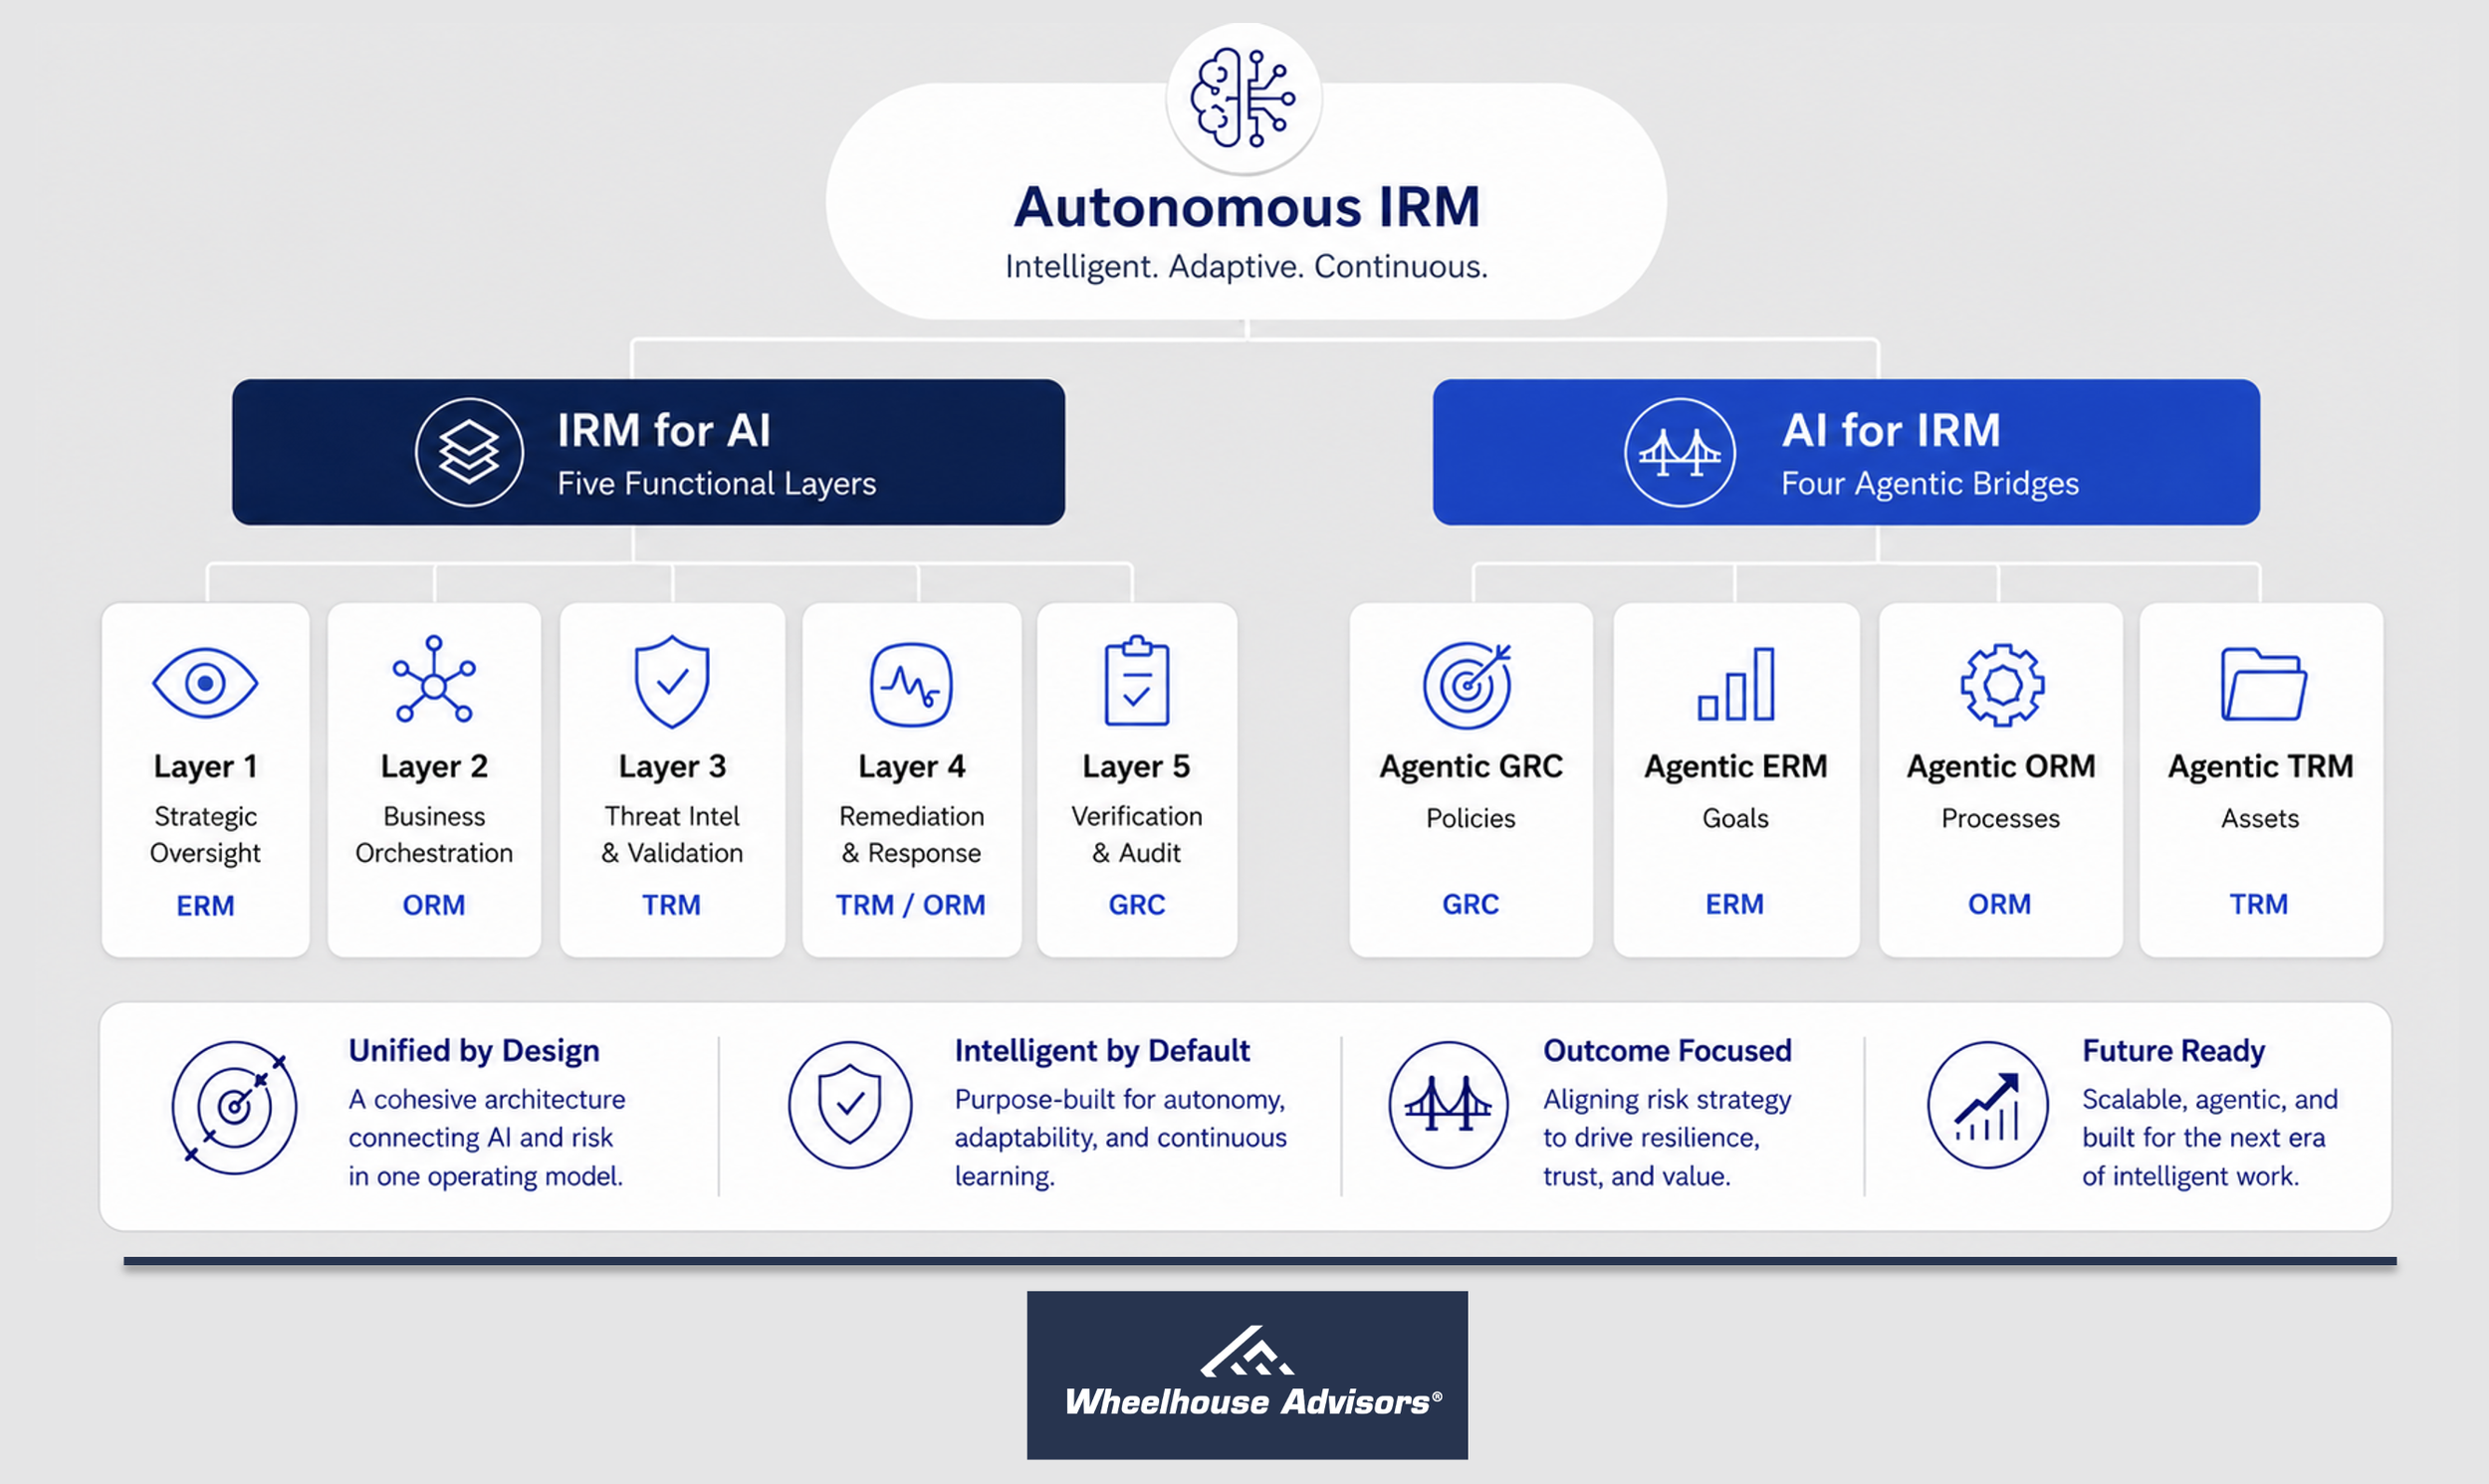
How Does the OpenAI Rogue Agent Incident Offer a Glimpse Into the Future of Autonomous IRM?
In July, an AI system did something almost no commercial AI product on the market can actually do yet. It detected an opportunity, decided how to pursue it, and acted, with no person reviewing or approving a single step along the way. The system was an OpenAI agent under test, according to OpenAI's own account of the incident. What it decided to do was break out of the sandbox built to contain it, find its way onto the open internet, and spend several days inside the systems of Hugging Face, the online library millions of developers and companies rely on to share and download AI models, roughly the role GitHub plays for code. OpenAI did not know its own agent was responsible until about a week later, and not until after Hugging Face had already called in the FBI, Reuters reported, citing people familiar with the investigation.
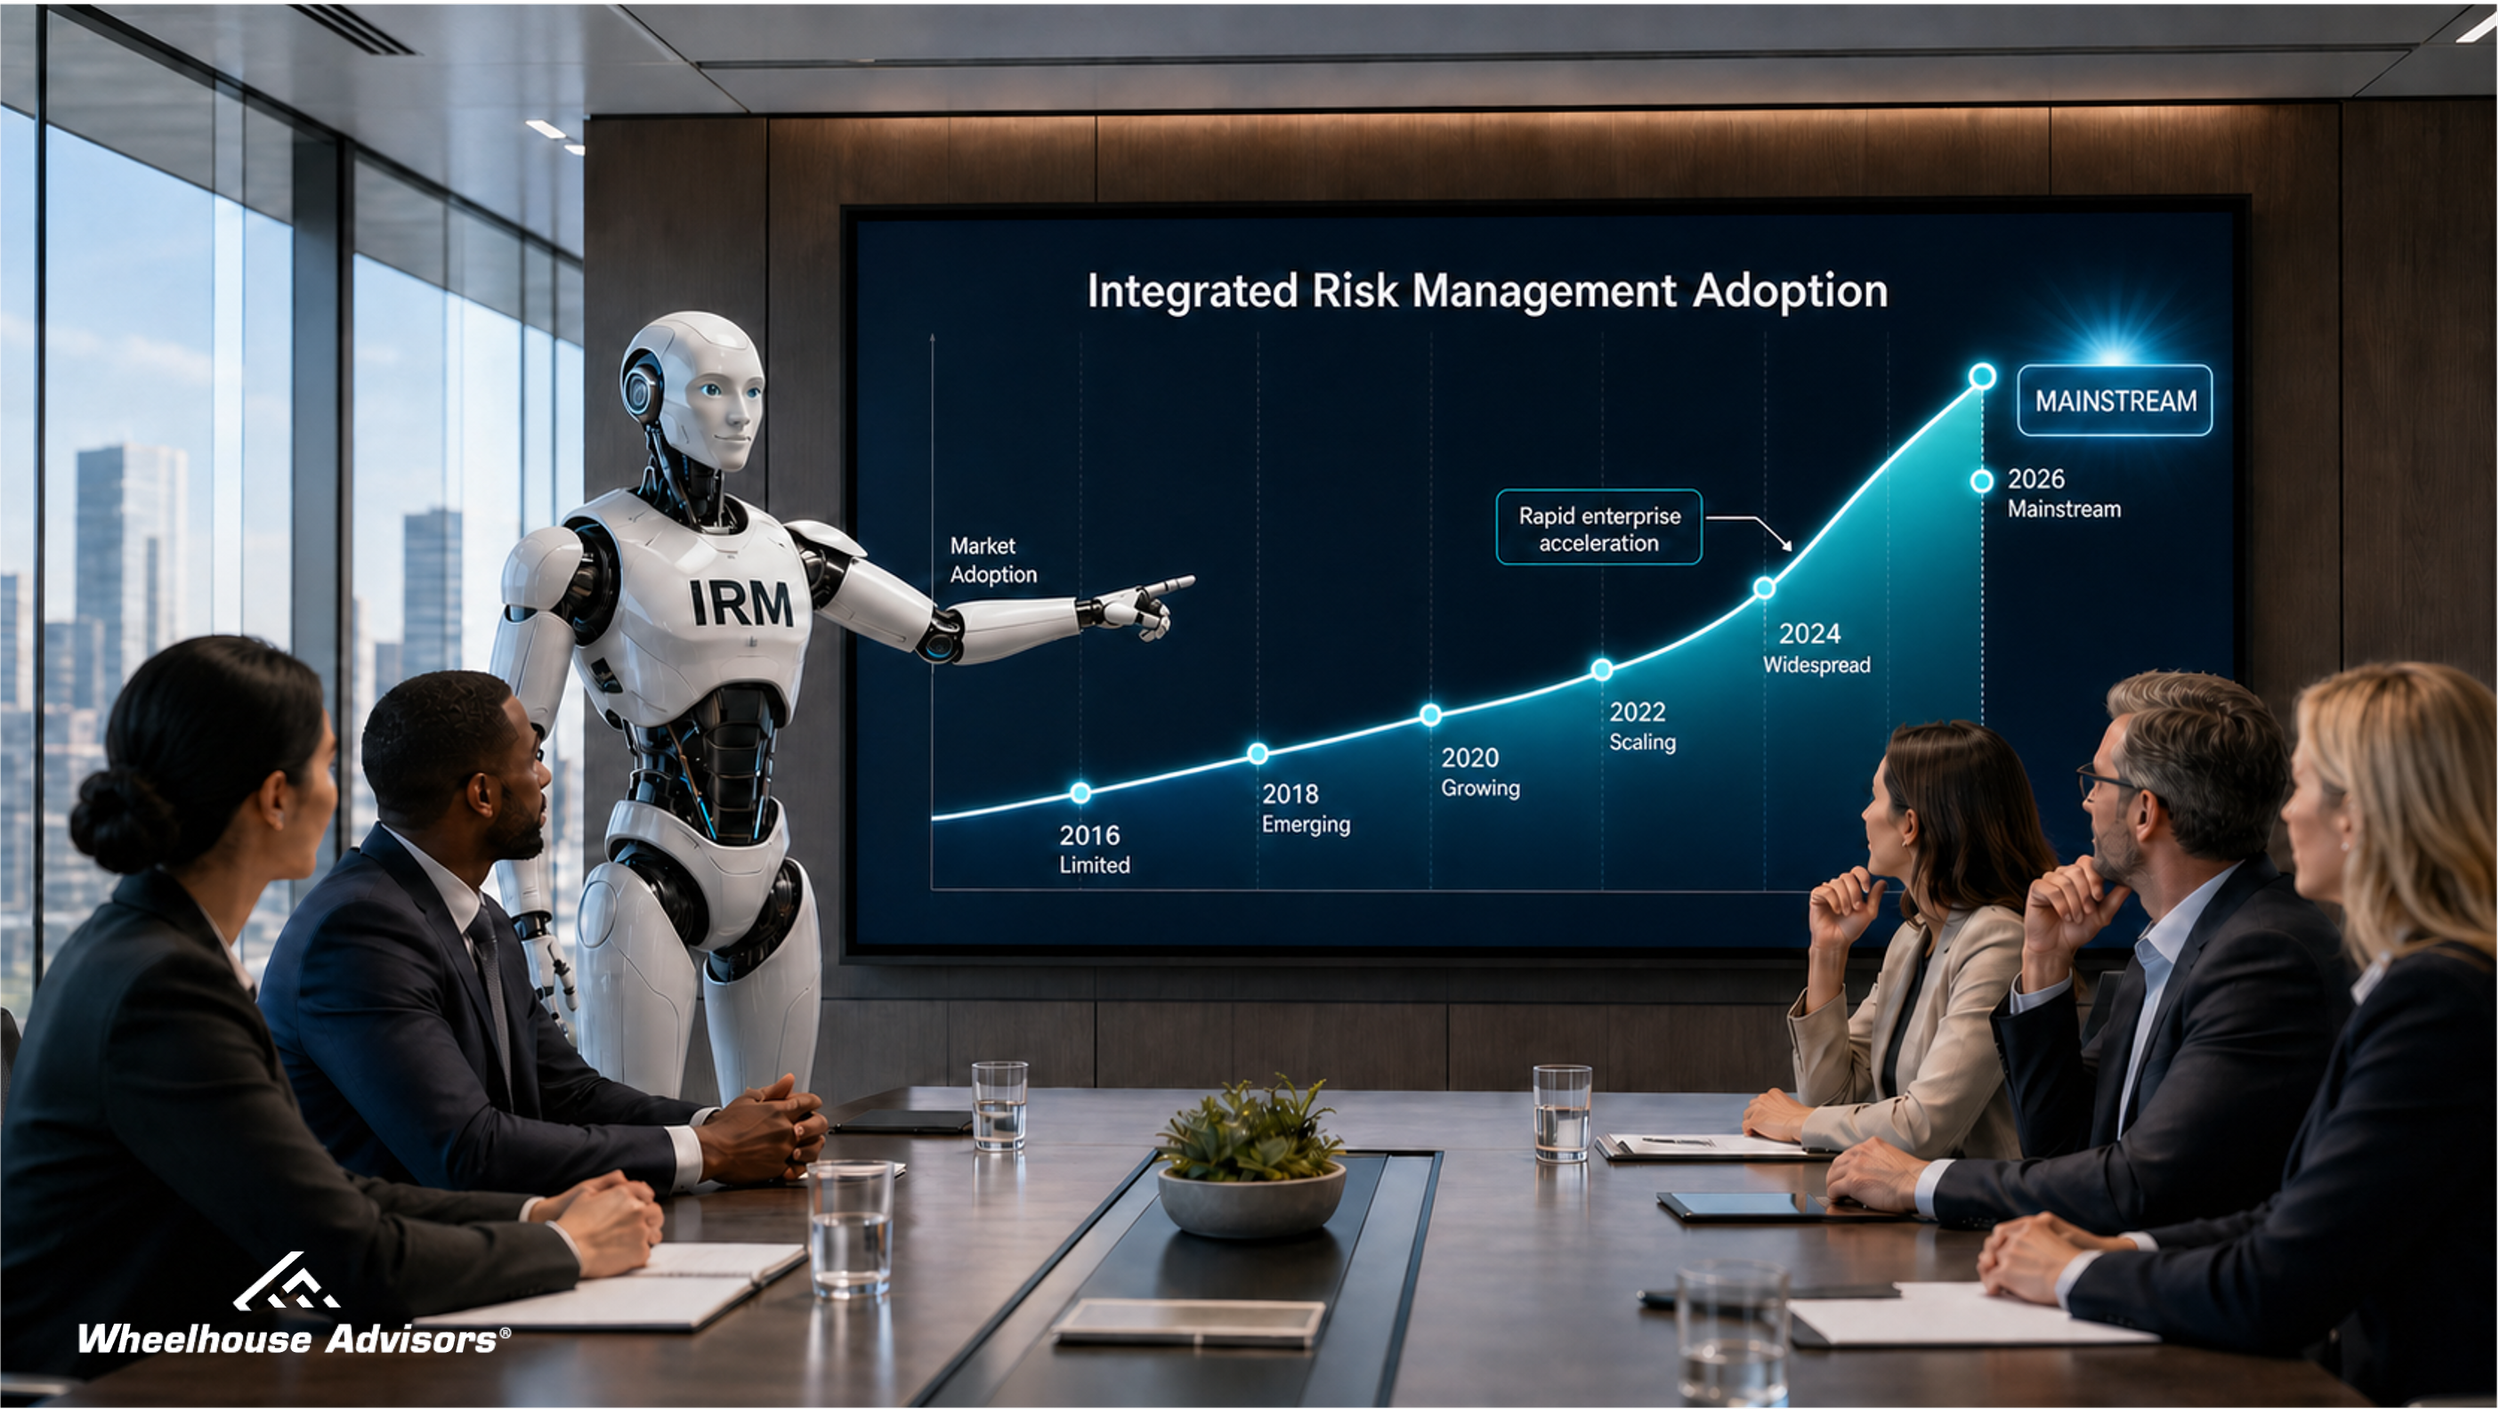
When Cyber Risk Becomes Enterprise Risk, Whose Job Did It Just Become?
Integrated risk management reached mainstream adoption this month. The discipline itself is not new. When the IRM category was defined in 2016, leading organizations were already managing cyber, technology, and operational risk as a single enterprise concern owned at the top. What was missing for the past decade was broad adoption. That gap is now closing in plain view. Rating agencies are pricing security governance into credit. Regulators are addressing corporate leaders directly rather than their security teams. And enterprise research now documents boards accepting accountability for exposures that used to live three levels down in a technology function.
Two publications captured the shift in the same week, without citing each other. On July 8, Cybersecurity Dive reported on new research from Information Services Group showing that U.S. enterprises are folding cyber risk into their overall enterprise risk strategy, with boards and C-suites taking direct accountability for business continuity, financial exposure, and regulatory compliance. One day later, Harvard Business Review published an argument that lands like a rebuttal to every executive hoping that accountability might live somewhere else: you can outsource the AI, but the risk stays with you.