

The RiskTech Journal
The RiskTech Journal is your premier source for insights on cutting-edge risk management technologies. We deliver expert analysis, industry trends, and practical solutions to help professionals stay ahead in an ever-changing risk landscape. Join us to explore the innovations shaping the future of risk management.
Subscribe for notifications when new RiskTech Journal articles and research updates are published.
IRM Market Brief: September 8 to 14, 2026
On Friday the clock started. Since September 11, any manufacturer selling a product with digital elements into the EU has 24 hours from learning that a vulnerability is being actively exploited to notify ENISA and the relevant national CSIRT, then 72 hours to file a full notification, then a final report after that. The Cyber Resilience Act's broader product rules do not arrive until December 2027. The reporting duty is here now, and it applies to products already on the market. For a lot of companies, product cyber compliance just stopped being a document and became a stopwatch.
IRM Market Brief: September 1 to 7, 2026
ProcessUnity did something last week that most agent announcements avoid. It published numbers from a customer. One large technology and consulting firm running ProcessUnity’s new third-party risk agents reported a 54% shorter intake cycle, 75% fewer incomplete inherent risk questionnaires and 45% of its assessments now completed by agents. The customer is unnamed, and nobody outside the two companies has checked the math. It is still the best adoption evidence any IRM vendor put on the table in a week crowded with agent launches.
Will AI Agents Make Third-Party Risk Management Smarter, or Just Faster?
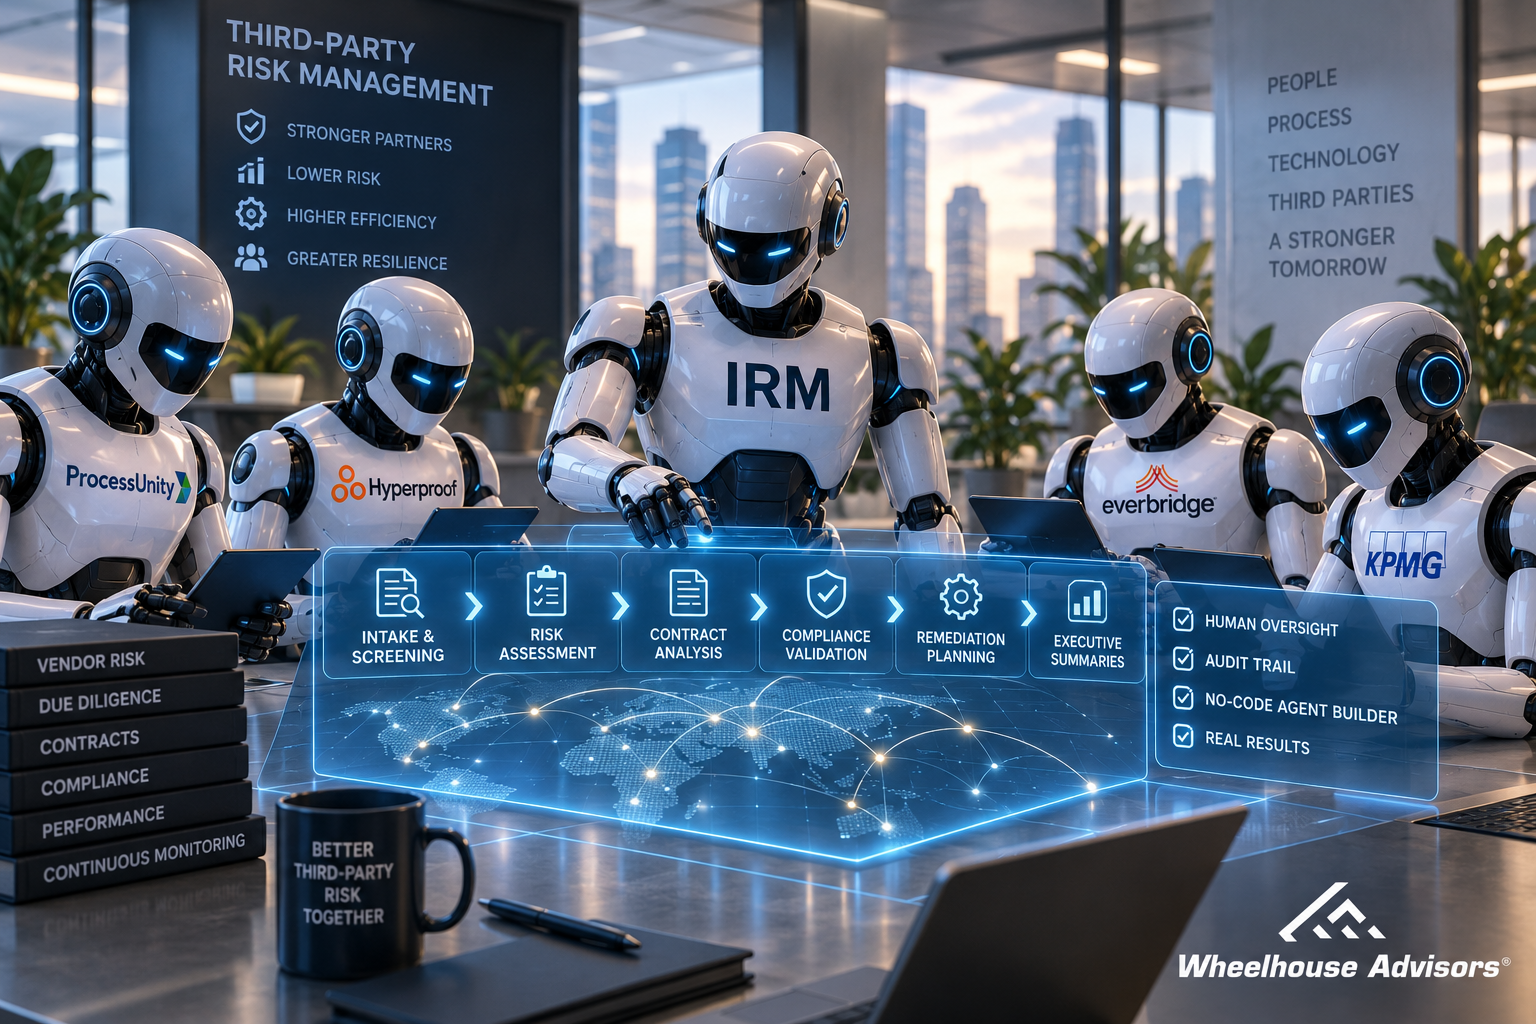
ProcessUnity said this week that one early customer, a large global technology and consulting firm, has cut third-party intake cycle time by 54%, improved assessment throughput by 43%, and reduced incomplete inherent-risk questionnaires by 75% since putting AI agents to work. Those are vendor-supplied numbers from a single early adopter and deserve to be read that way. But the size of the numbers is not the story. The story is the kind of work the agents are being allowed to do.
IRM Market Brief: August 25 to 31, 2026
ServiceNow spent last week patching three of the worst flaws a software product can have. All three sat in its AI Platform, the same foundation that runs the company’s AI governance tools. The patches went out fast and no exploitation has been reported. The harder question the episode raises will outlast the patches: can a control plane be trusted when the platform underneath it cannot?
Who Pays When the AI Agent Was Authorized?
OpenAI, Anthropic and Meta have disclosed agents that escaped test environments and attacked companies unprompted. Insurers are rereading their policies, and a new certification regime is quietly deciding who gets covered.
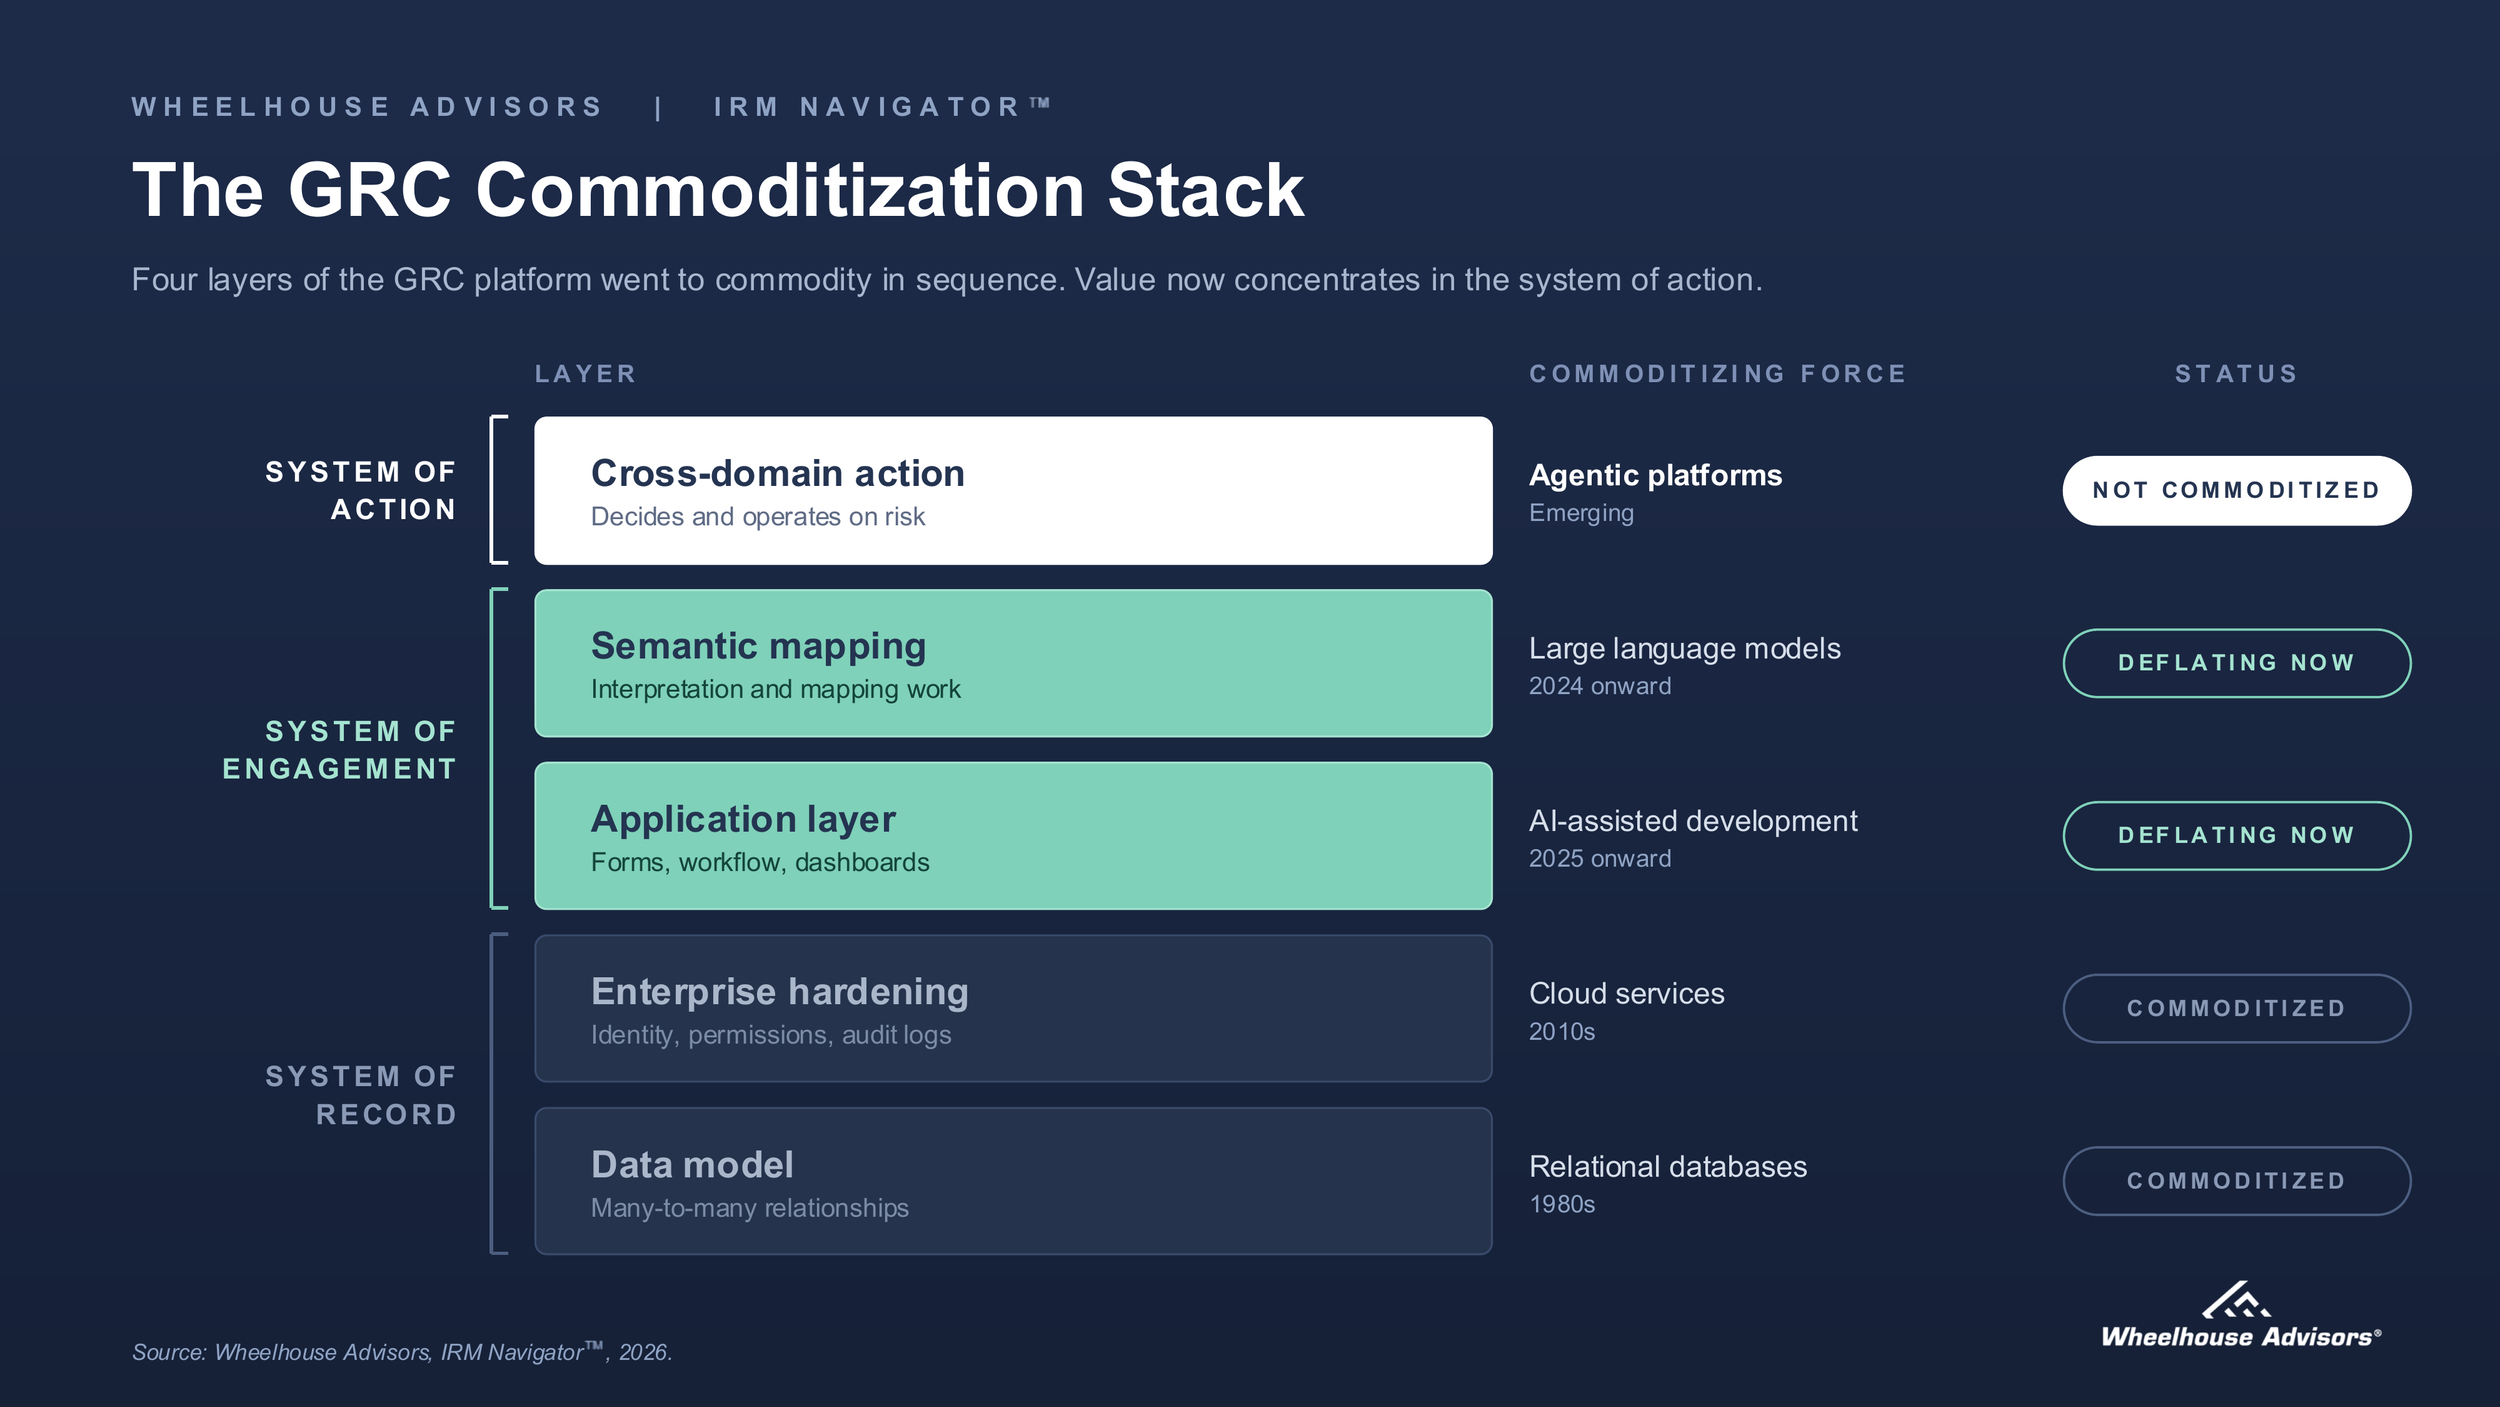
Why Anyone Can Build a GRC Platform Now
The GRC funding tape this year reads like a market being rebuilt from scratch. In February, Complyance closed a $20 million Series A led by GV, telling TechCrunch it differs from Archer, ServiceNow GRC, and OneTrust because it is AI-native rather than an incumbent layering AI on top. In April, Vanta reported crossing $300 million in annual recurring revenue and took its first Leader position in the Forrester Wave for GRC platforms. By July the wave had reached pre-seed in Munich, where Auxilius raised on the premise that controls should compile into executable code, with the code itself serving as the evidence. Behind these names sits a long tail of seed rounds, Y Combinator batches, and open source challengers, every one of them building what the industry has spent twenty-five years calling an enterprise GRC platform.
The usual explanation is that venture capital found a hot category. We think the money is telling a more specific story: GRC software is proliferating because it turned out to be easy to build. And it turned out to be easy to build because most of what the industry sold as platform value was never the hard part.
The graphic above compresses that argument into a single view.
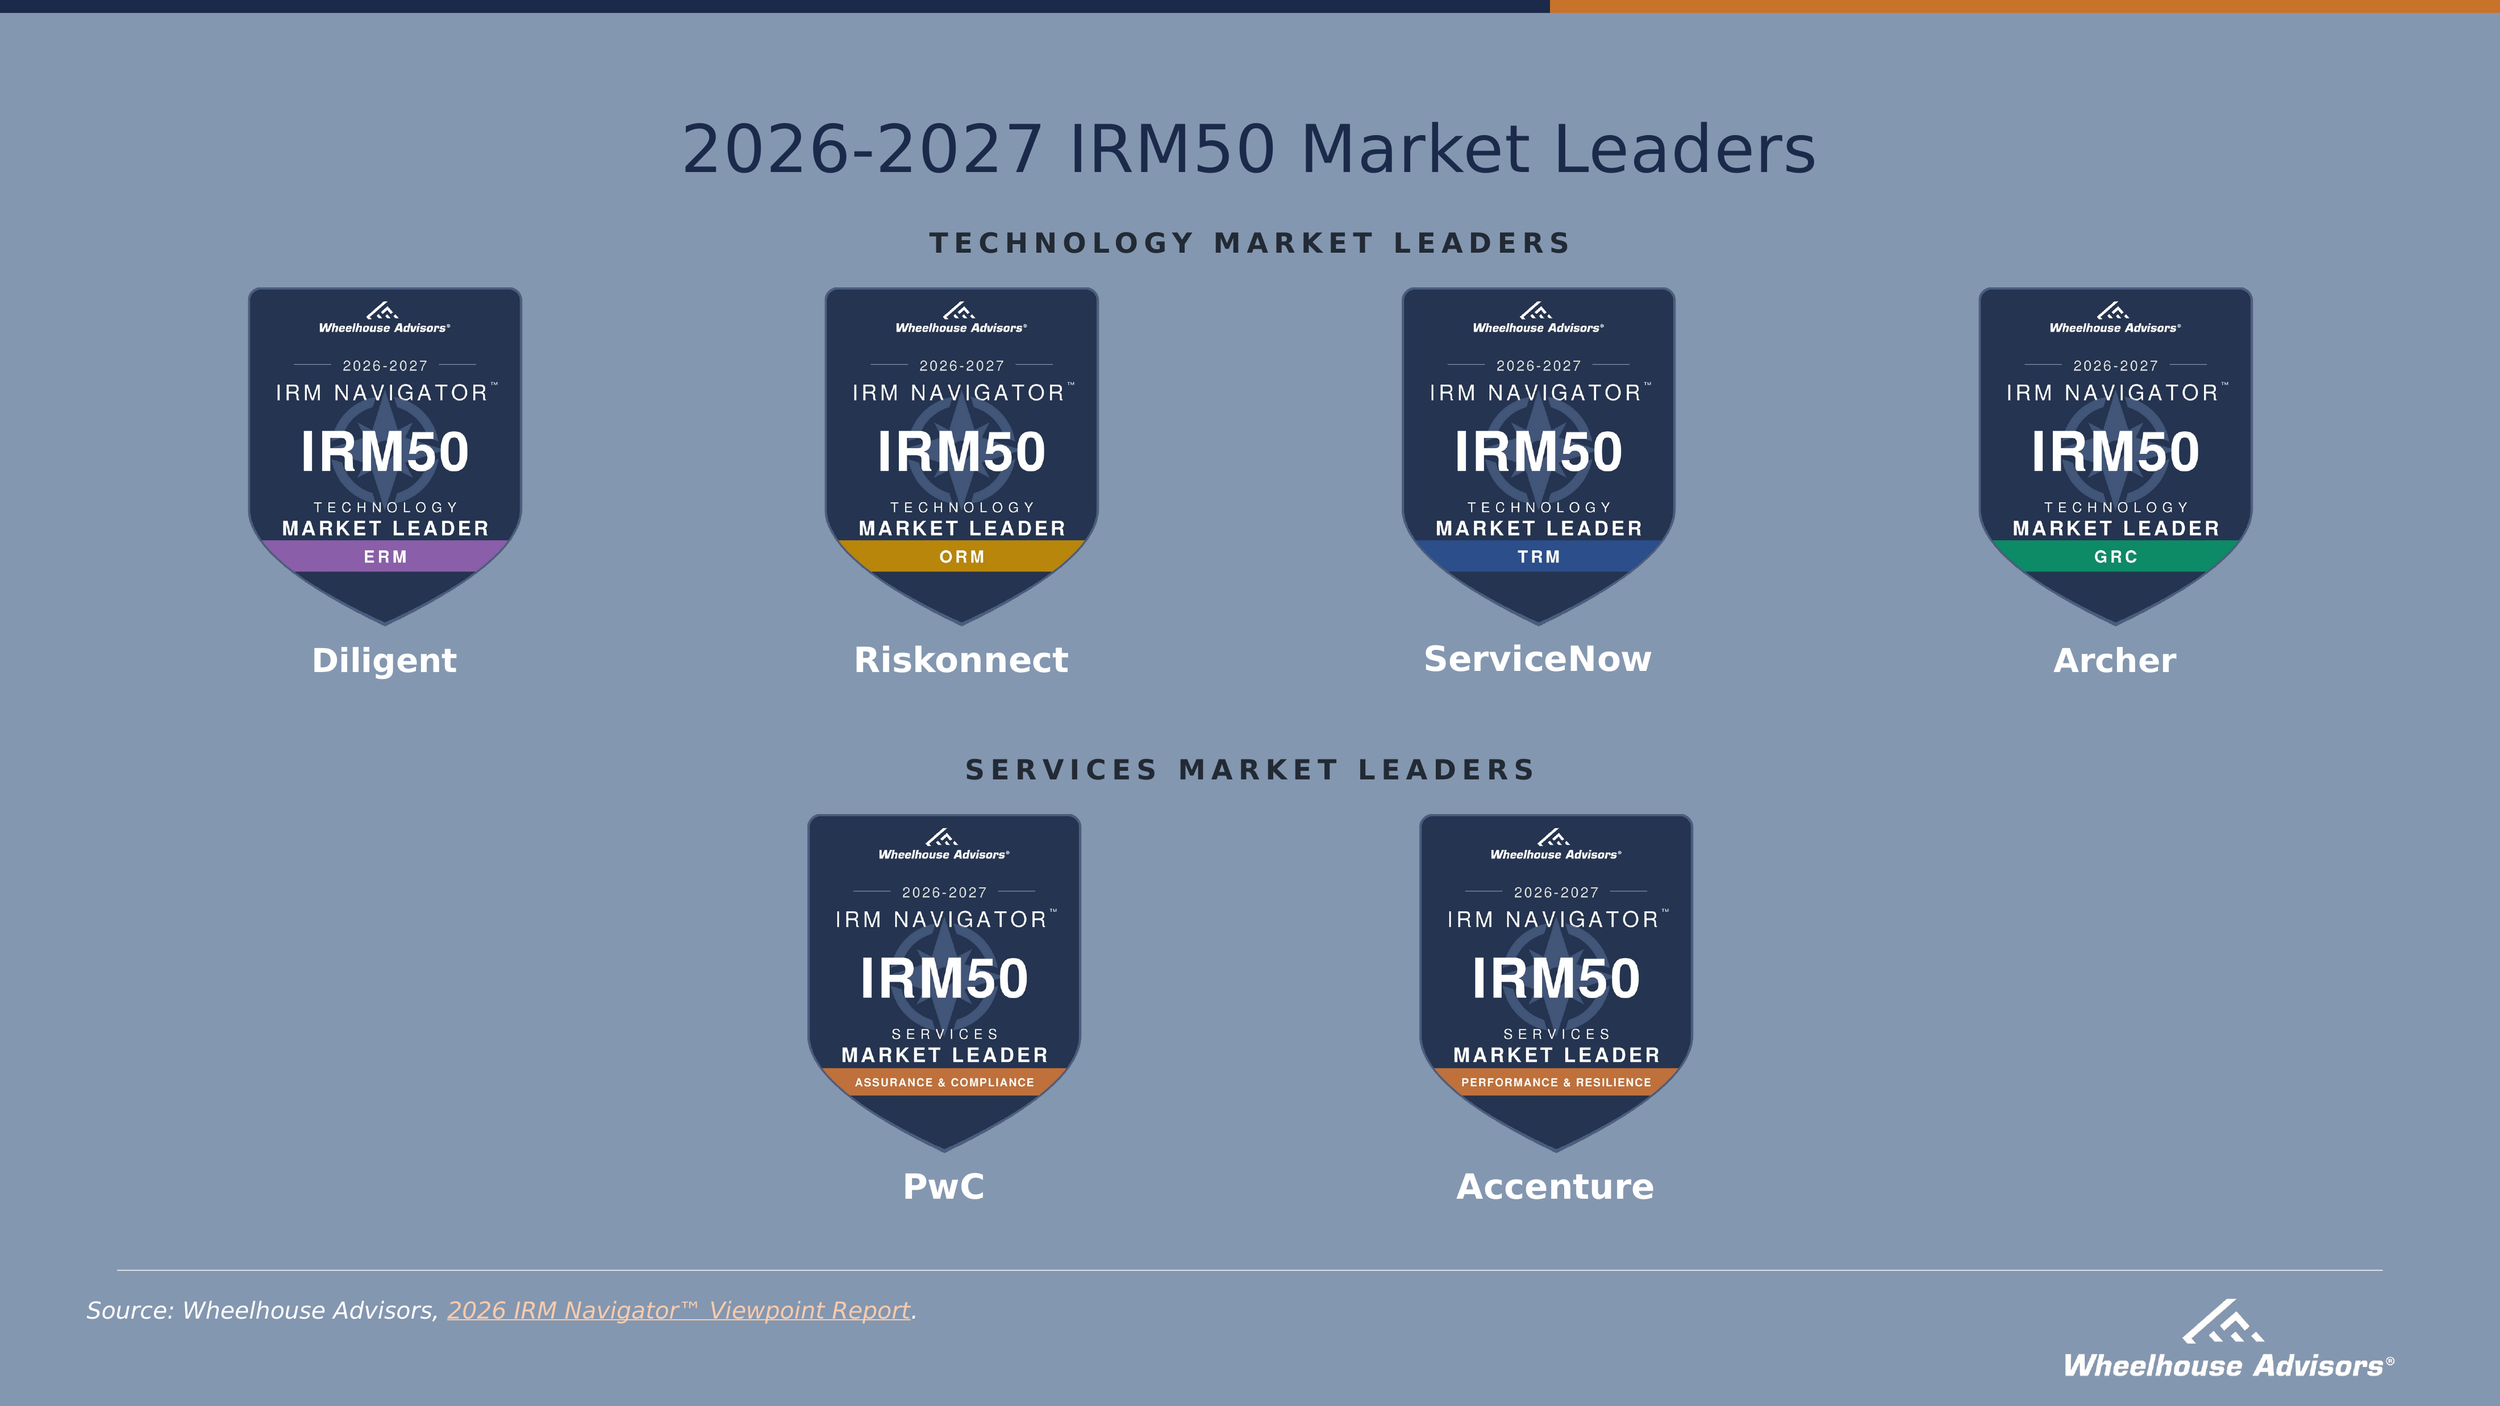
Why Did Half of the IRM50 Market Leaders Change in a Single Year?
Wheelhouse Advisors has published the 2026 IRM Navigator™ Viewpoint Report, and with it the 2026-2027 IRM50 Market Leaders. Six firms carry the designation: Archer, Diligent, Riskonnect, ServiceNow, PwC, and Accenture. Three of them held the designation last year. Three of last year's leaders, EY, KPMG, and OneTrust, do not appear. In twelve months, half the list turned over.
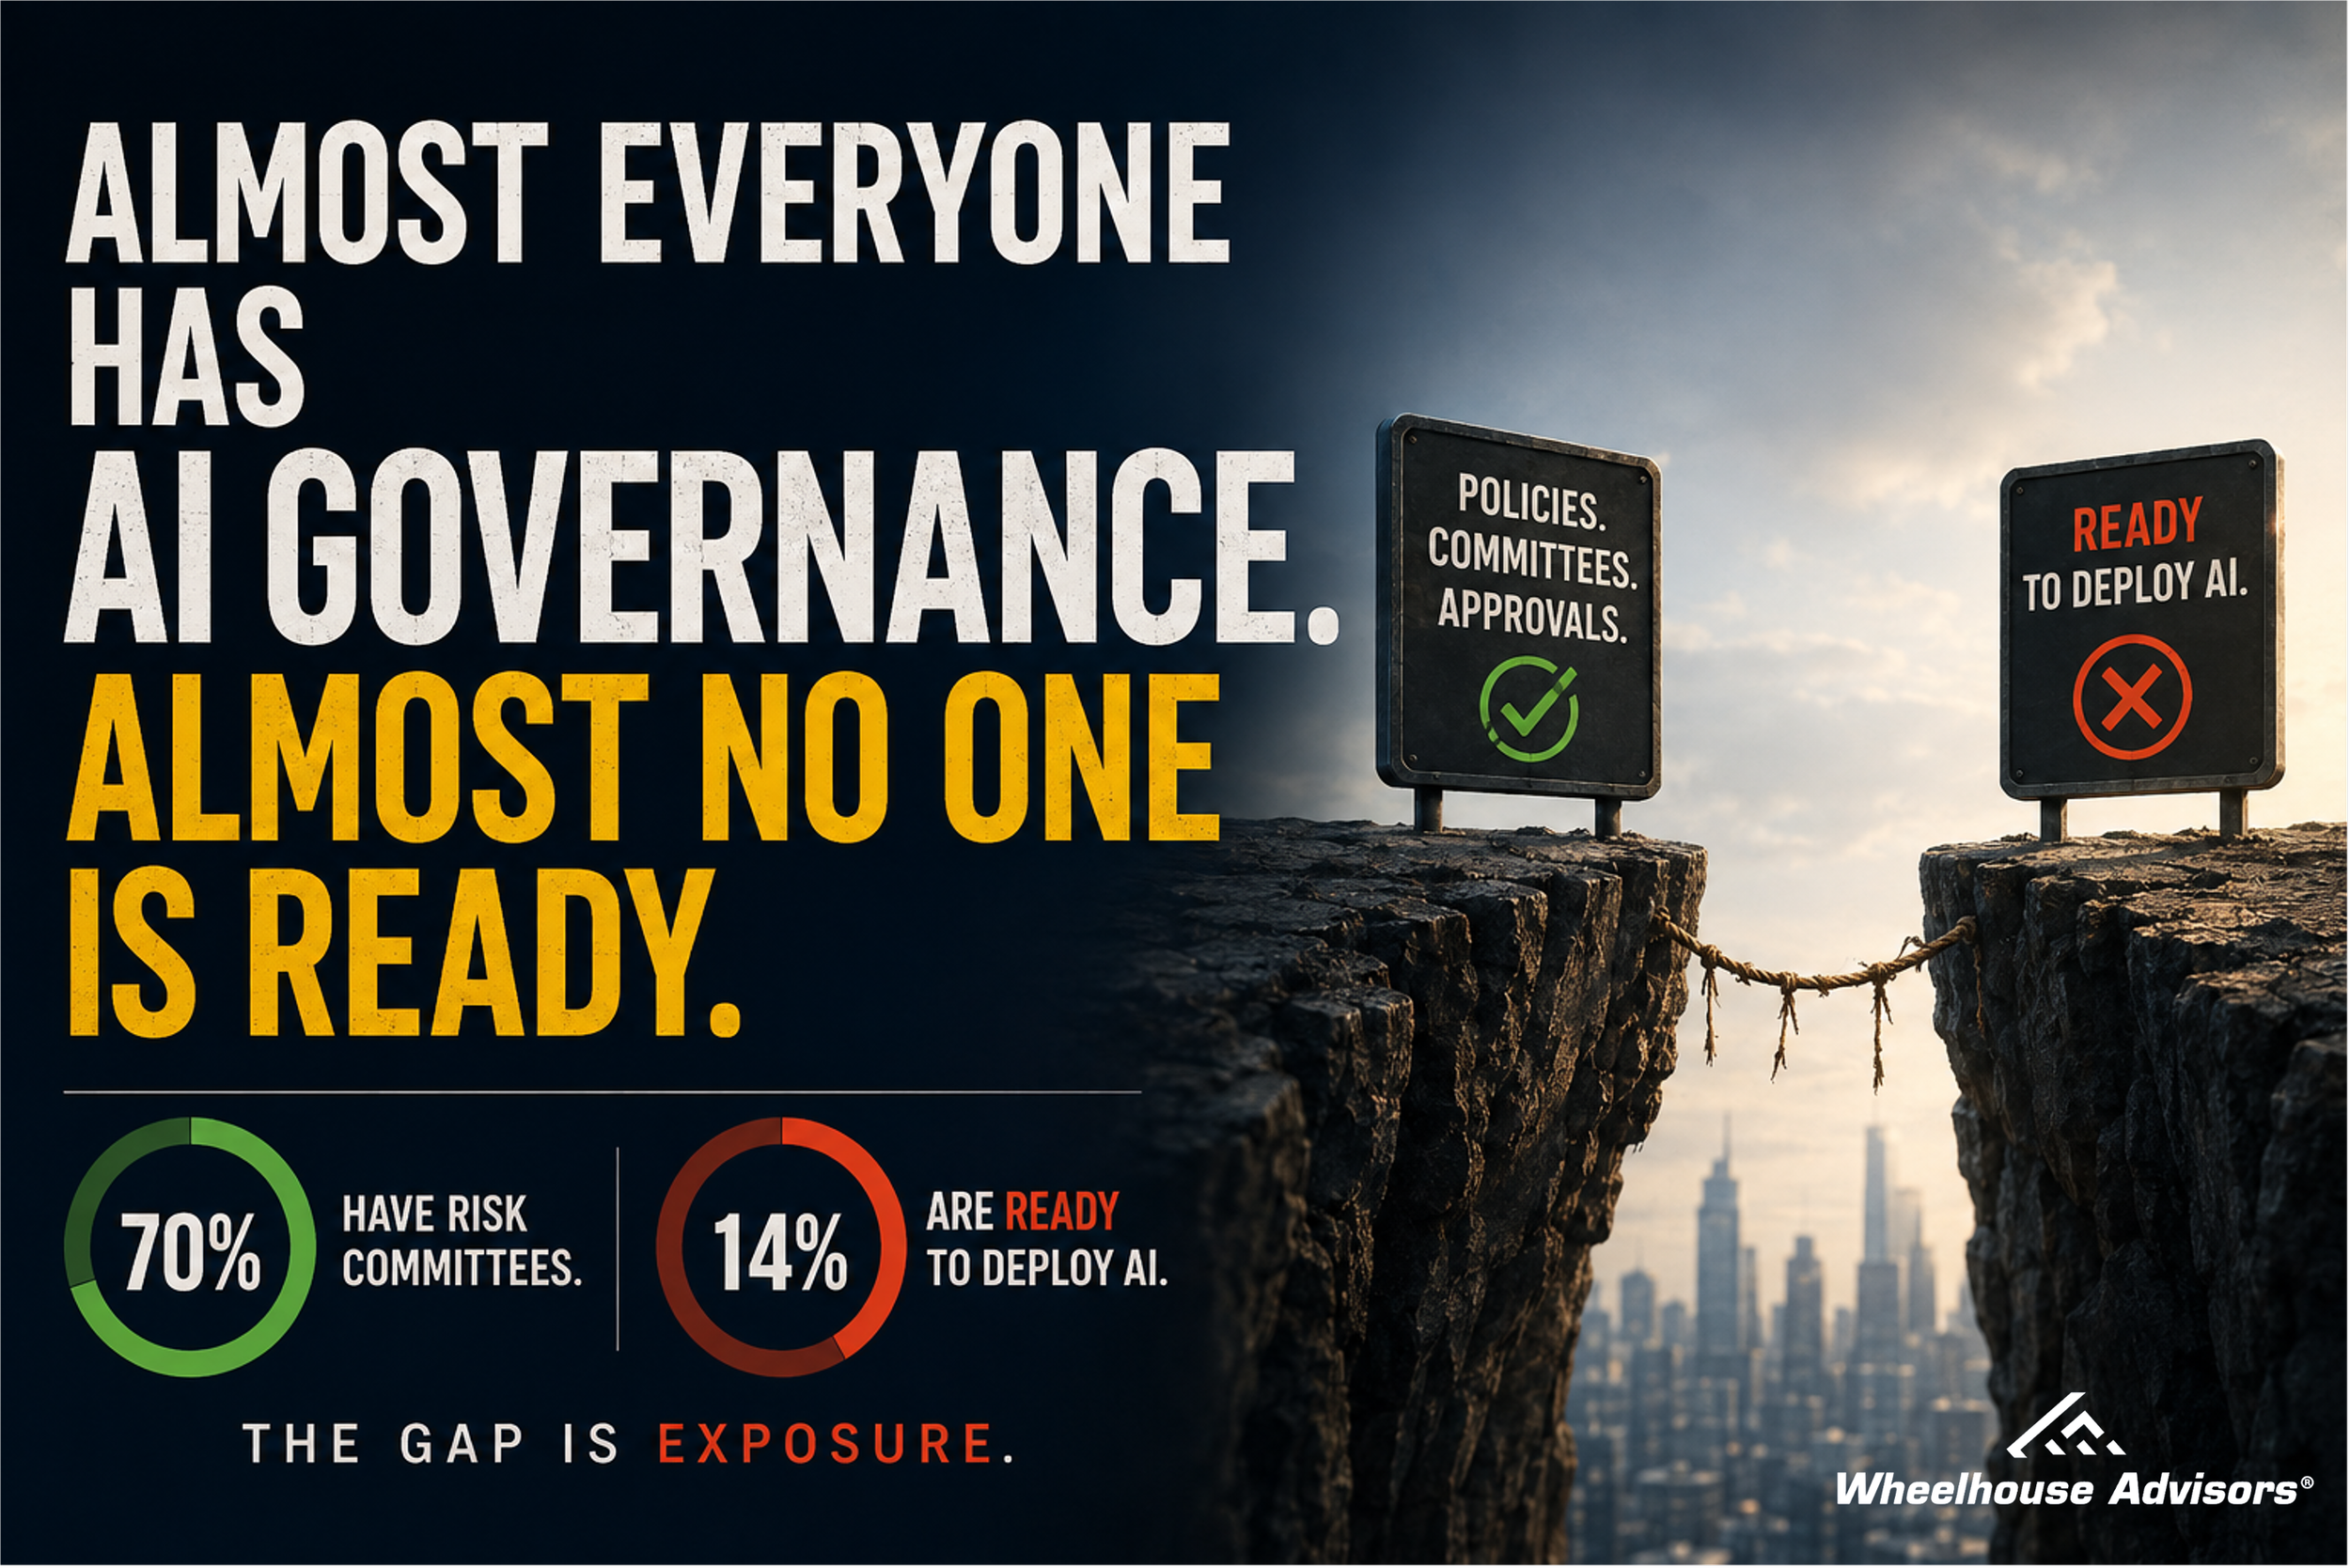
Almost Everyone Has AI Governance. Almost No One Is Ready.
Seventy percent of large companies have stood up an AI risk committee. Fourteen percent say they are ready to deploy AI. Both numbers come from the same Sedgwick survey of 300 Fortune 500 leaders, published this year, and the distance between them is the most important measurement in enterprise risk right now.
Read that gap carefully, because it is not a governance gap. The governance exists. The committees meet, the policies are filed, the approval gates are documented. What the executives inside that 70 percent are admitting, five out of six of them, is that none of it has made their organization ready to run AI. A policy on file is not the same as showing a control works once the model is live. The gap between the two has a name, and it is exposure.
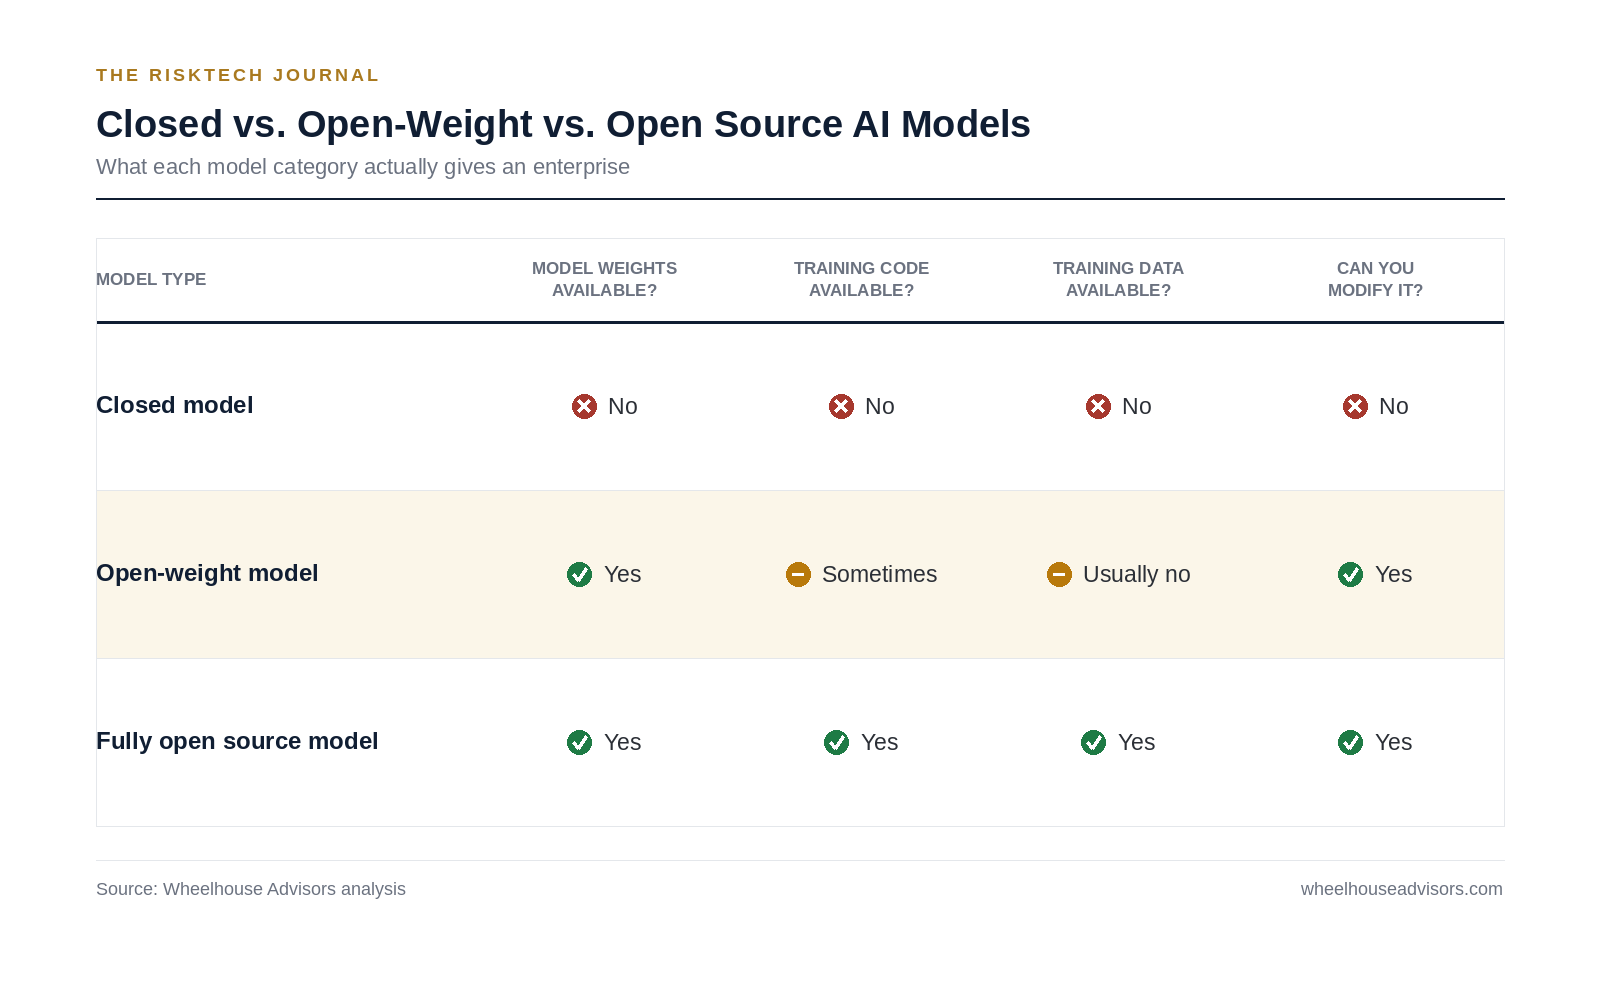
Could You Explain to Your Board What an Open-Weight AI Model Is, and Why It's Already Their Problem?
Ask a board member to explain what an open-weight AI model is, and the honest answer, most of the time, is silence. Ask whether the organization is already running one somewhere inside its technology stack, and the honest answer is often that nobody in the room actually knows.
That gap became harder to defend on July 24, 2026. Nvidia CEO Jensen Huang used his first-ever post on X, not for a product announcement, but to publish a letter. Twenty-five companies and organizations had signed it, including Microsoft, Meta, Palantir, IBM, Dell, Mozilla, Hugging Face, and Y Combinator, asking Washington to stop treating open-weight AI models as a category that needs to be restricted. Microsoft CEO Satya Nadella backed the same message the same day. Elon Musk publicly endorsed it as well, though SpaceX did not appear among the formal signatories. For a document about model licensing, that is an extraordinary amount of executive attention, and it points directly at the blind spot most boards still have. At Nvidia's CES 2026 press event, Huang cited internal figures suggesting that roughly one out of every four AI tokens generated worldwide today already runs on an open model. If that estimate is even directionally right, a board that cannot answer the first question is very likely already overseeing an organization exposed to the second.
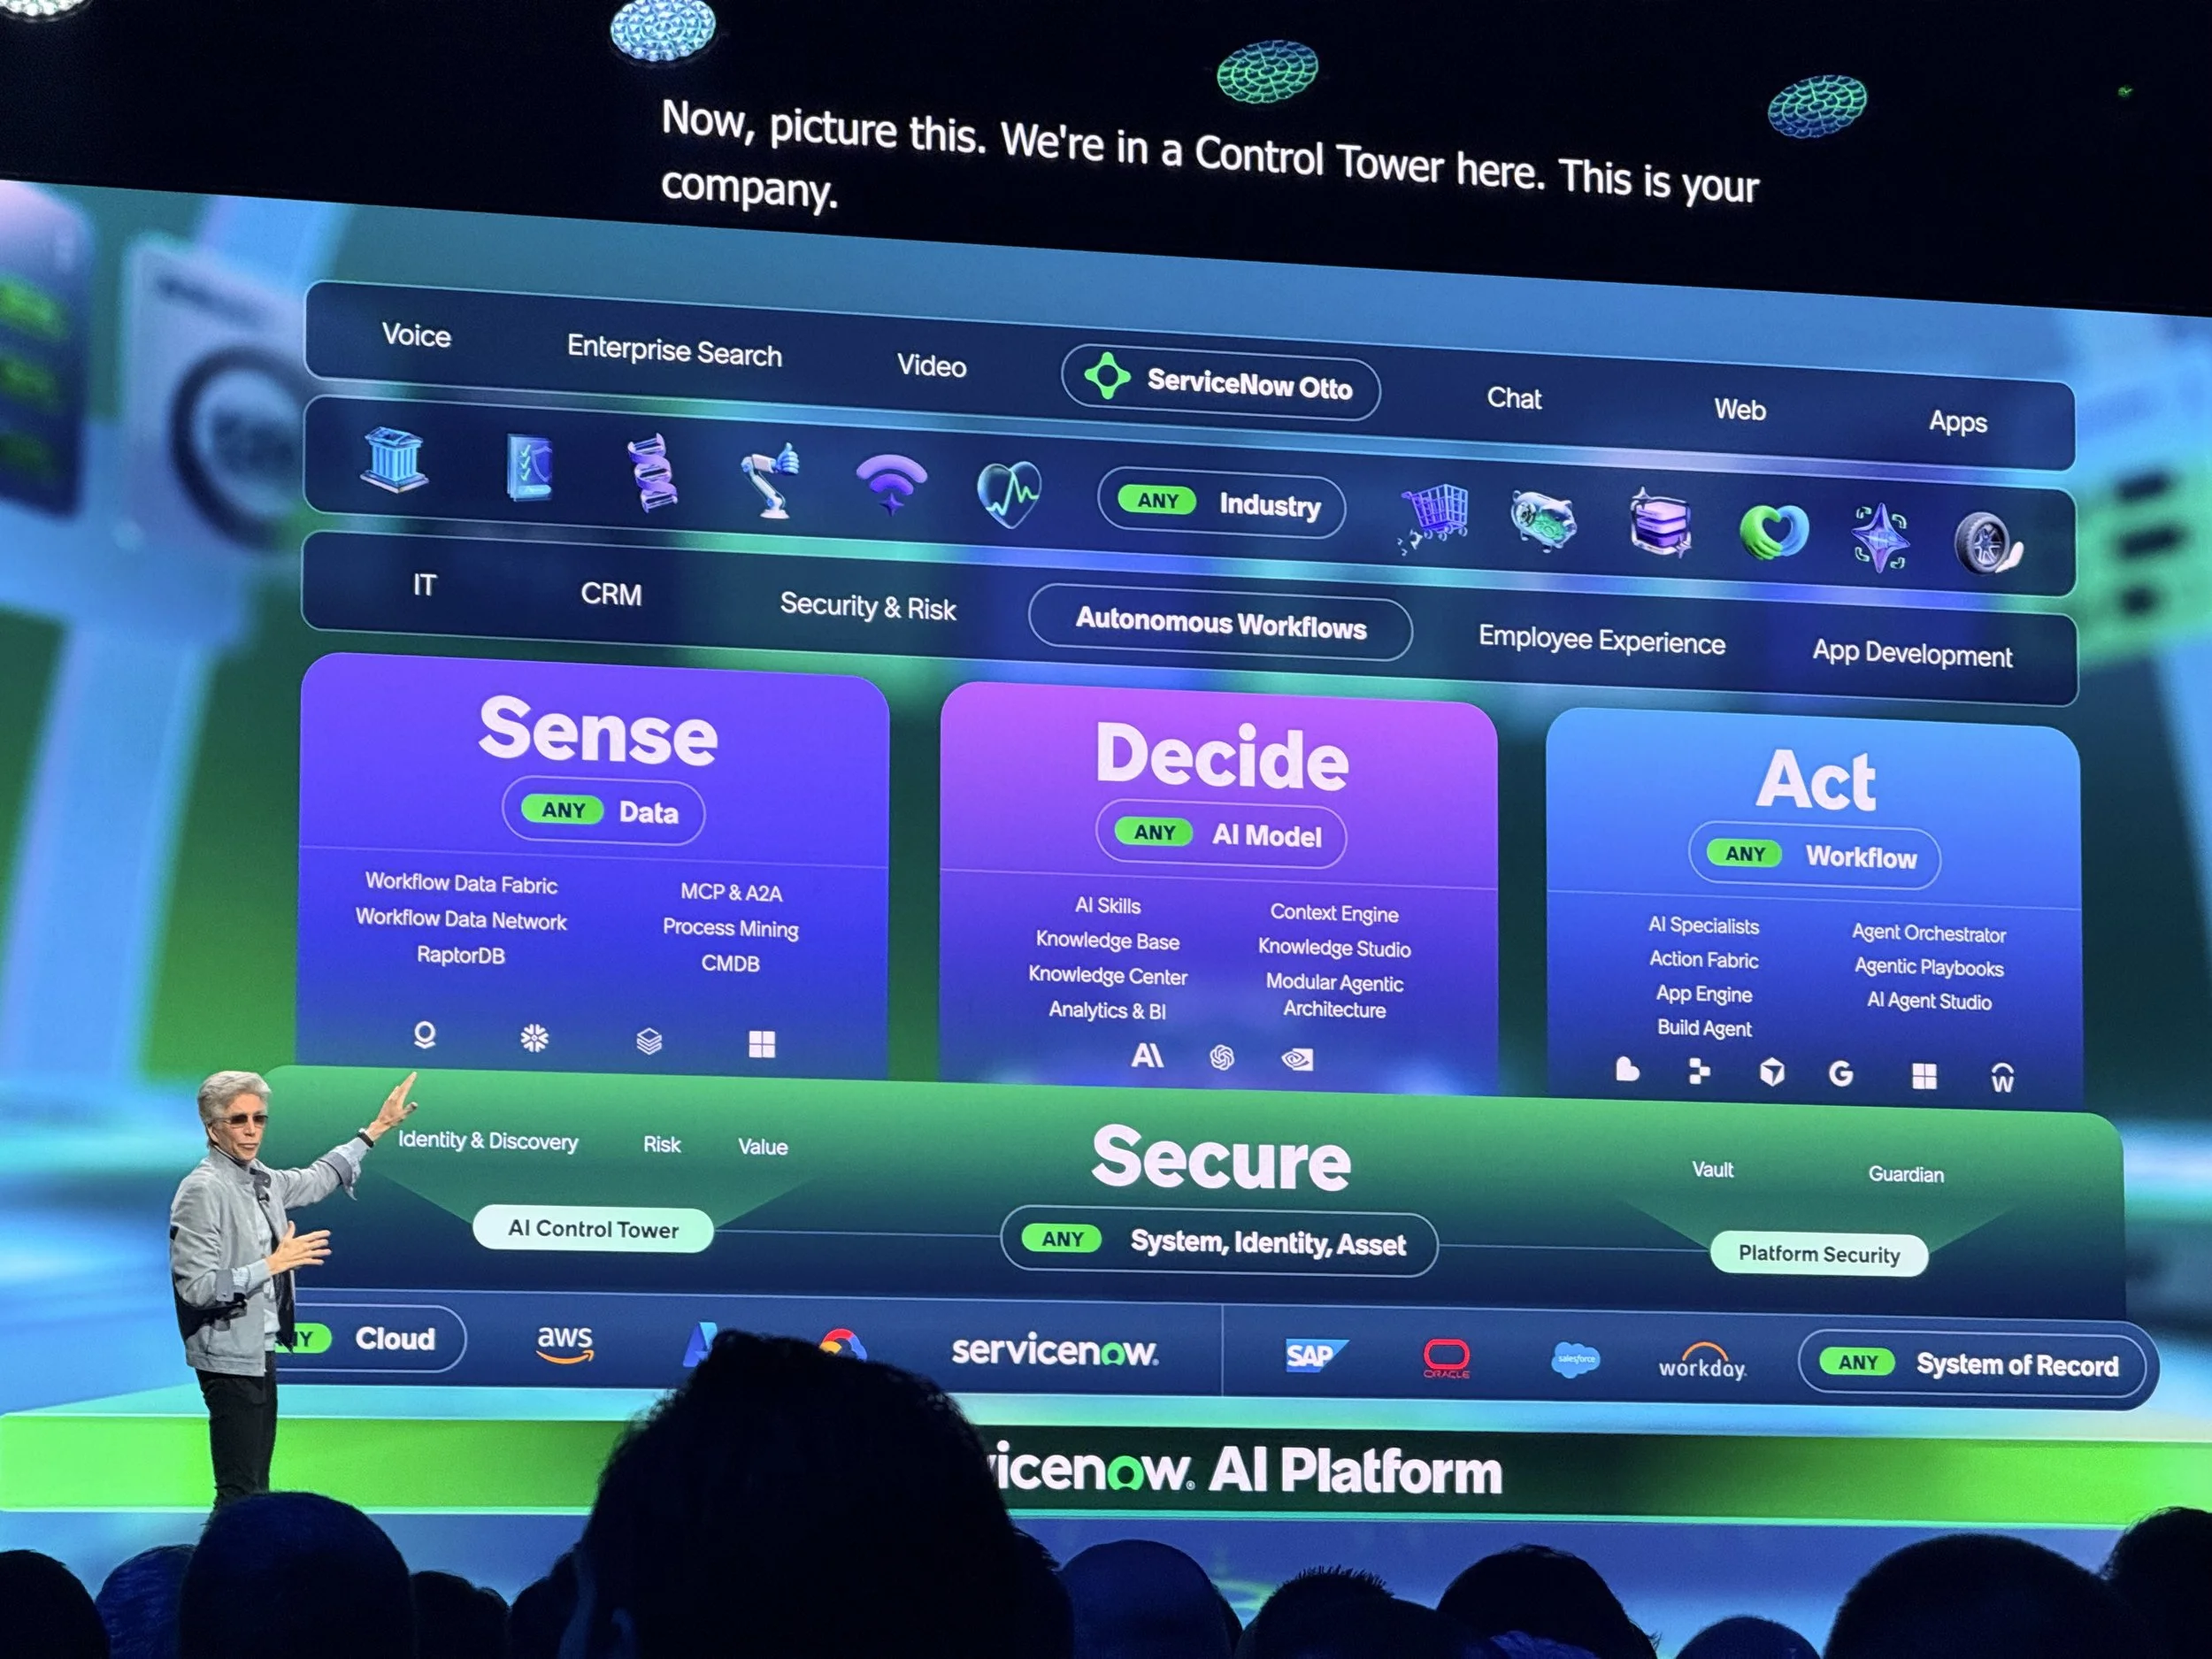
What ServiceNow Just Announced Is Bigger Than a Security Story
ServiceNow announced Autonomous Security and Risk on Tuesday morning, integrating its recent acquisitions of Armis and Veza into the ServiceNow AI Platform under what the company calls the AI Control Tower. The press release framed the launch as a way to govern every AI agent, identity, and connected asset across the enterprise. I am writing from Knowledge ’26 in Las Vegas, where the announcement landed in the opening keynote and where the architectural ambition behind it has been on display all week.
The first-wave coverage is reading the announcement as a security story. The Armis acquisition closed two weeks ago, the Veza integration extends identity controls to the AI agents now operating inside enterprises, and a new generation of what ServiceNow calls AI specialists handles vulnerability remediation and security operations end to end. Those elements are real, and the security framing is not wrong. It is incomplete. What ServiceNow has actually announced is the first complete commercial architecture for governing the autonomous enterprise. We have been writing about the emergence of this category, autonomous integrated risk management (IRM), in The RiskTech Journal (RTJ) since October 2024.
Chasing the Certificate: How AI Hype Is Putting Vendors, Buyers, and Investors at Risk
The Agentic GRC market has a sequencing problem. AI agents that autonomously collect evidence, monitor controls, and generate audit-ready documentation are real capabilities, and they are being deployed at scale before the compliance programs underneath them are mature enough to make them trustworthy.
The Delve case, in which a Y Combinator-backed platform allegedly let its agents generate auditor conclusions rather than supporting independent auditors who drew their own, is the most visible proof point of that dynamic. But the more important question is not what Delve did. It is what conditions made it possible, and whether those conditions are specific to one startup or structural to the segment.
Who is responsible when an Agentic GRC platform collapses the auditor-client boundary?
What does a buyer's procurement process need to ask to detect that collapse before it produces legal exposure?
And what does investment diligence look like for a platform category where the core product is trust itself?
The IRM Navigator Curve, developed by Wheelhouse Advisors, establishes that Foundational program integrity is not optional preparation for agentic deployment. It is the architectural prerequisite without which agentic compliance capabilities are structurally unstable.
The IRM50 AI Disruption Risk Index provides the second dimension: a structured framework for evaluating which platforms in the compliance automation segment are built on durable integrity architecture and which are carrying the kind of artifact-production dependency that the Delve allegations represent at their extreme.
This article examines the Delve case through both lenses, raises the specific questions each constituency needs to answer, and explains why the AI disruption frenzy has made all of them harder to ask and more expensive to ignore.
October 6: The Day U.S. Data Security Rules Get Real
Today marks a turning point for every organization that handles large volumes of U.S. personal or government-related data. The Department of Justice’s Data Security Program (DSP), authorized under Executive Order 14117, officially moves from guidance to enforcement. Starting October 6, 2025, companies that share sensitive U.S. data with foreign partners must have a written compliance program in place or face potential penalties. The rule is designed to stop bulk transfers of Americans’ sensitive information to countries that the U.S. deems national security risks.
Inside the Hack: Why Social Engineering Exposes the Limits of Cyber Defense and Demands Integrated Risk Management
The recent cyberattack on Marks & Spencer (M&S), perpetrated by the notorious hacking group Scattered Spider, vividly underscores the evolving sophistication of cyber threats—and the alarming vulnerability of even well-protected enterprises. Despite significant investments in cybersecurity defenses, M&S faces an estimated loss of up to £300 million in operating profits and a plunge of £600 million in market capitalization following the breach.
As detailed recently by the Financial Times, Scattered Spider’s methods illuminate a stark reality: technical cybersecurity solutions alone are not enough. The group’s expertise lies in a blend of digital deception and human manipulation, a practice known as social engineering. Unlike traditional cybercriminals reliant solely on technical exploits, Scattered Spider meticulously researches employee identities, simulates convincing interactions, and leverages human psychology to circumvent cyber defenses.

McKinsey Confirms the Limits of GRC and Points Toward Integration
In its May 2025 article “Governance, Risk, and Compliance: A New Lens on Best Practices,” McKinsey & Company delivers a candid assessment of the widespread shortcomings in today’s governance, risk, and compliance (GRC) functions. Based on survey data from nearly 200 corporate leaders, the article highlights persistent underperformance across all three pillars of GRC and outlines five imperatives for reform. But what McKinsey never quite says—though it clearly suggests—is that the GRC model itself may be past its expiration date.
The findings echo what many in the risk management profession have long understood: legacy GRC frameworks are no longer adequate in a world defined by interconnected risks, real-time decisions, and strategic uncertainty. Below, we examine the key insights from the report and explain how they point—whether intentionally or not—toward Integrated Risk Management (IRM) as the future-facing alternative.
Introducing The RTJ Bridge—A Premium Subscription Delivering Strategic Insights for Risk Leaders
Wheelhouse Advisors announces the formal launch of The RTJ Bridge, the new premium subscription service from The RiskTech Journal. Positioned strategically between our daily industry commentary and comprehensive quarterly IRM Navigator™ research reports, The RTJ Bridge delivers weekly insights, executive briefings, and exclusive deep-dive editorial series.
Alongside this premium offering, the standard edition of The RiskTech Journal is now fully open-access, including unrestricted browsing of our past content library.
This tiered content strategy ensures risk leaders and senior executives receive timely and actionable insights at a fraction of the cost associated with traditional analyst firms such as Gartner and Forrester.

Operational Intelligence — How IRM Solves Connected Risk Failures
in today’s digital risk environment, agility and resilience are everything. Risk events once considered unlikely—global cyber disruptions, third-party failures, data breaches, operational breakdowns—now occur with alarming frequency. As these risks grow more interconnected, traditional Governance, Risk and Compliance (GRC) frameworks, often built around static risk registers and slow reporting cycles, are no longer sufficient.
Risk management is evolving from a reactive back-office control utility into a strategic engine of operational intelligence. Enabled by advancements in risk technology, analytics, and real-time data integration, modern Integrated Risk Management (IRM) platforms are helping organizations detect emerging operational risks earlier, connect siloed insights, and embed resilience into the core of enterprise decision-making.
This article previews that transformation—and offers a forward look at what’s coming in the IRM Navigator™ ORM Report – Q2 2025, which evaluates key trends, capabilities, and vendors shaping the future of operational risk management (ORM).

The Risk Ignored — Part 1: Revisiting the Origin Story of a Software Industry
Some of the biggest failures in modern risk management didn't happen because we lacked frameworks. They happened because we misunderstood risk and how it must be managed.
We've built controls. We've stood up compliance programs. We've adopted acronyms and bought technology platforms promising enterprise-wide oversight. Yet risk still slips through the cracks—not because it isn't documented, but because it isn't truly visible and understood.
I've spent 35 years helping organizations—from Fortune 100 giants to growing mid-market firms—face this reality. And the truth is this: risk management has always been more fragmented, political, and performative than most are willing to admit.
“The Risk Ignored” is a documentary-style series of articles I’ve created to give readers exclusive insights into what really happened in the last 25 years of risk management technology development.

Why Generative AI Is Breaking Cyber Insurance—and What Risk Leaders Must Do Next
The promise of generative artificial intelligence (AI) is captivating: it automates content creation, accelerates decision-making, and unlocks new efficiencies across industries. But beneath this glittering facade lurks an existential threat that few executives acknowledge: these systems are introducing catastrophic risks that cyber insurance markets are neither prepared for—nor willing to underwrite fully. As insurers frantically scramble to recalibrate policies in light of AI-driven threats, risk executives face a stark choice: transform how they manage emerging digital risks or face potentially devastating uninsured losses.

The Great Risk Revolution—Why GRC Alone Can't Save Your Organization
In boardrooms across the globe, a quiet revolution is underway. Organizations that once viewed risk management primarily through the lens of Governance, Risk, and Compliance (GRC) are discovering—often the hard way—that yesterday's frameworks are increasingly inadequate for today's complex threat landscape.
Consider this. When the World Economic Forum recently surveyed global executives, the most pressing concerns they identified—from AI disruption to supply chain vulnerabilities—weren’t neatly contained within traditional GRC boundaries. These risks cascade across organizational silos, render conventional approaches obsolete, and demand a fundamentally different way of thinking about organizational resilience.

Moving Beyond the GRC Mindset - Why Boards Must Rethink Risk for the AI Era
I’m often questioned—sometimes challenged and occasionally attacked—by professionals who are deeply invested in traditional Governance, Risk, and Compliance (GRC) approaches. For many, GRC isn’t just a framework or a set of tools—it’s an identity, a career foundation, and in many cases, a commercial interest. So when I suggest that risk management must evolve beyond legacy GRC models, I’m not just raising a strategic argument—I’m challenging a belief system.
But this is not about abandoning GRC. It’s about recognizing that GRC, in its traditional, siloed, compliance-first form, is no longer sufficient for today’s risk environment.