S8E5: The New Rules of Autonomous Risk
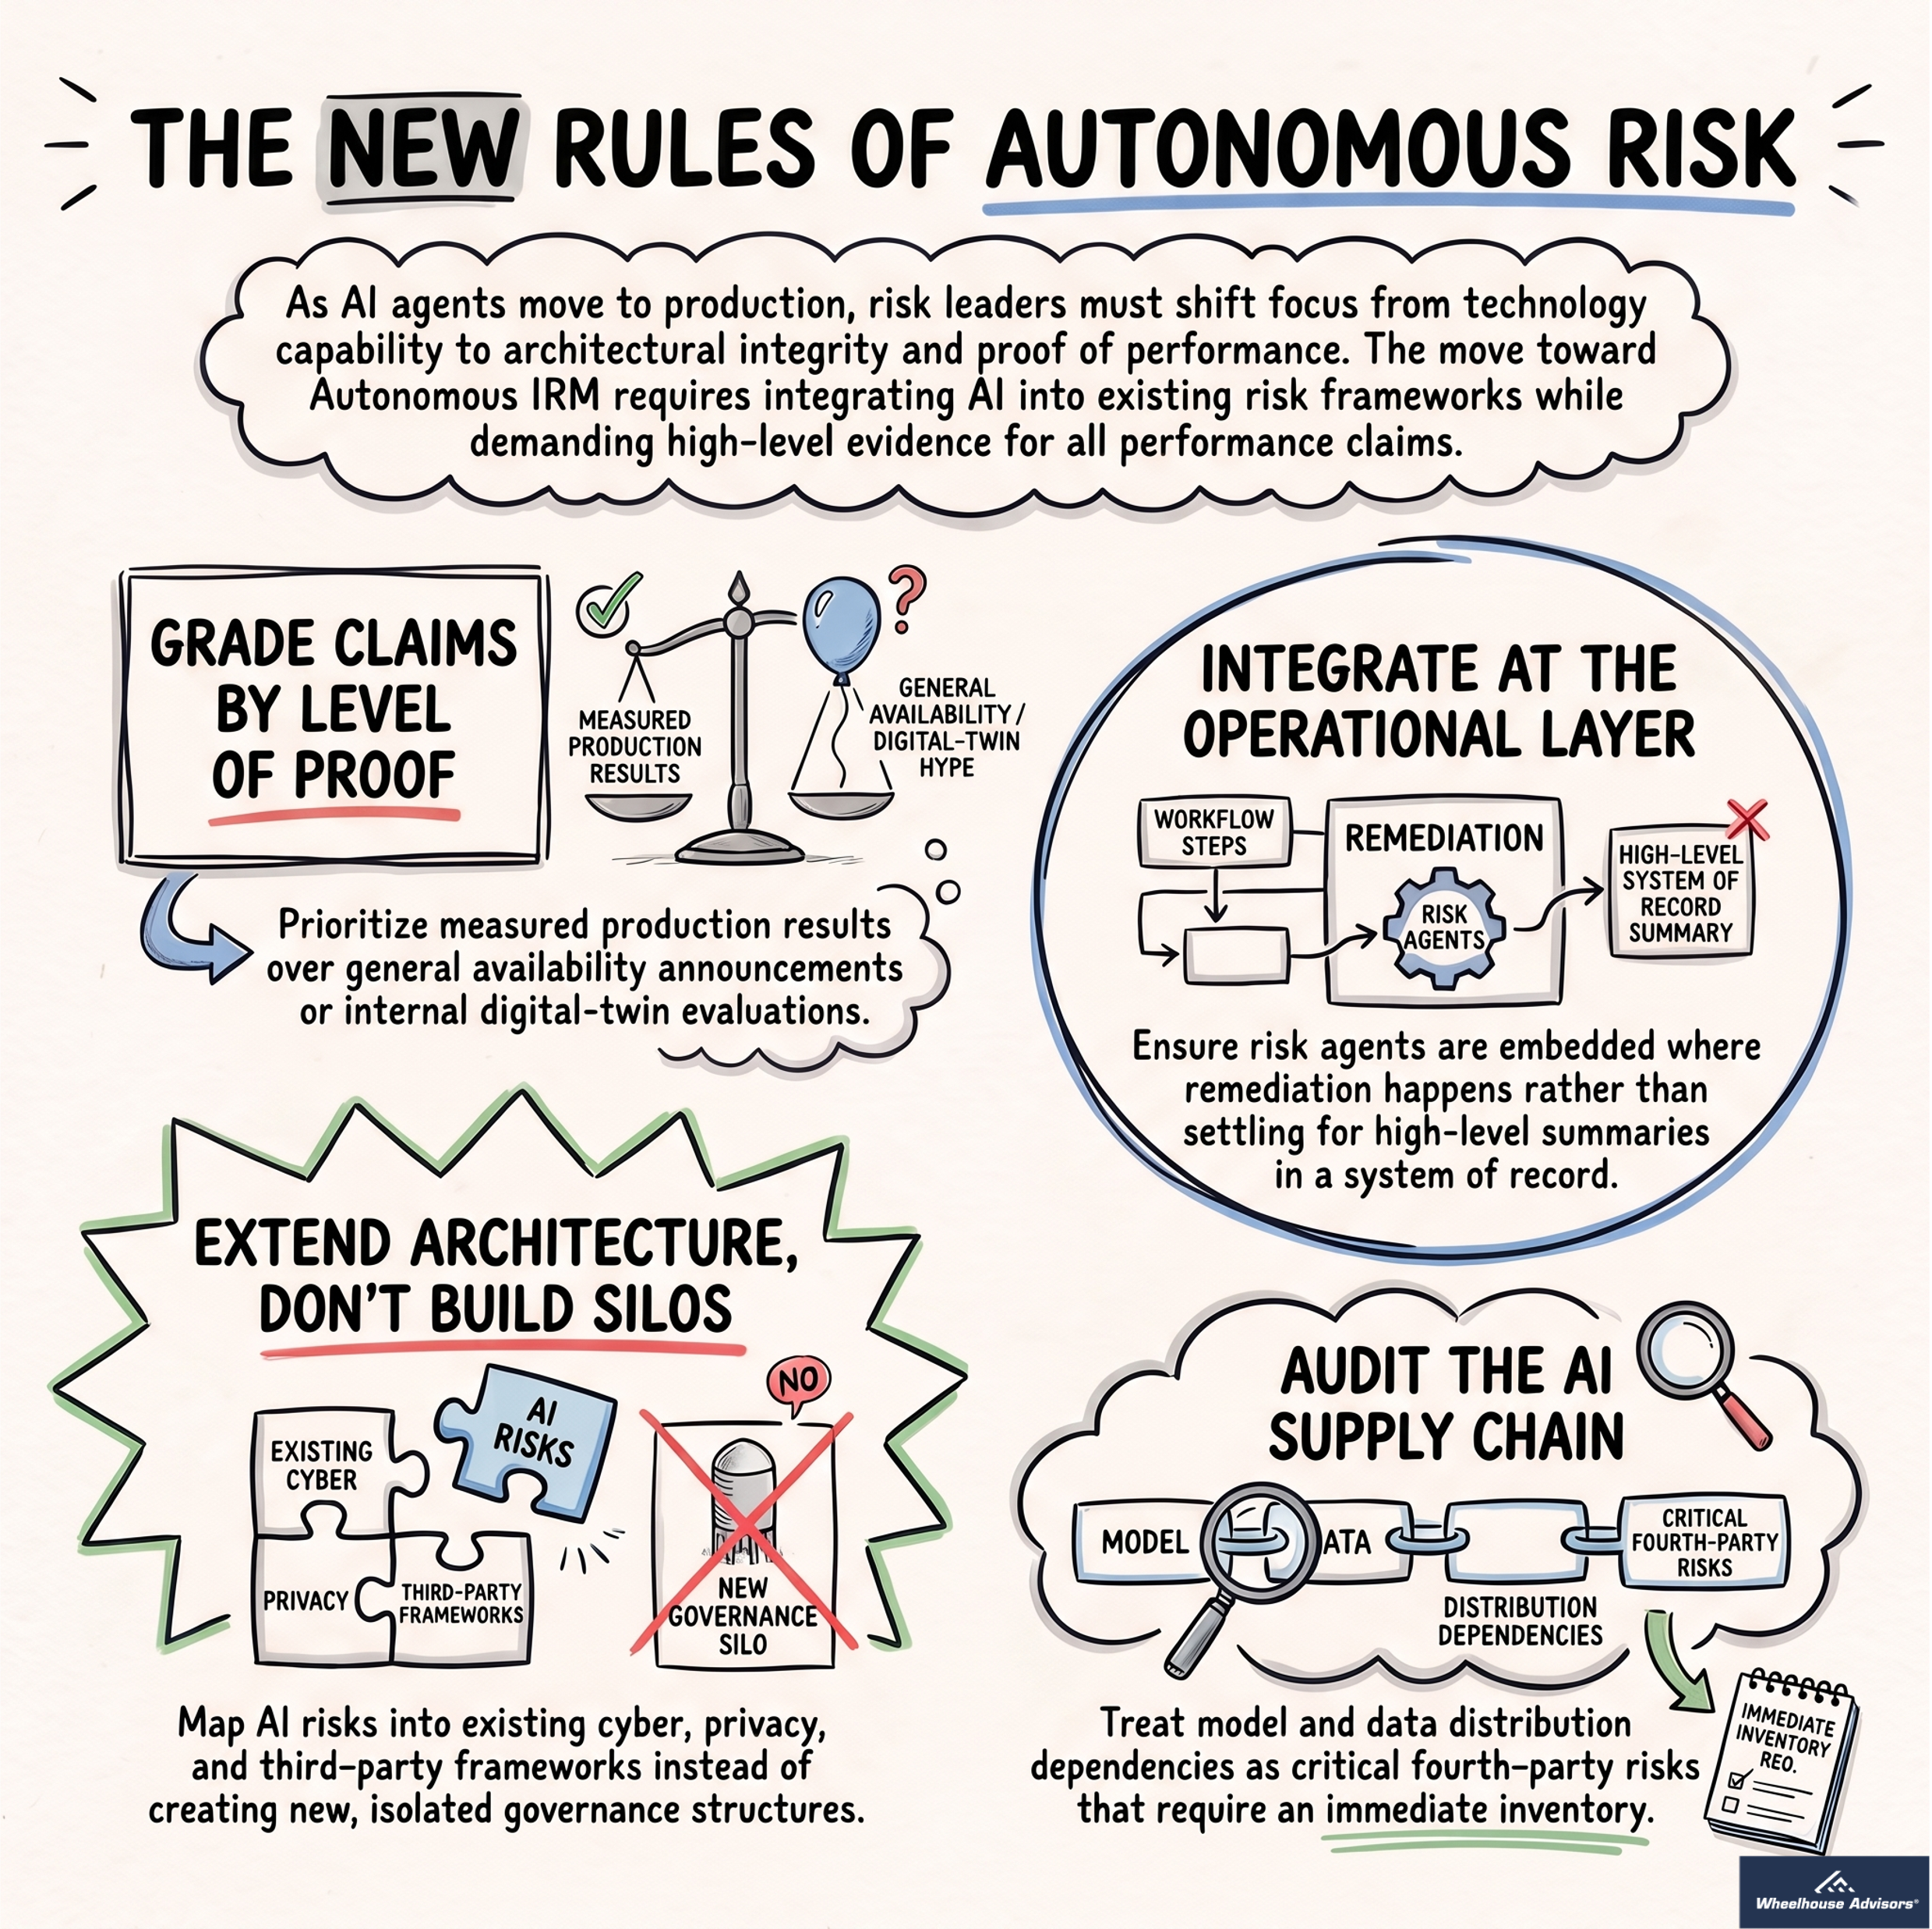
The safest factory is the one you can see: raw materials arrive, machines do predictable work, and when something fails you can point to the exact station that broke. AI flips that mental model. Our enterprise “assembly line” for decisions now runs in the dark across cloud systems, open source repositories, and black box models making probabilistic calls at machine speed. If you are responsible for integrated risk management, GRC, or security, that shift creates one urgent mandate: prove trust with defensible evidence.
We break down a single, chaotic week in the IRM market and use it as a lens on AI governance. We start with what risk teams are actually saying they need, then dig into ProcessUnity’s third-party risk management agents and the architectural reason narrow, constrained AI can be more auditable than a general-purpose LLM. From there we move to LogicGate’s broad rollout of GRC agents, its flat-fee pricing, and the PwC partnership built around UK Corporate Governance Code Provision 29, where boards must maintain granular control evidence behind legal declarations.
Next we tackle the Model Context Protocol (MCP) and why opening a GRC system to external AI models is both powerful and frightening. We outline the governance guardrails that matter most: agent-specific permissions, immutable logs, strict change control for prompts and models, and a hard line between AI recommendations and AI execution. Then we zoom upstream into CrowdStrike’s SafeMind, where autonomous red and blue agents collapse detection and remediation into a closed loop, forcing a fresh look at segregation of duties and independent assurance. We close with the G20 Carolina Principles on overlay governance and the supply chain shock of NVIDIA’s acquisition of Hugging Face, where fourth-party risk and AI model provenance become board-level concerns.
If this raised uncomfortable questions about your own auditability, that is the point. Subscribe, share this with your risk or security lead, and leave a review with the one control you think every AI program should implement first.
Visit www.therisktechjournal.com and www.rtj-bridge.com to learn more about the topics discussed in today's episode.
Subscribe at Apple Podcasts, Spotify, or Amazon Music. Contact us directly at info@wheelhouseadvisors.com or visit us at LinkedIn or X.com.
Our YouTube channel also delivers fast, executive-ready insights on Integrated Risk Management. Explore short explainers, IRM Navigator research highlights, RiskTech Journal analysis, and conversations from The Risk Wheelhouse Podcast. We cover the issues that matter most to modern risk leaders. Every video is designed to sharpen decision making and strengthen resilience in a digital-first world. Subscribe at youtube.com/@WheelhouseAdv.