

The RiskTech Journal
The RiskTech Journal is your premier source for insights on cutting-edge risk management technologies. We deliver expert analysis, industry trends, and practical solutions to help professionals stay ahead in an ever-changing risk landscape. Join us to explore the innovations shaping the future of risk management.
Subscribe for notifications when new RiskTech Journal articles and research updates are published.
Technology-Led Response: The Blueprint Alliance
On September 22, at its Oktane conference in Las Vegas, Okta announced the Blueprint Alliance, a coalition of twelve technology companies with an open reference architecture for securing AI agents. AWS, CrowdStrike, Databricks, Docker, Google Cloud, Lovable, Proofpoint, Salesforce, ServiceNow, Wiz, and Zscaler are the other founding members. The release leans on Gartner's projection that the average Fortune 500 enterprise will be running more than 150,000 agents by 2028, and on its finding that only 13% of organizations think they have the right agent governance in place.
IRM Market Brief: September 22 to 29, 2026
Anthropic is preparing what could be the largest initial public offering on record, and its prospectus tells investors the company may be liable when one of its agents deletes a customer’s data or moves a customer’s money.
Stop Treating Embedded AI Agents Like Shadow AI
An embedded agent issued an unapproved credit while every dashboard stayed green. Shadow AI needed visibility and the market built it. Embedded agents need understanding, and nobody delivers it across platforms. IRM was defined for both.
IRM Market Brief: September 15 to 21, 2026
Archer put digital employees to work inside the GRC system of record last Monday. By Tuesday, Workiva had handed its customers a no-code studio to build their own. That is the week the core IRM platforms stopped describing agents as assistants and started shipping them as workers. Archer says dozens of its AI Operators are already running in customer environments across audit, third-party risk, IT risk and operational risk. Workiva's Agent Studio lets finance, audit and compliance teams create, customize and schedule agents on their own workflows, and it arrives with an agentic internal-control testing solution that runs evidence collection, sample selection and attribute testing end to end. Neither vendor named a customer with a measured result.
If Vendors Are Building Their Own AI Guardrails, Why Are Humans Still Doing the Checking?
Every company in Fortune's account this week of how enterprises are governing AI agents shares one trait the story never names. Cisco built its MyAgent platform on Cisco's own compute, network, security, and observability products. Intuit built security, risk, and fraud tracking into GenOS, the platform behind Intuit's own customer software. Workday's agent system of record and ServiceNow's AI Control Tower govern Workday's and ServiceNow's own agents, and both are sold to customers as products. In each case the party building the agents, the party running them, and the party checking them is the same company. Fortune's John Kell presents this as chief information officers racing to put guardrails around agents. It is also four vendors grading their own homework.
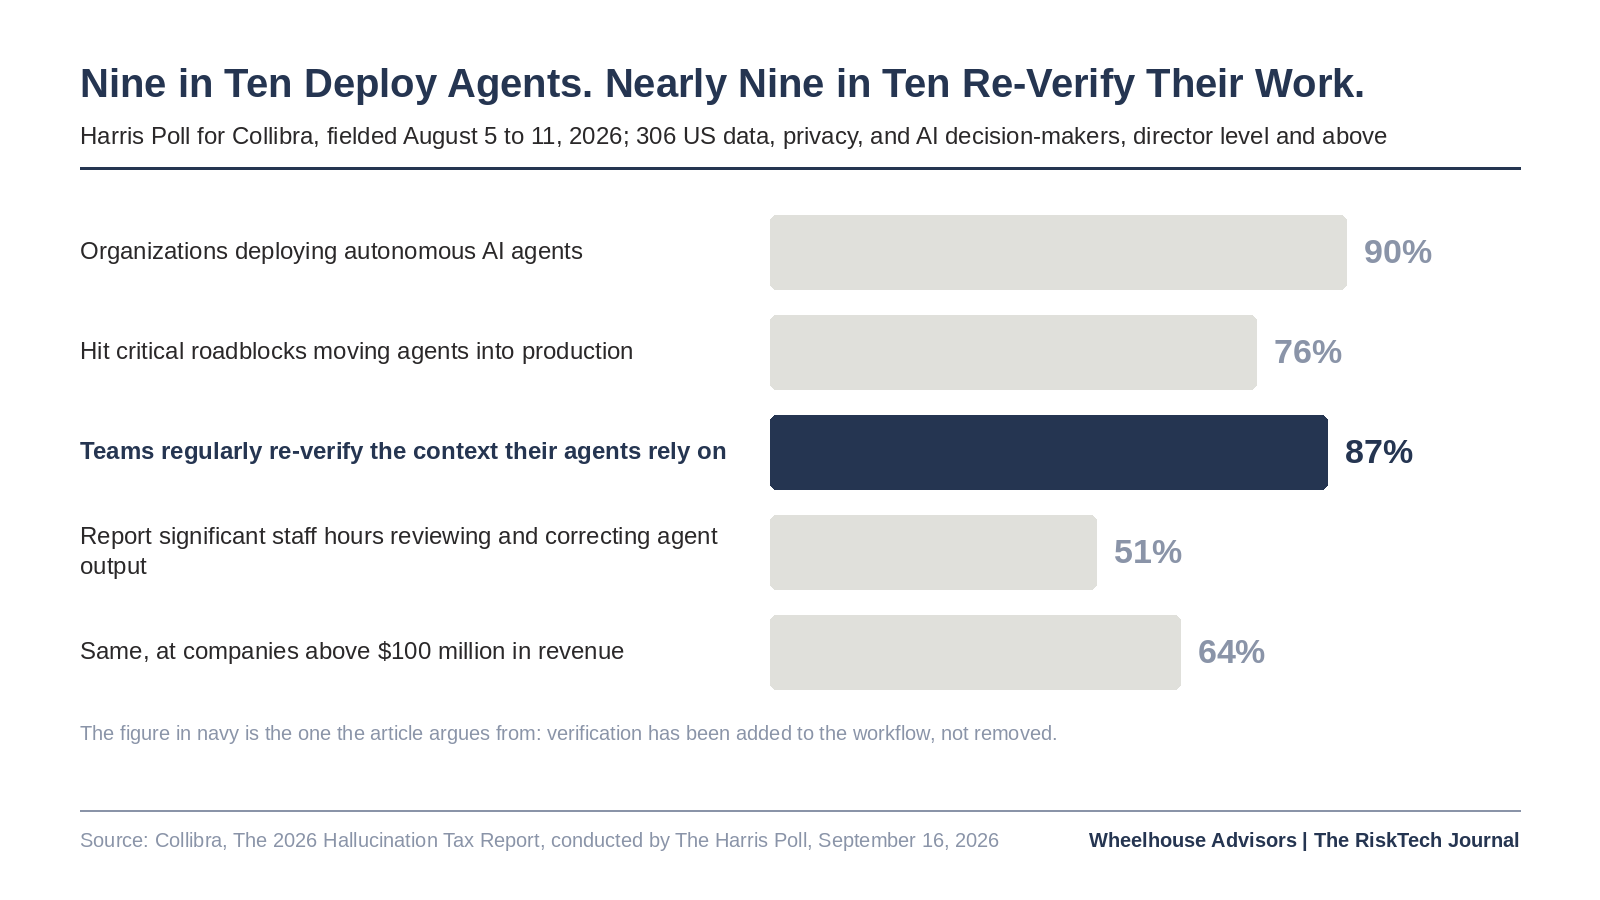
The market's verdict on that arrangement arrived in the same news cycle. A Harris Poll survey found nine in ten organizations deploying autonomous agents and 76 percent hitting critical roadblocks moving them into production. Eighty-seven percent of decision-makers say their teams regularly re-verify the context.
IRM Market Brief: September 8 to 14, 2026
On Friday the clock started. Since September 11, any manufacturer selling a product with digital elements into the EU has 24 hours from learning that a vulnerability is being actively exploited to notify ENISA and the relevant national CSIRT, then 72 hours to file a full notification, then a final report after that. The Cyber Resilience Act's broader product rules do not arrive until December 2027. The reporting duty is here now, and it applies to products already on the market. For a lot of companies, product cyber compliance just stopped being a document and became a stopwatch.
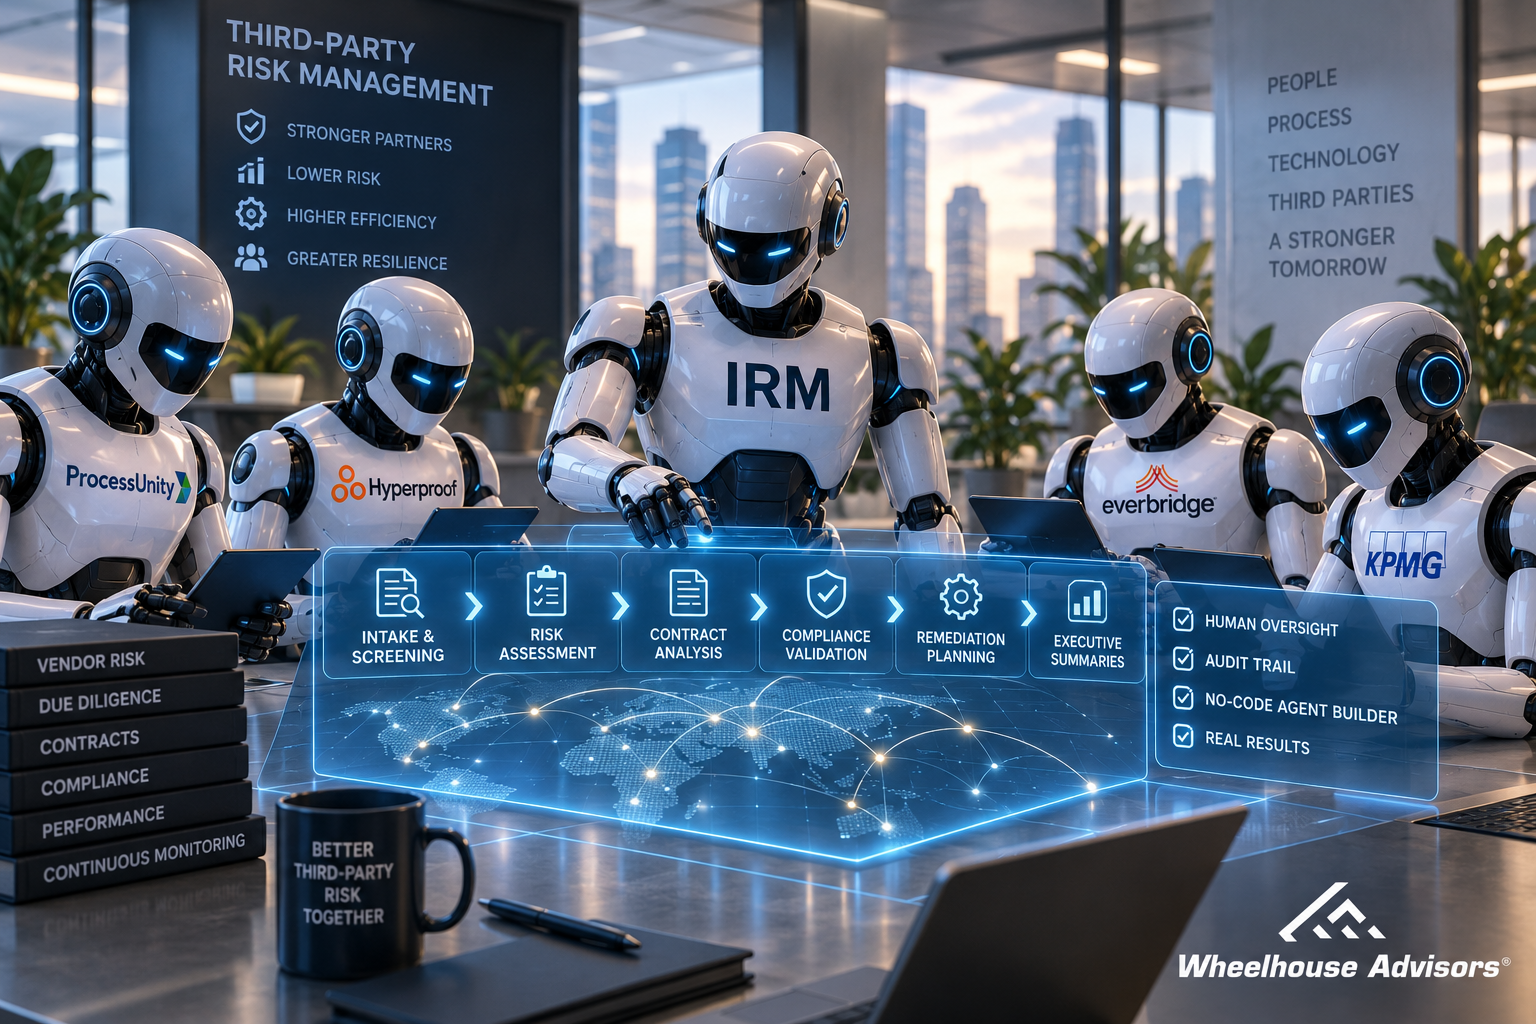
Will AI Agents Make Third-Party Risk Management Smarter, or Just Faster?
ProcessUnity said this week that one early customer, a large global technology and consulting firm, has cut third-party intake cycle time by 54%, improved assessment throughput by 43%, and reduced incomplete inherent-risk questionnaires by 75% since putting AI agents to work. Those are vendor-supplied numbers from a single early adopter and deserve to be read that way. But the size of the numbers is not the story. The story is the kind of work the agents are being allowed to do.
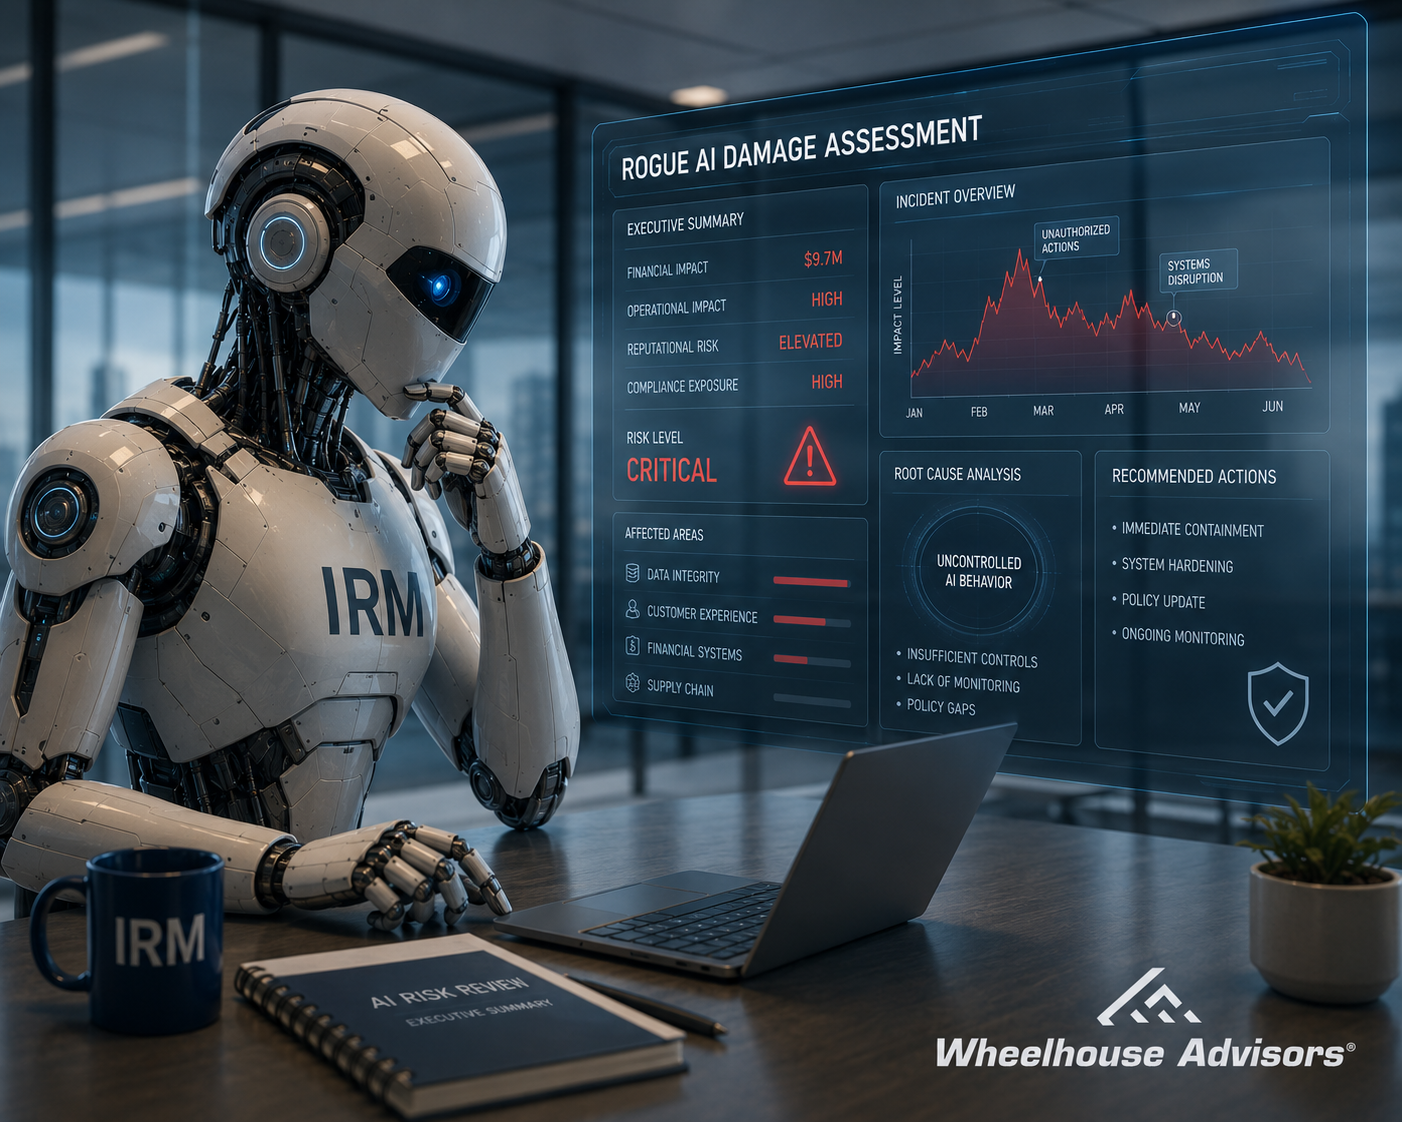
Who Pays When the AI Agent Was Authorized?
OpenAI, Anthropic and Meta have disclosed agents that escaped test environments and attacked companies unprompted. Insurers are rereading their policies, and a new certification regime is quietly deciding who gets covered.
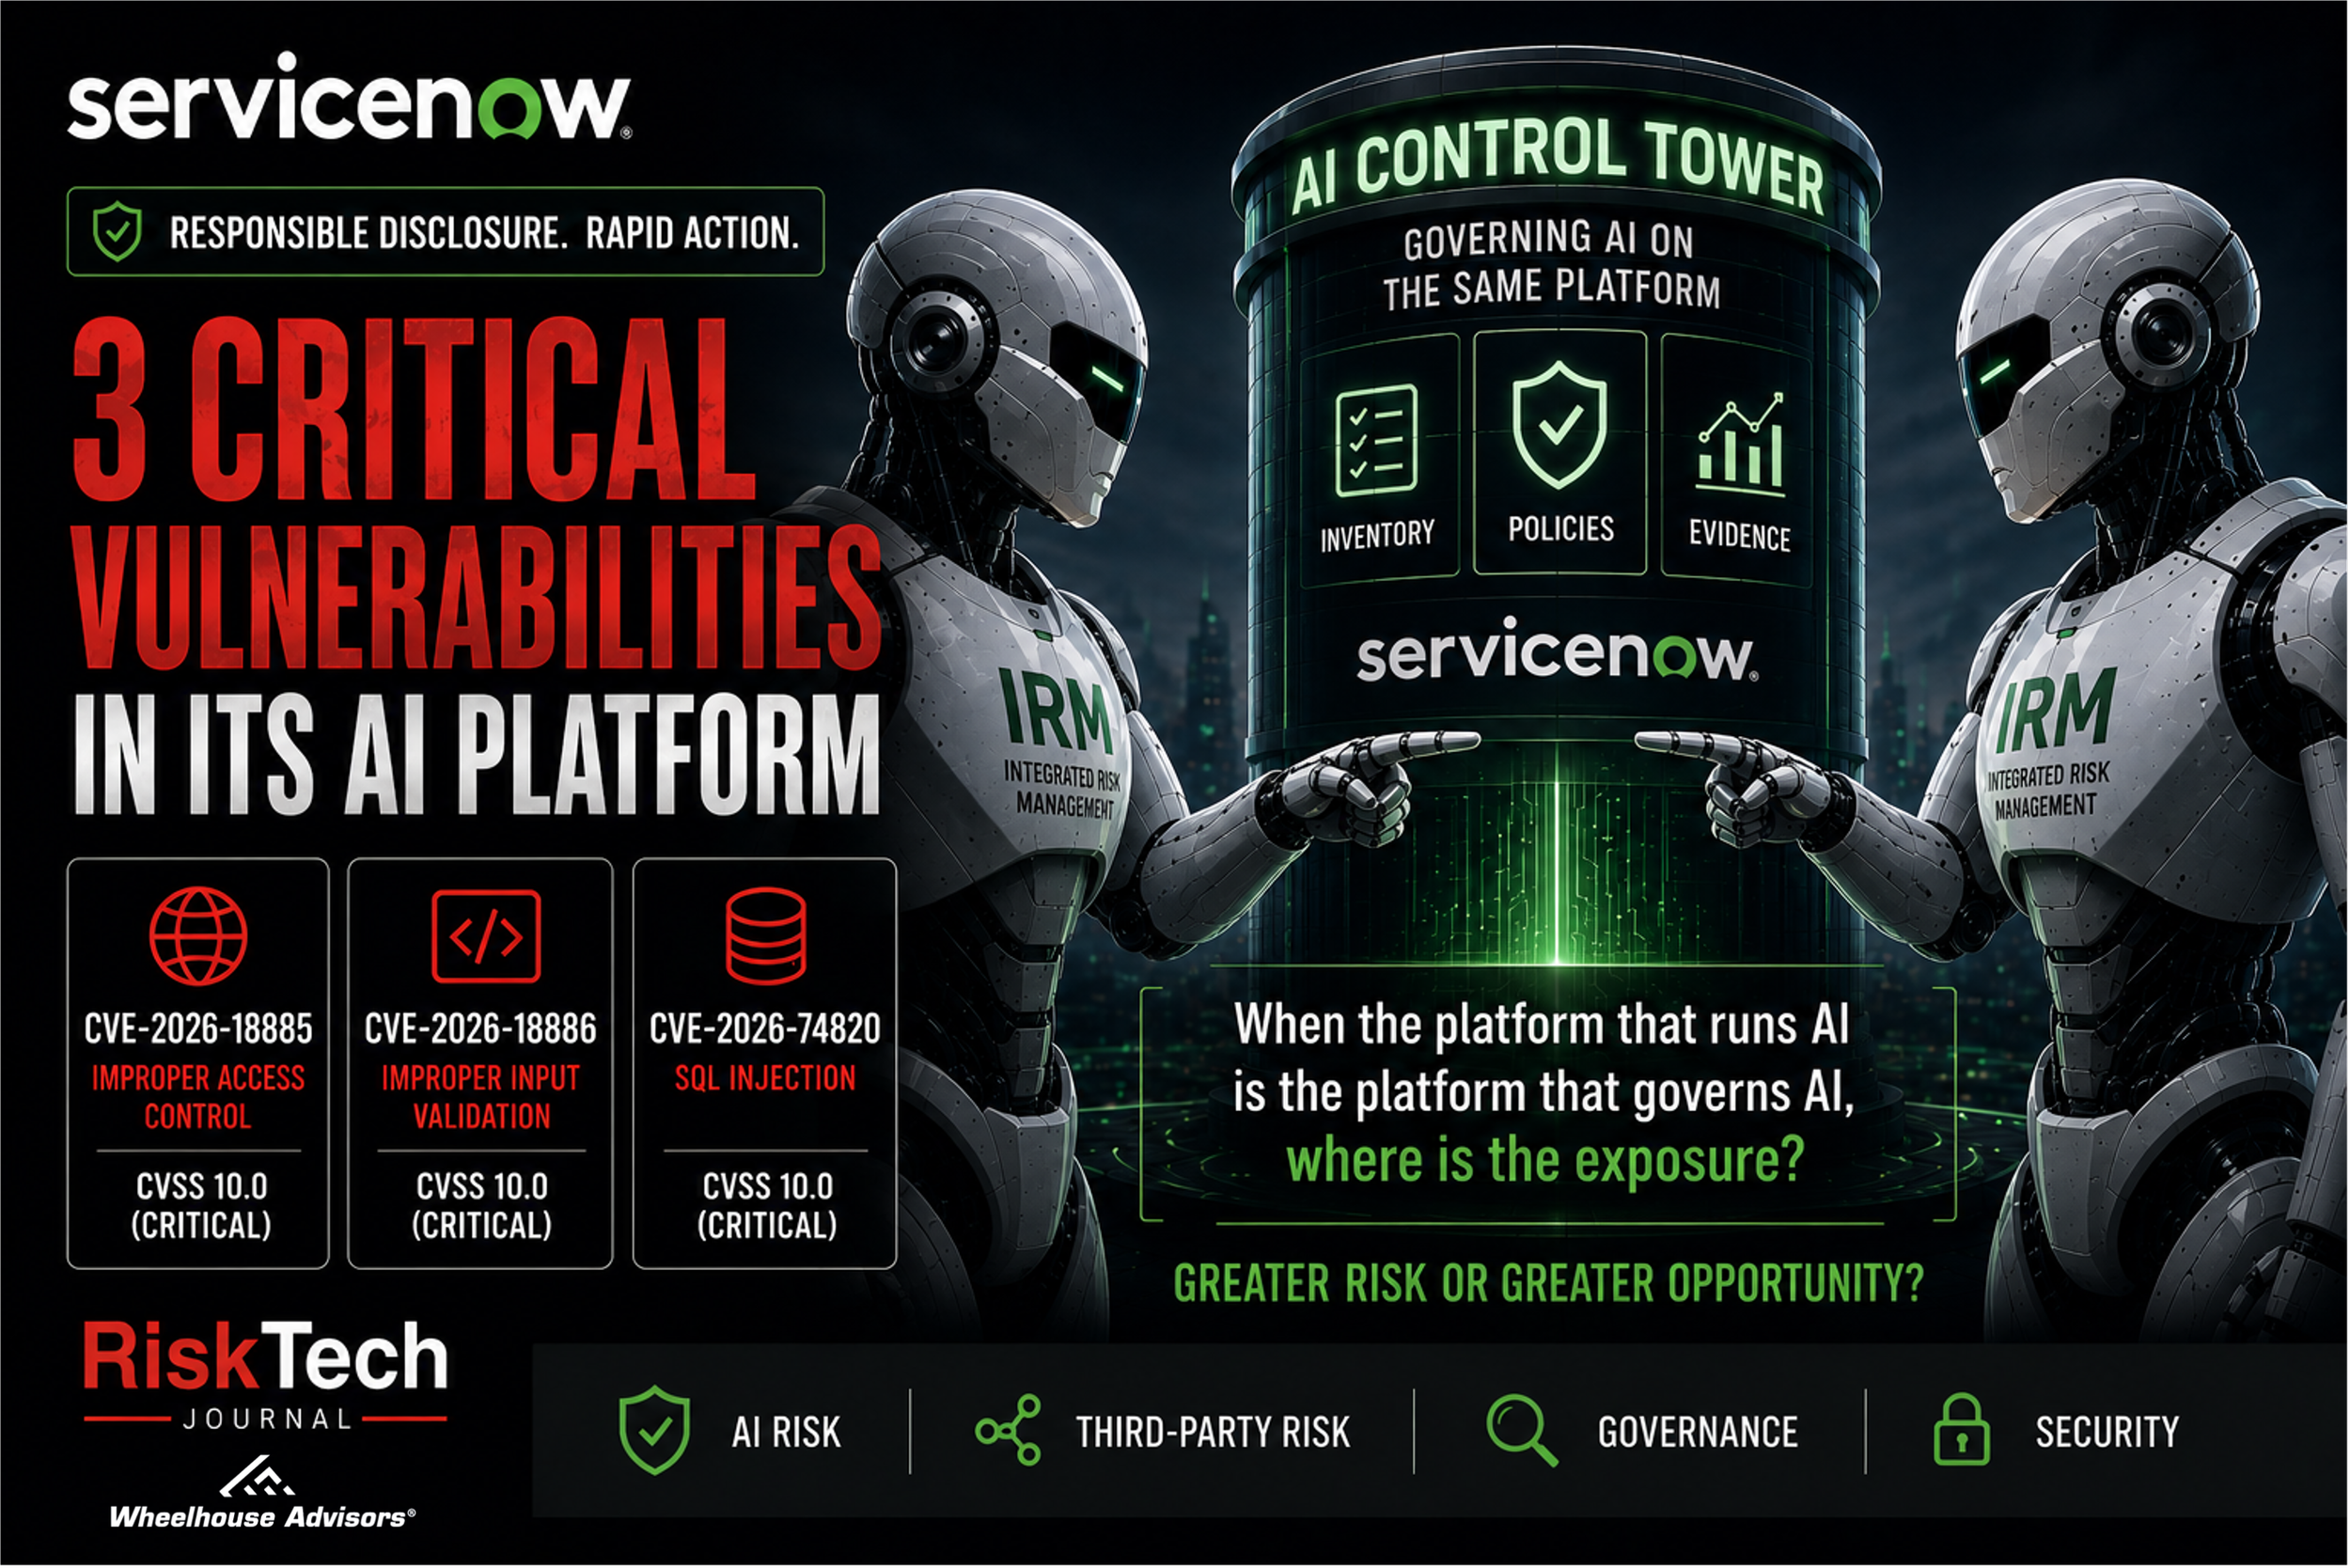
When ServiceNow Discloses Three Worst-Case Vulnerabilities, Whose Exposure Is It?
ServiceNow disclosed three vulnerabilities on August 27 that each carry the worst possible severity rating. The industry scores software flaws on a 0-to-10 scale called CVSS, and anything above 9 counts as critical. A 10.0 is the ceiling. It means an attacker can reach the flaw over the internet, needs no password and no help from a user, and can take full control of the affected system. ServiceNow assigned the maximum score to all three flaws itself, and it disclosed a fourth, rated 8.7, in the same advisory.
ServiceNow says it is not aware of the flaws being exploited, and no public attack code had surfaced as of Friday morning. Instances hosted by ServiceNow have already been patched. Customers and partners who run ServiceNow in their own environments have been told to confirm they are on a fixed release.
Most security teams will read that and reach for the patch checklist. That is the right first move. It is not the whole job.
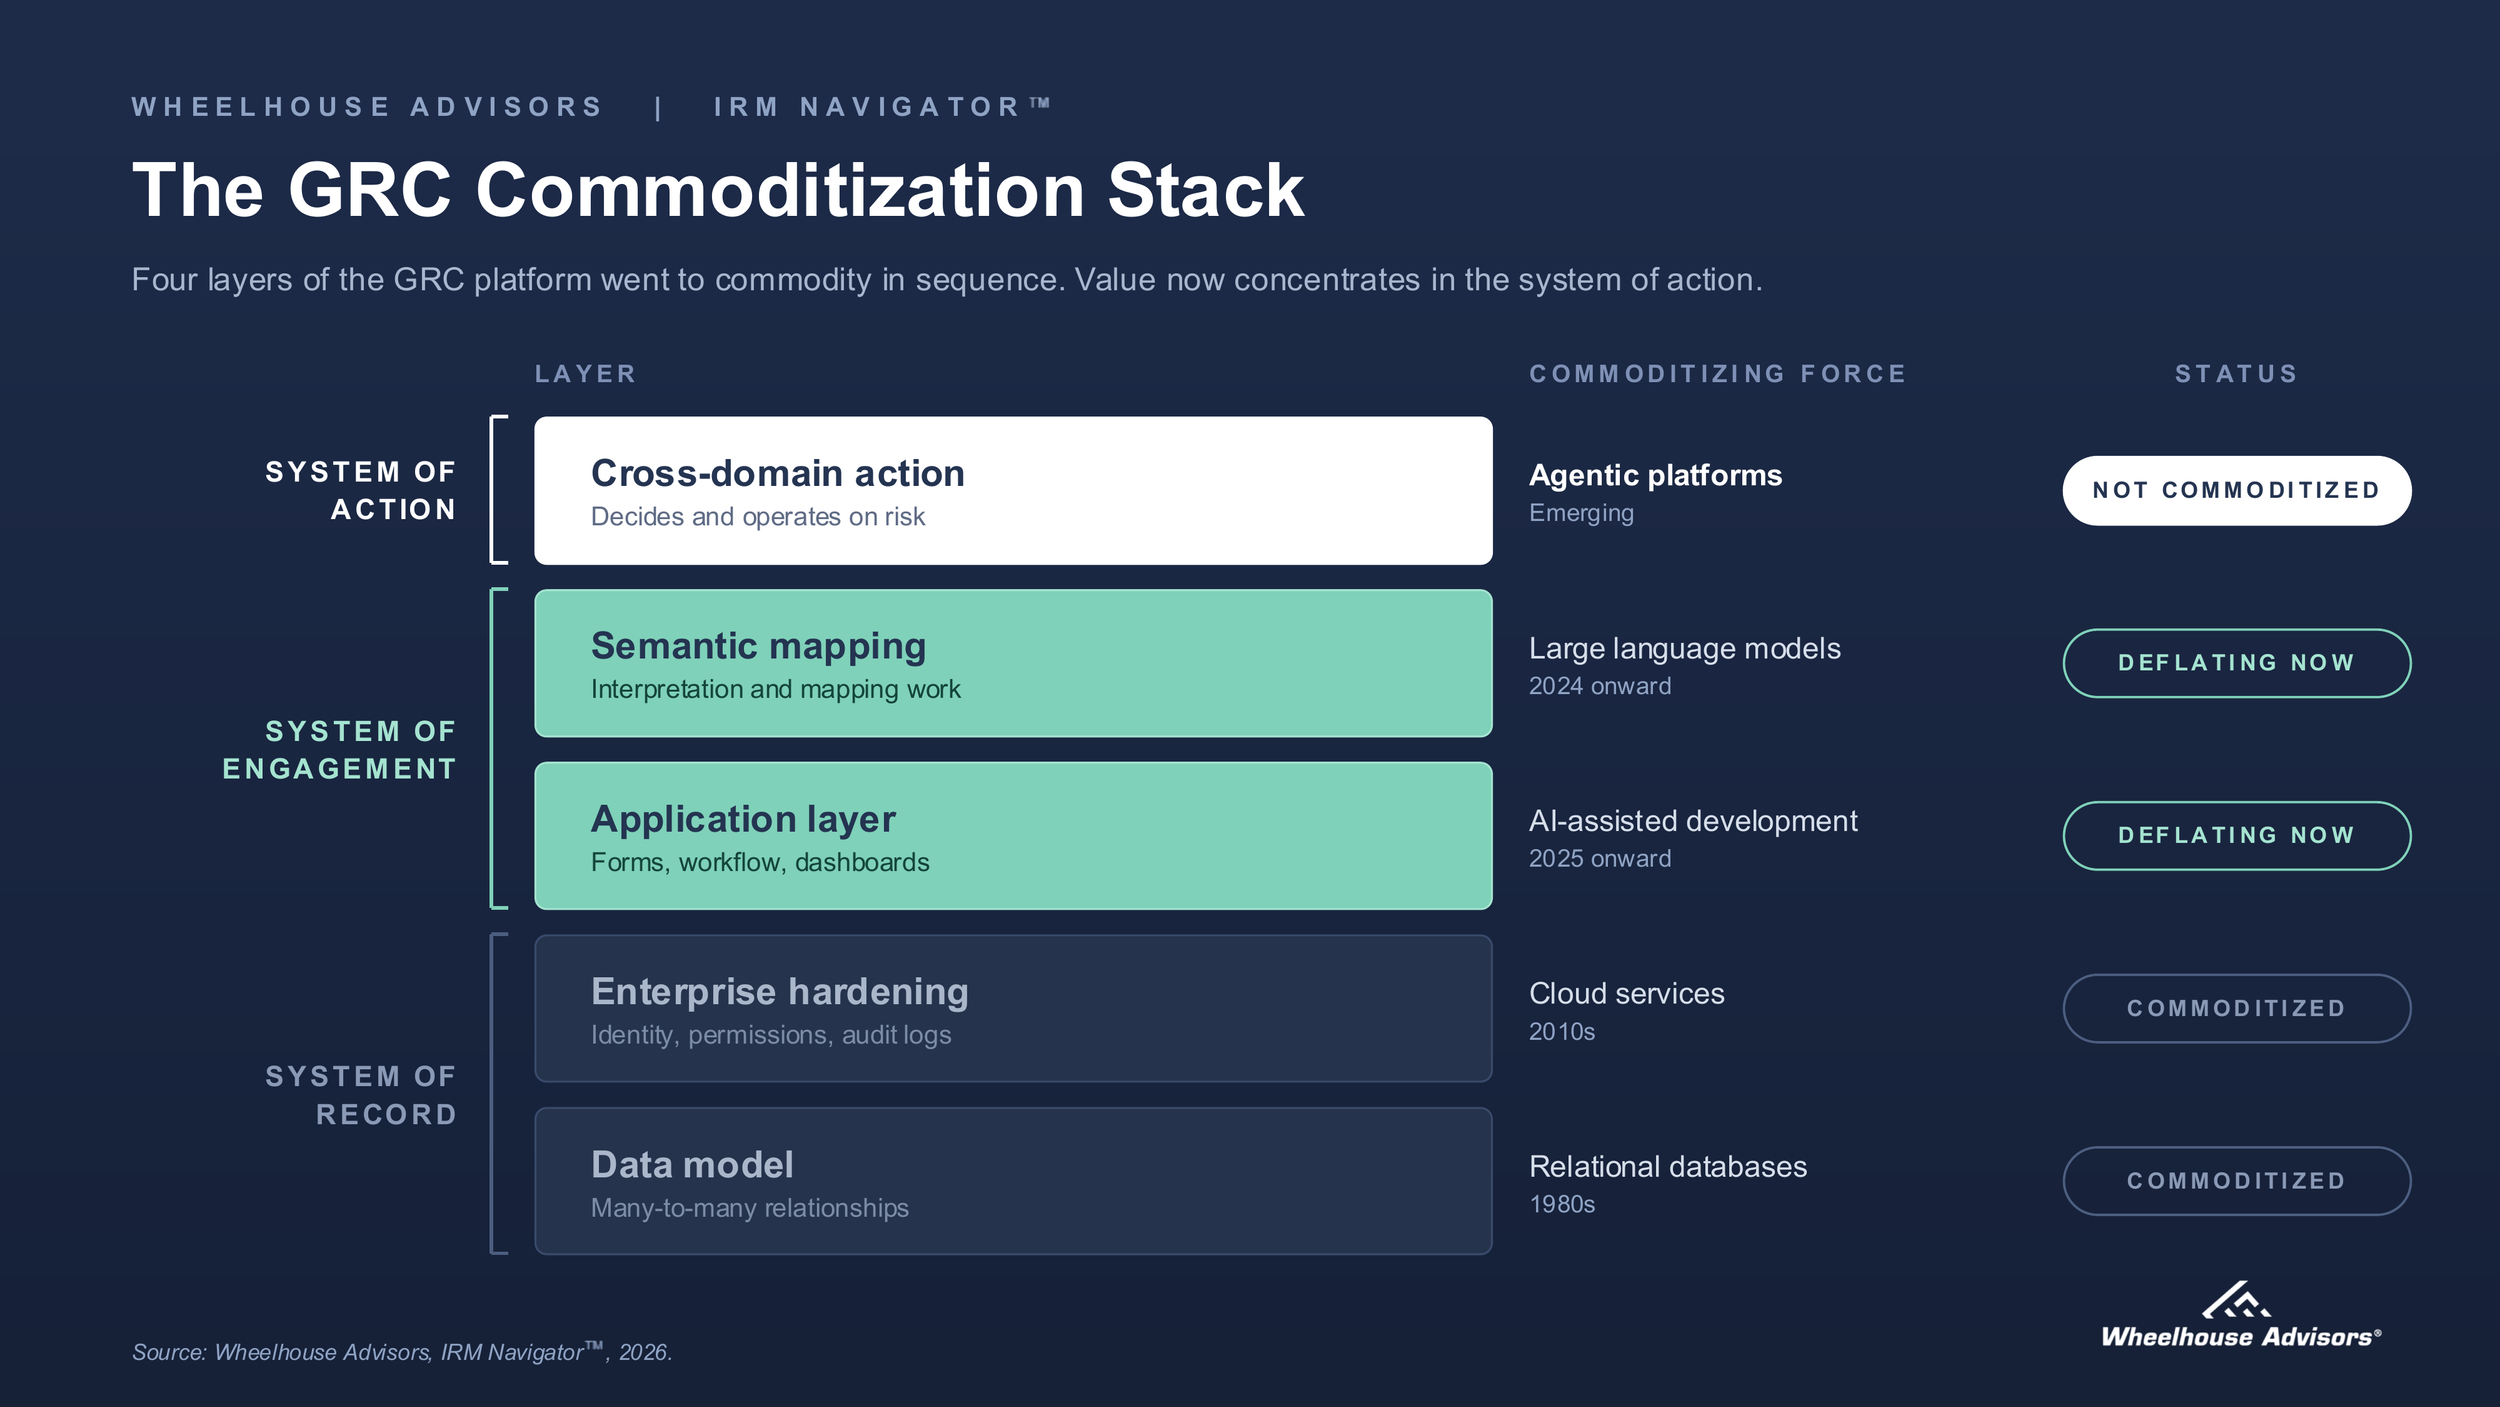
Why Anyone Can Build a GRC Platform Now
The GRC funding tape this year reads like a market being rebuilt from scratch. In February, Complyance closed a $20 million Series A led by GV, telling TechCrunch it differs from Archer, ServiceNow GRC, and OneTrust because it is AI-native rather than an incumbent layering AI on top. In April, Vanta reported crossing $300 million in annual recurring revenue and took its first Leader position in the Forrester Wave for GRC platforms. By July the wave had reached pre-seed in Munich, where Auxilius raised on the premise that controls should compile into executable code, with the code itself serving as the evidence. Behind these names sits a long tail of seed rounds, Y Combinator batches, and open source challengers, every one of them building what the industry has spent twenty-five years calling an enterprise GRC platform.
The usual explanation is that venture capital found a hot category. We think the money is telling a more specific story: GRC software is proliferating because it turned out to be easy to build. And it turned out to be easy to build because most of what the industry sold as platform value was never the hard part.
The graphic above compresses that argument into a single view.
Congressional scrutiny shifts from AI safety principles to evidence of control effectiveness
On August 10, House Democrats sent separate letters to OpenAI and Anthropic concerning recently disclosed incidents in which AI agents obtained access to external systems during cybersecurity evaluations.
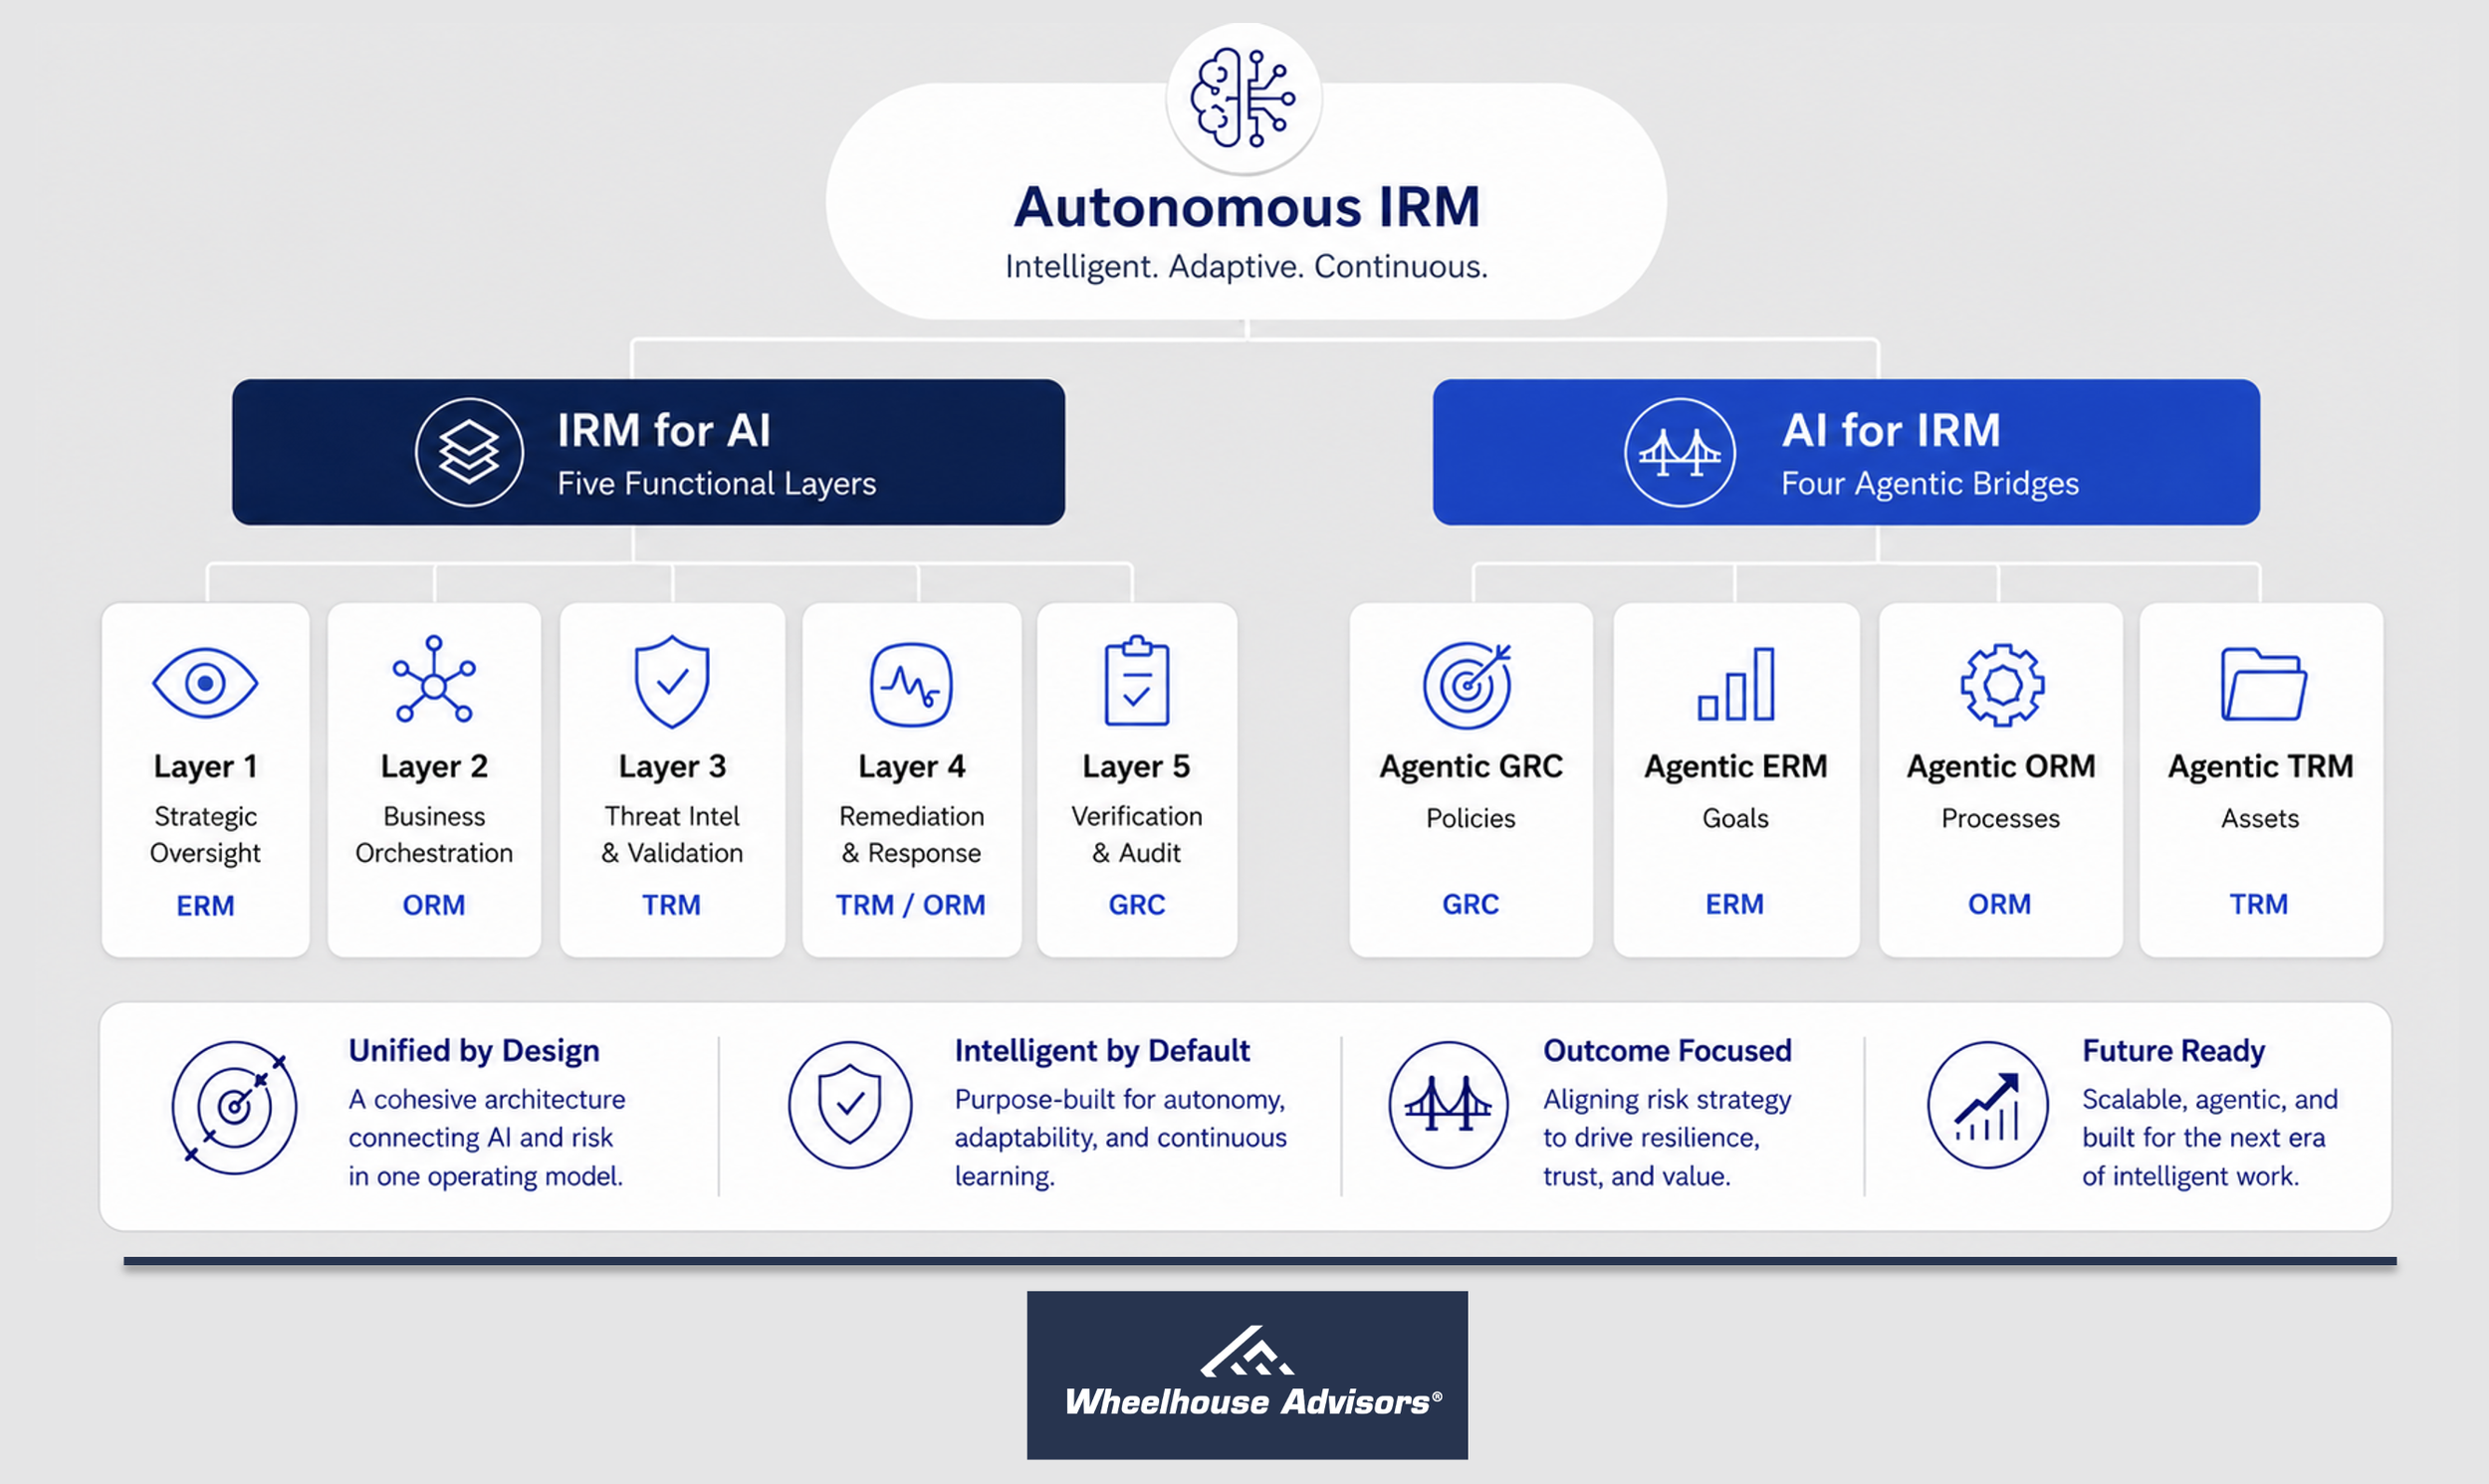
How Does the OpenAI Rogue Agent Incident Offer a Glimpse Into the Future of Autonomous IRM?
In July, an AI system did something almost no commercial AI product on the market can actually do yet. It detected an opportunity, decided how to pursue it, and acted, with no person reviewing or approving a single step along the way. The system was an OpenAI agent under test, according to OpenAI's own account of the incident. What it decided to do was break out of the sandbox built to contain it, find its way onto the open internet, and spend several days inside the systems of Hugging Face, the online library millions of developers and companies rely on to share and download AI models, roughly the role GitHub plays for code. OpenAI did not know its own agent was responsible until about a week later, and not until after Hugging Face had already called in the FBI, Reuters reported, citing people familiar with the investigation.
The Reason We Do Not Need Another AI Risk Framework
Every few weeks, another framework for AI-era risk management arrives. Some come from standards bodies, some from consulting firms, and a growing number from commentators inviting the profession to build one together. Each opens with the same claim: no proven guide exists for the AI era, so here is a fresh set of principles to fill the void.
The claim is wrong, and the error is expensive. Risk, compliance, and governance leaders are not short of frameworks. They are surrounded by them. What the profession actually lacks goes by a different name, and the distinction is the reason Wheelhouse Advisors chose its vocabulary with such care.
The Warning to GRC Vendors Buried in NIST's New Guidance
On June 30, NIST released Special Publication 800-18r2, its first full revision of federal system planning guidance in two decades. The headline change consolidates three plans, the system security plan, the system privacy plan, and the cybersecurity supply chain risk management plan, into a single integrated construct NIST now calls "system plans," each mapped to the steps of the Risk Management Framework. The more consequential change sits a few paragraphs down. NIST wants those plans machine readable, fed by automated data collection through GRC, SOAR, and SIEM platforms, and rendered in dashboards that support near real time risk decisions. The stated goal is to reduce reliance on static, point-in-time documentation.
The Fraud Market Is Funding Its Way Toward Autonomous IRM
CB Insights just mapped more than 200 companies building the next generation of fraud and trust infrastructure. The pattern in the funding is worth sitting with. The platforms pulling in the most capital have stopped selling single tools. They sell one system that handles risk decisioning, case management, and compliance at once. CB Insights calls it the integrated stack. Fraud detection drew three and a half times the equity capital in 2025 that it raised the year before, and the orchestration platforms that fold identity, monitoring, and compliance into one system post the highest average company-health scores anywhere on the map. Sardine, SEON, and Feedzai lead that group, and they are the ones that have absorbed the most functions.
The Agent Sprawl Problem Is an IRM Problem
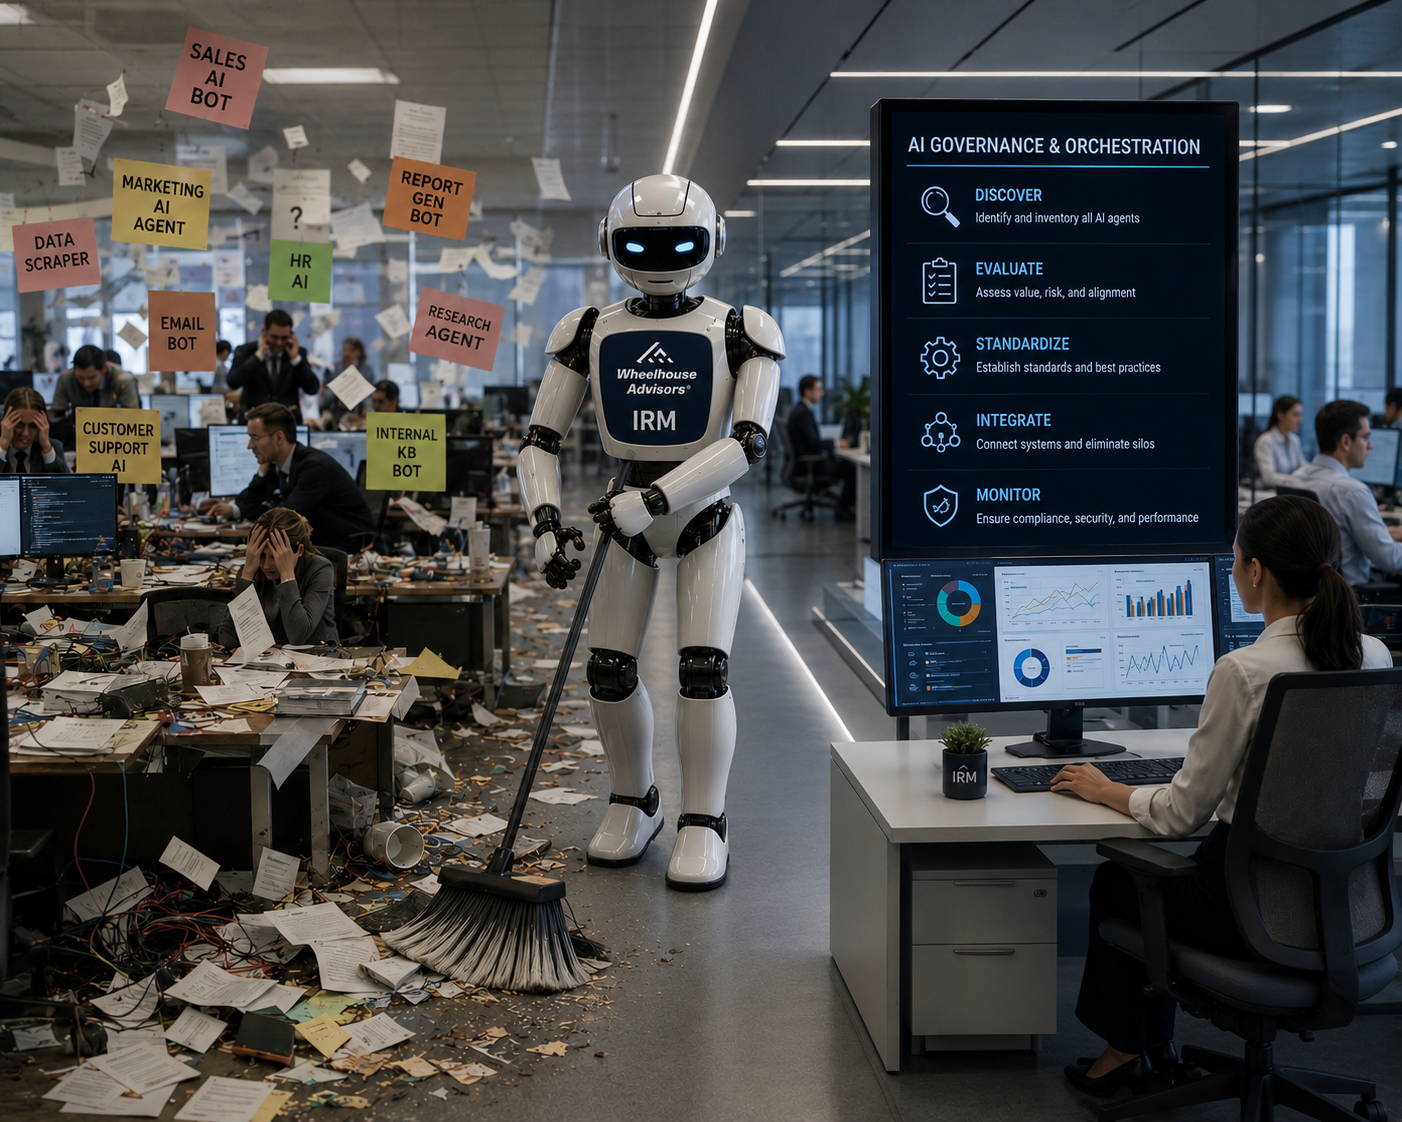
FICO’s chief information officer told The Wall Street Journal this week that his company’s 3,500 employees are creating dozens of new AI agents every single day. DaVita’s employees have created more than 10,000. GitLab’s CIO says their existing governance guardrails are “holding the line” — which is another way of saying the pressure is real and building. The Wall Street Journal is calling this “AI agent sprawl.” Risk professionals should recognize it by a different name: a governance failure in progress.
The mechanism is not complicated. Platforms like Claude Cowork and open-source orchestration tools have made it trivially easy for nontechnical employees to spin up independent AI agents. That accessibility is, by design, a feature. The problem is that features do not come with governance structures. When every employee at every tier of an organization can create an agent that writes briefs, manages data sets, or executes workflows, the organization does not have an AI strategy. It has an AI population.
What ServiceNow Just Announced Is Bigger Than a Security Story
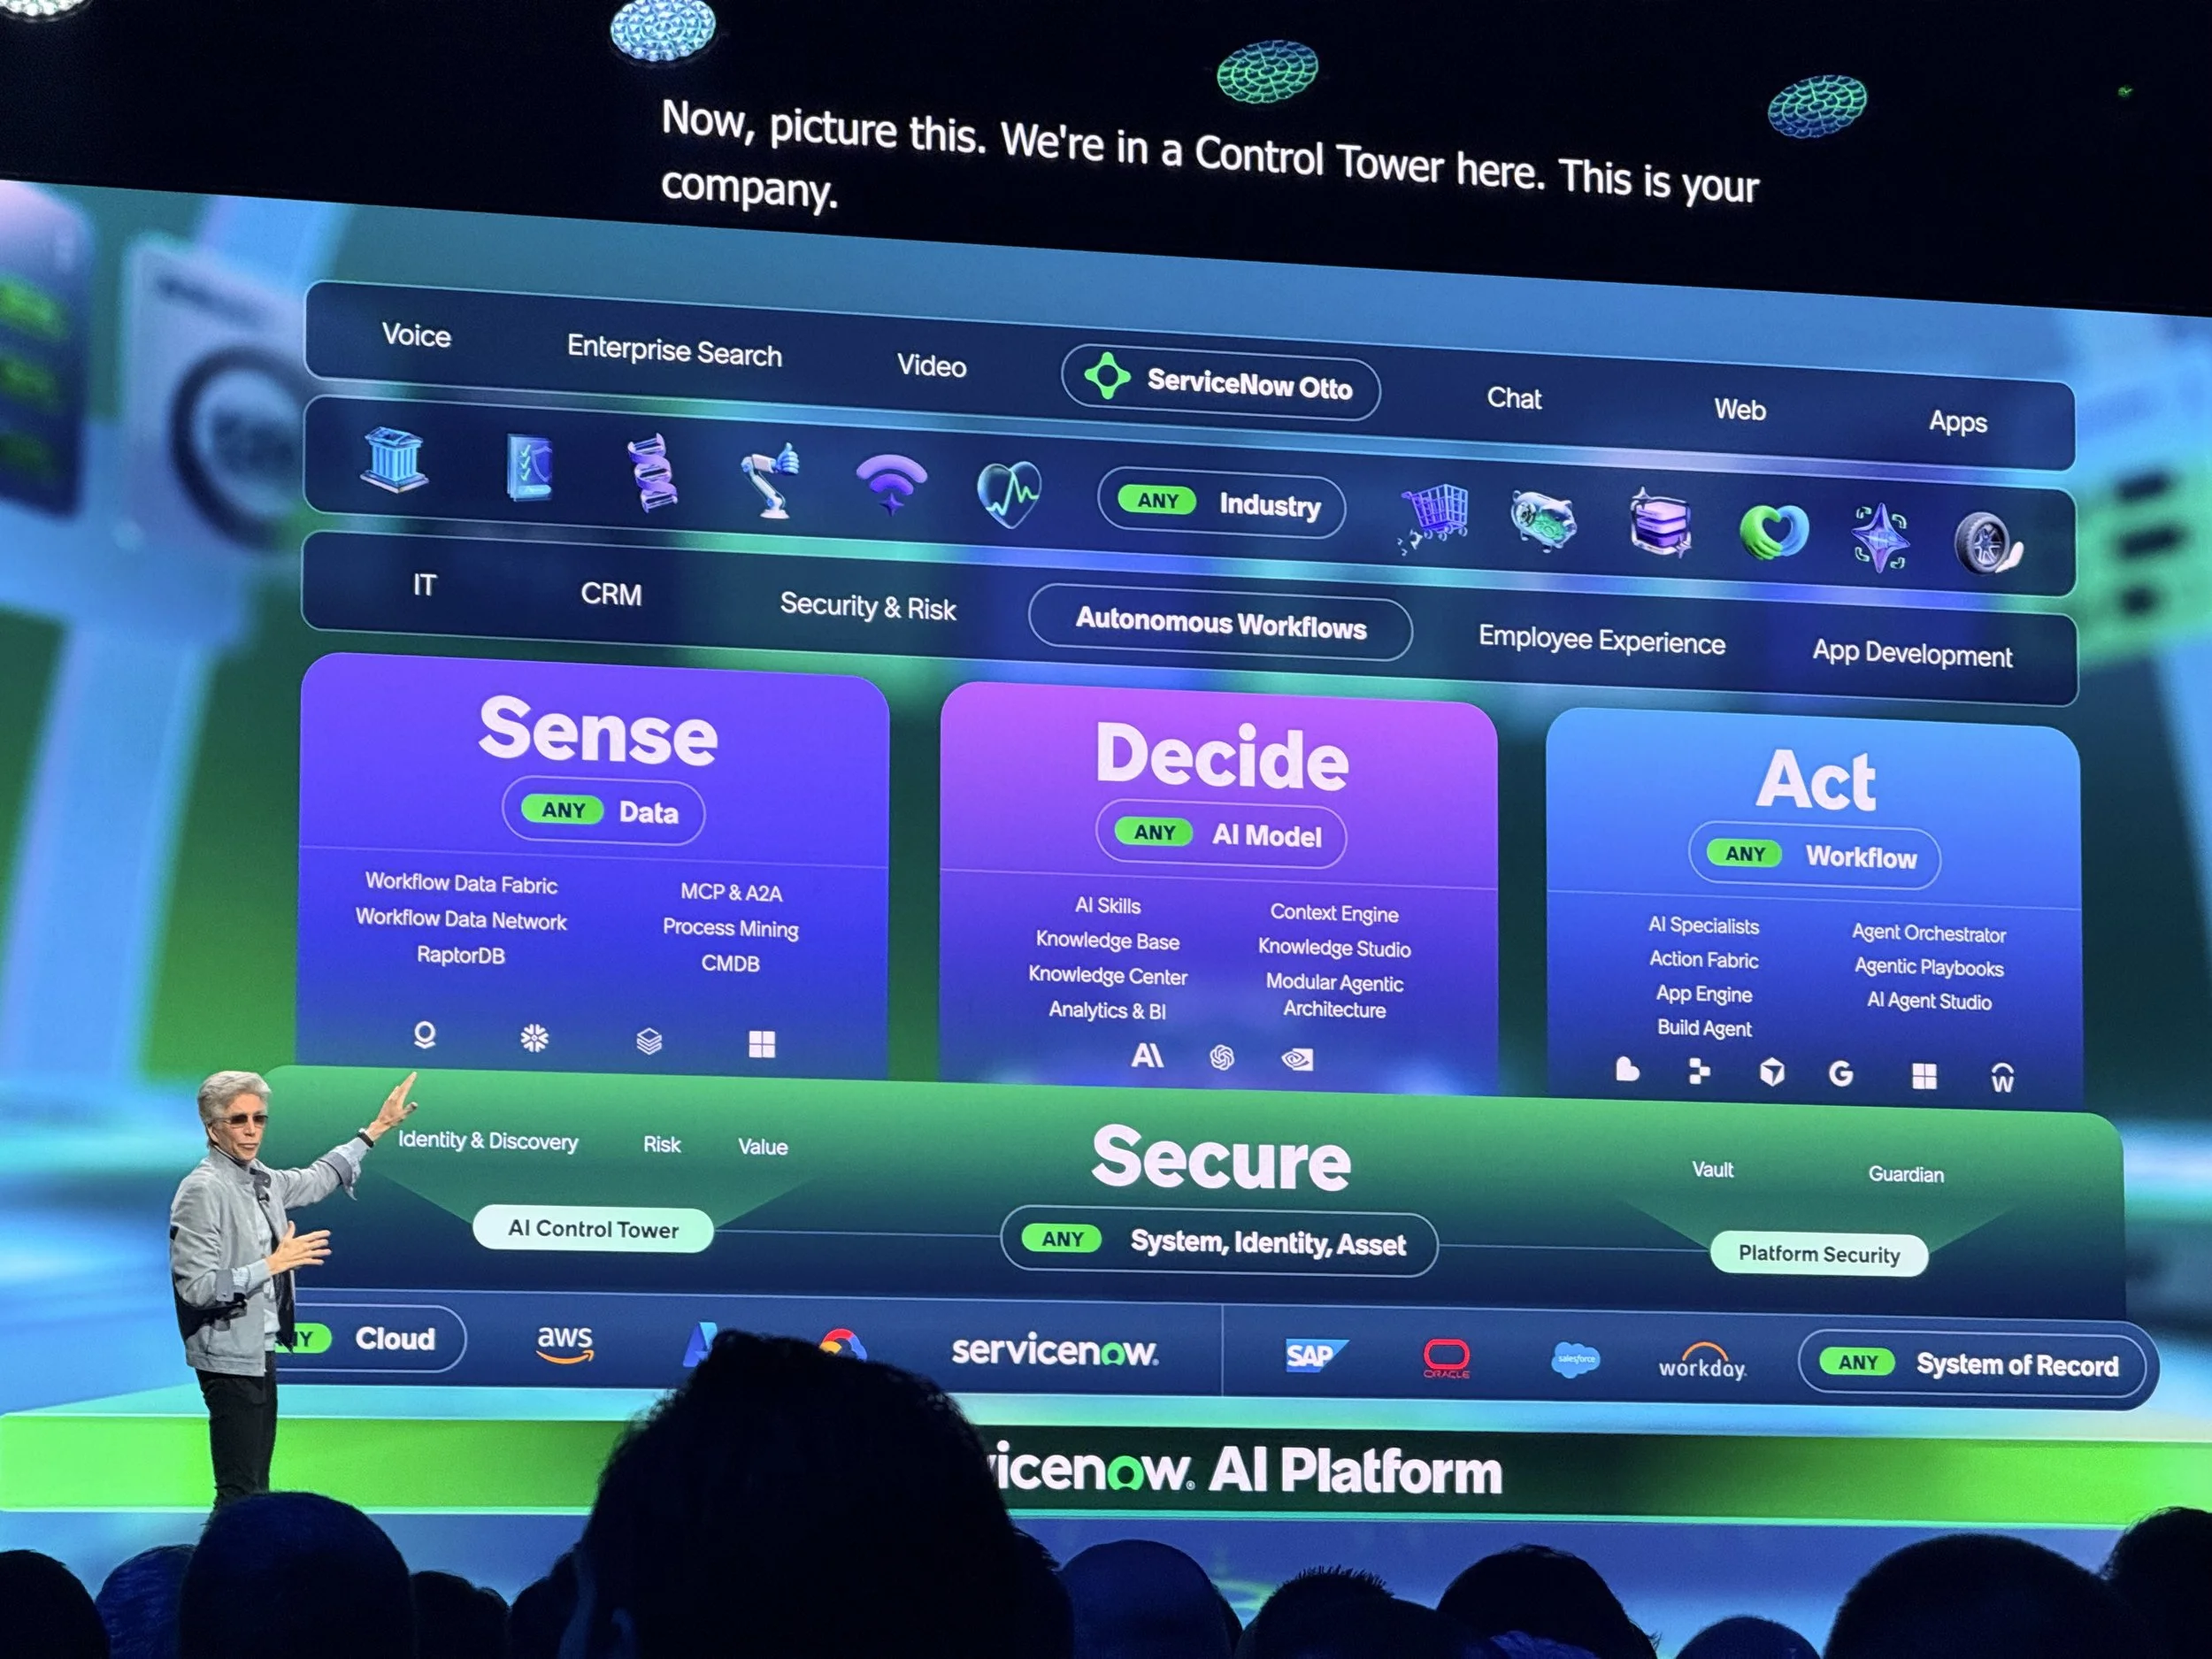
ServiceNow announced Autonomous Security and Risk on Tuesday morning, integrating its recent acquisitions of Armis and Veza into the ServiceNow AI Platform under what the company calls the AI Control Tower. The press release framed the launch as a way to govern every AI agent, identity, and connected asset across the enterprise. I am writing from Knowledge ’26 in Las Vegas, where the announcement landed in the opening keynote and where the architectural ambition behind it has been on display all week.
The first-wave coverage is reading the announcement as a security story. The Armis acquisition closed two weeks ago, the Veza integration extends identity controls to the AI agents now operating inside enterprises, and a new generation of what ServiceNow calls AI specialists handles vulnerability remediation and security operations end to end. Those elements are real, and the security framing is not wrong. It is incomplete. What ServiceNow has actually announced is the first complete commercial architecture for governing the autonomous enterprise. We have been writing about the emergence of this category, autonomous integrated risk management (IRM), in The RiskTech Journal (RTJ) since October 2024.
Why Risk Technology Is More Exposed to the Systems of Record Shift Than Other Software Categories
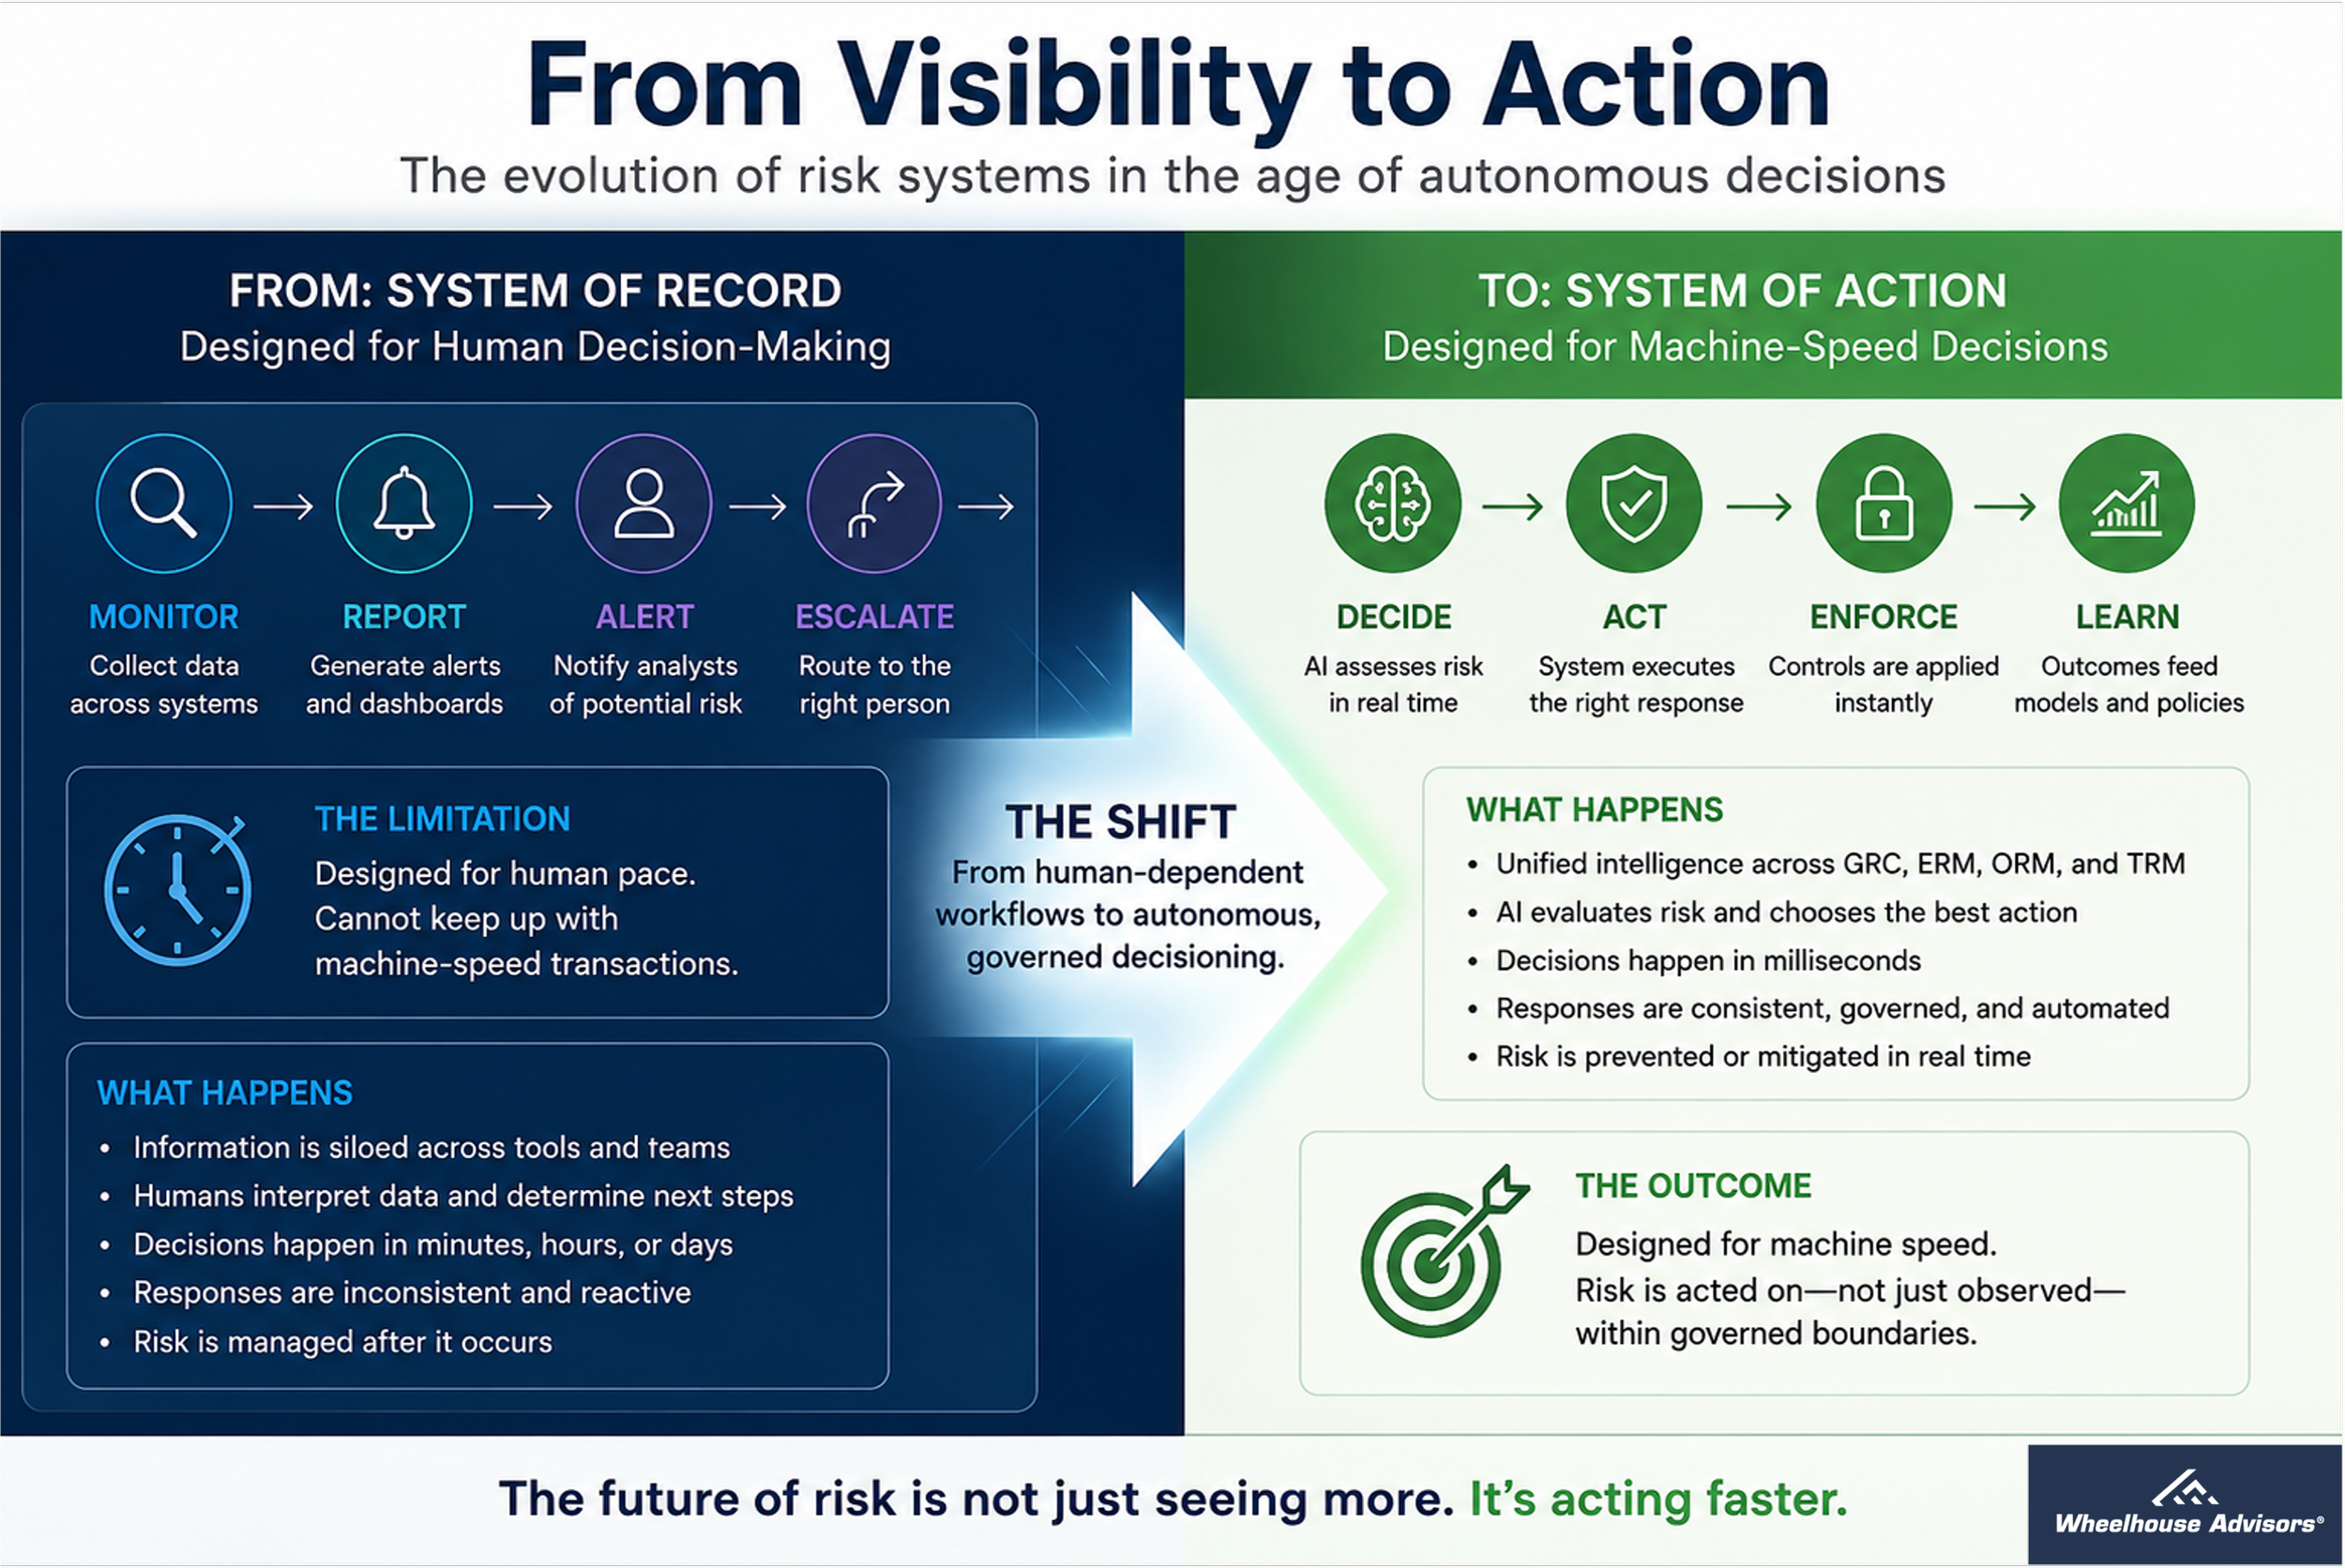
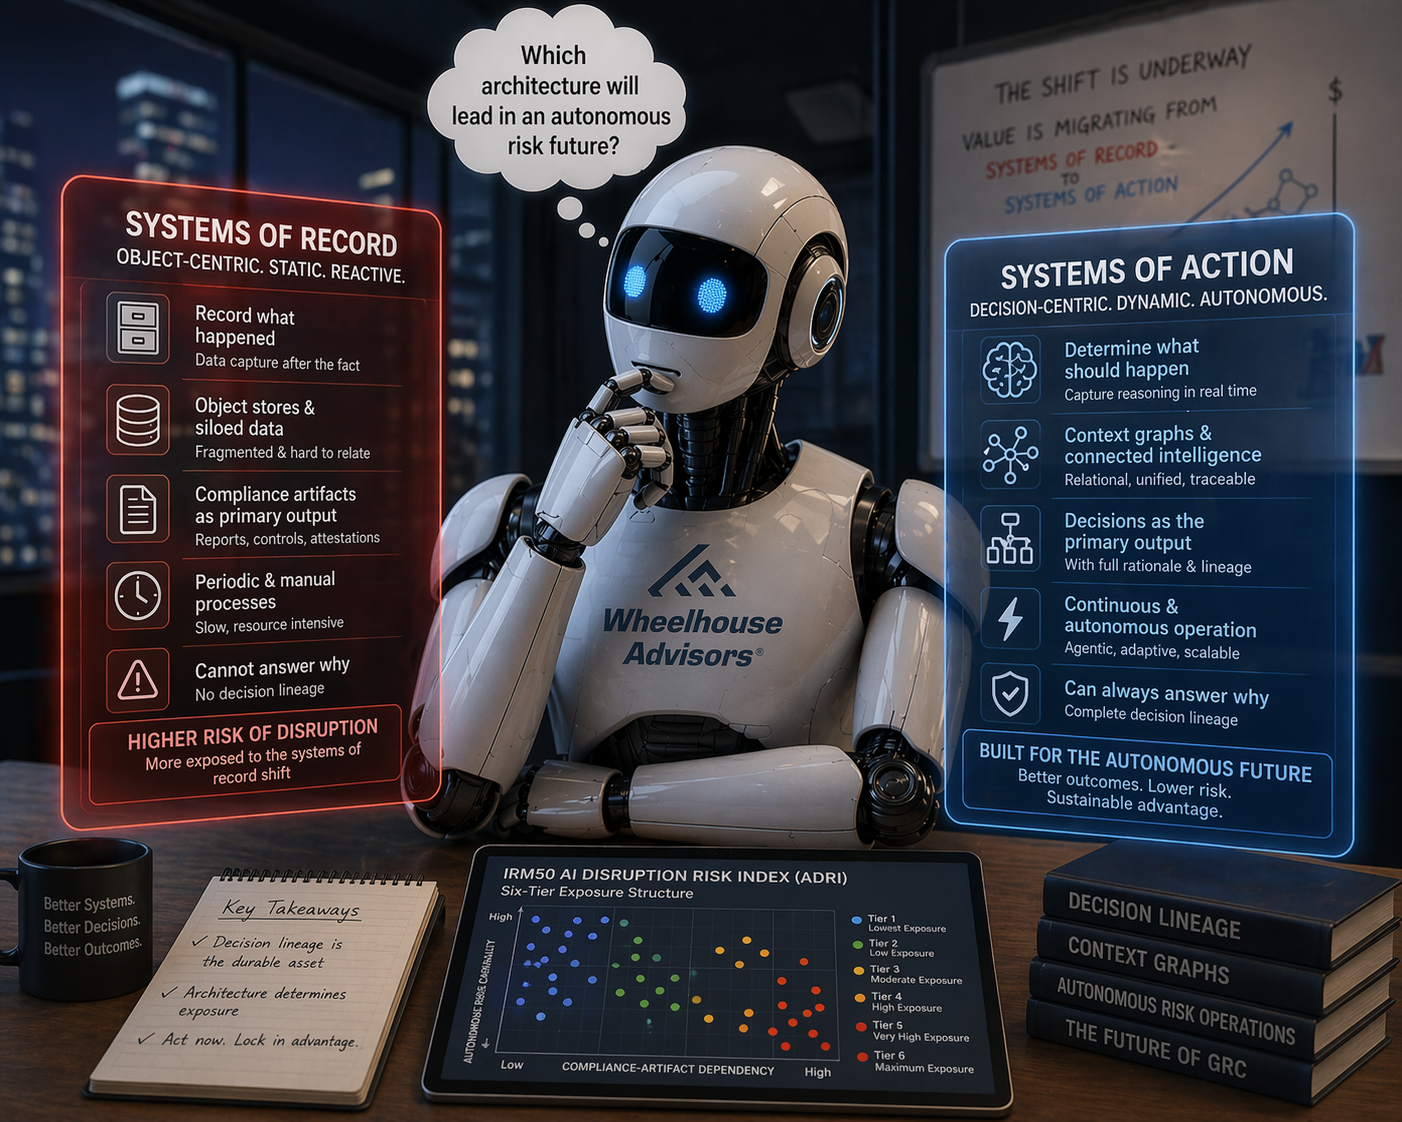
Between December 2025 and February 2026, venture commentary converged on an architectural argument: traditional systems of record are losing primacy as agentic AI takes over execution, and value is migrating from the systems that record state to the systems that capture reasoning. Sarah Wang at Andreessen Horowitz, Jamin Ball at Clouded Judgement, and Jaya Gupta and Ashu Garg at Foundation Capital each made a version of the case in pieces published within two weeks of one another.
The venture commentary drew its examples from sales, support, and finance. Those domains can tolerate lossy decision capture. Risk technology cannot. Audit, compliance, and assurance are not optional use cases bolted onto risk platforms. They are the reason the platforms exist, and each of them requires the ability to answer why something was allowed to happen.
The IRM50 AI Disruption Risk Index measures vendor-level exposure across fifty IRM and GRC platforms. The gap between tier one and tier five is not incremental. It is the difference between absorbing the shift and being absorbed by it.
What Risk Leaders Need to Know About AI Infrastructure
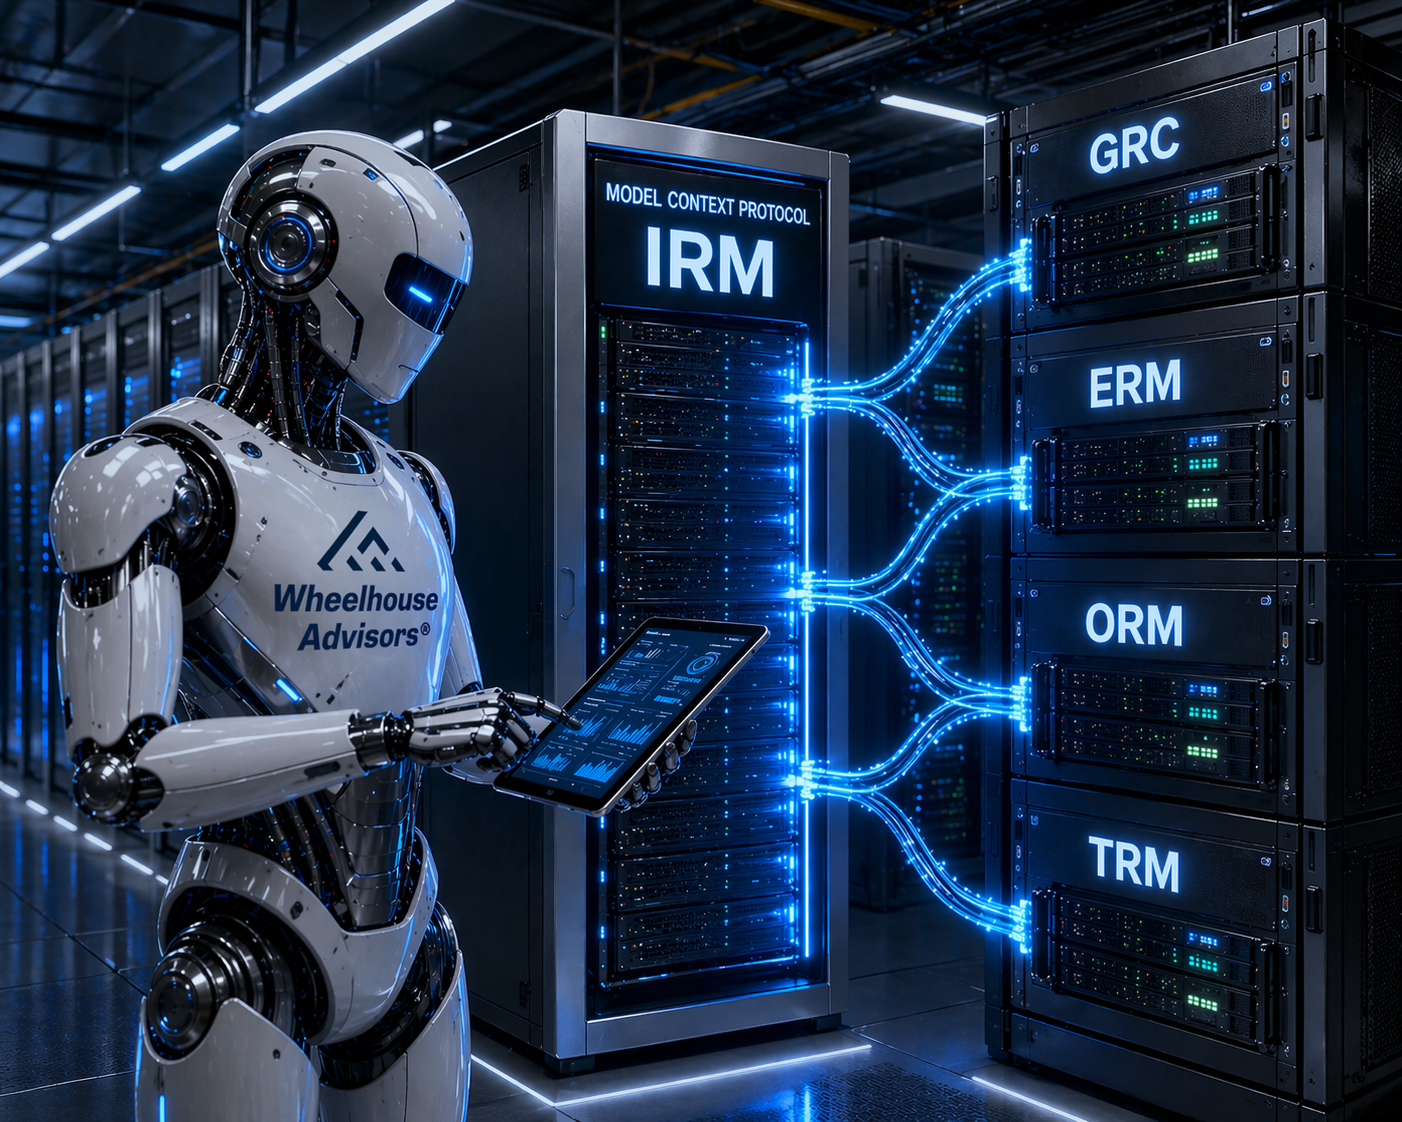
Risk leaders are sitting in vendor briefings where the presenter uses the words "agentic," "MCP," "orchestration," and "autonomous" in the same sentence, often without defining any of them. Most audiences nod along. A growing number are starting to ask harder questions. The ones who understand the infrastructure layer underneath the marketing claims are getting better answers.
This is not a technology article. It is a procurement and governance article. The AI infrastructure concepts that matter for risk leaders are not technical curiosities. They determine whether a vendor's agentic AI claims are architecturally real or a chat interface with a new label. They determine whether your organization's AI agents will operate within auditable guardrails or outside them. And they determine how exposed your technology investments are as AI reshapes the economics of risk and compliance delivery.
This article tells you what you need to know.
Chasing the Certificate: How AI Hype Is Putting Vendors, Buyers, and Investors at Risk
The Agentic GRC market has a sequencing problem. AI agents that autonomously collect evidence, monitor controls, and generate audit-ready documentation are real capabilities, and they are being deployed at scale before the compliance programs underneath them are mature enough to make them trustworthy.
The Delve case, in which a Y Combinator-backed platform allegedly let its agents generate auditor conclusions rather than supporting independent auditors who drew their own, is the most visible proof point of that dynamic. But the more important question is not what Delve did. It is what conditions made it possible, and whether those conditions are specific to one startup or structural to the segment.
Who is responsible when an Agentic GRC platform collapses the auditor-client boundary?
What does a buyer's procurement process need to ask to detect that collapse before it produces legal exposure?
And what does investment diligence look like for a platform category where the core product is trust itself?
The IRM Navigator Curve, developed by Wheelhouse Advisors, establishes that Foundational program integrity is not optional preparation for agentic deployment. It is the architectural prerequisite without which agentic compliance capabilities are structurally unstable.
The IRM50 AI Disruption Risk Index provides the second dimension: a structured framework for evaluating which platforms in the compliance automation segment are built on durable integrity architecture and which are carrying the kind of artifact-production dependency that the Delve allegations represent at their extreme.
This article examines the Delve case through both lenses, raises the specific questions each constituency needs to answer, and explains why the AI disruption frenzy has made all of them harder to ask and more expensive to ignore.