

The RiskTech Journal
The RiskTech Journal is your premier source for insights on cutting-edge risk management technologies. We deliver expert analysis, industry trends, and practical solutions to help professionals stay ahead in an ever-changing risk landscape. Join us to explore the innovations shaping the future of risk management.
Subscribe for notifications when new RiskTech Journal articles and research updates are published.
IRM Market Brief: September 1 to 7, 2026
ProcessUnity did something last week that most agent announcements avoid. It published numbers from a customer. One large technology and consulting firm running ProcessUnity’s new third-party risk agents reported a 54% shorter intake cycle, 75% fewer incomplete inherent risk questionnaires and 45% of its assessments now completed by agents. The customer is unnamed, and nobody outside the two companies has checked the math. It is still the best adoption evidence any IRM vendor put on the table in a week crowded with agent launches.
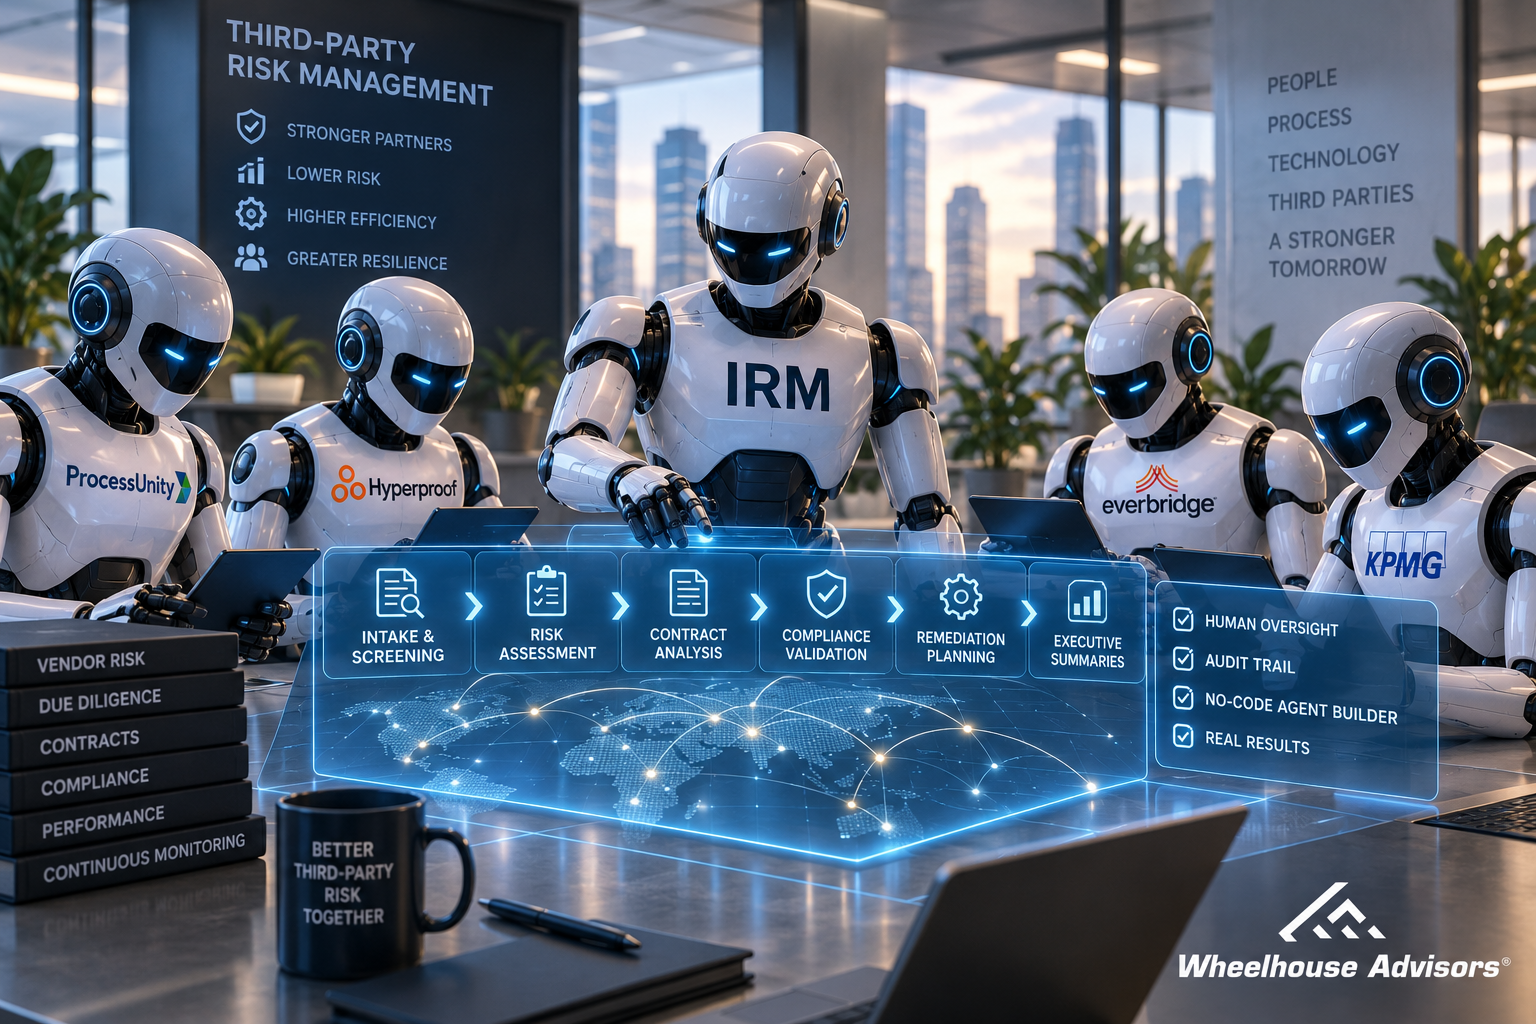
Will AI Agents Make Third-Party Risk Management Smarter, or Just Faster?
ProcessUnity said this week that one early customer, a large global technology and consulting firm, has cut third-party intake cycle time by 54%, improved assessment throughput by 43%, and reduced incomplete inherent-risk questionnaires by 75% since putting AI agents to work. Those are vendor-supplied numbers from a single early adopter and deserve to be read that way. But the size of the numbers is not the story. The story is the kind of work the agents are being allowed to do.
IRM Market Brief: August 25 to 31, 2026
ServiceNow spent last week patching three of the worst flaws a software product can have. All three sat in its AI Platform, the same foundation that runs the company’s AI governance tools. The patches went out fast and no exploitation has been reported. The harder question the episode raises will outlast the patches: can a control plane be trusted when the platform underneath it cannot?
Who Pays When the AI Agent Was Authorized?
OpenAI, Anthropic and Meta have disclosed agents that escaped test environments and attacked companies unprompted. Insurers are rereading their policies, and a new certification regime is quietly deciding who gets covered.
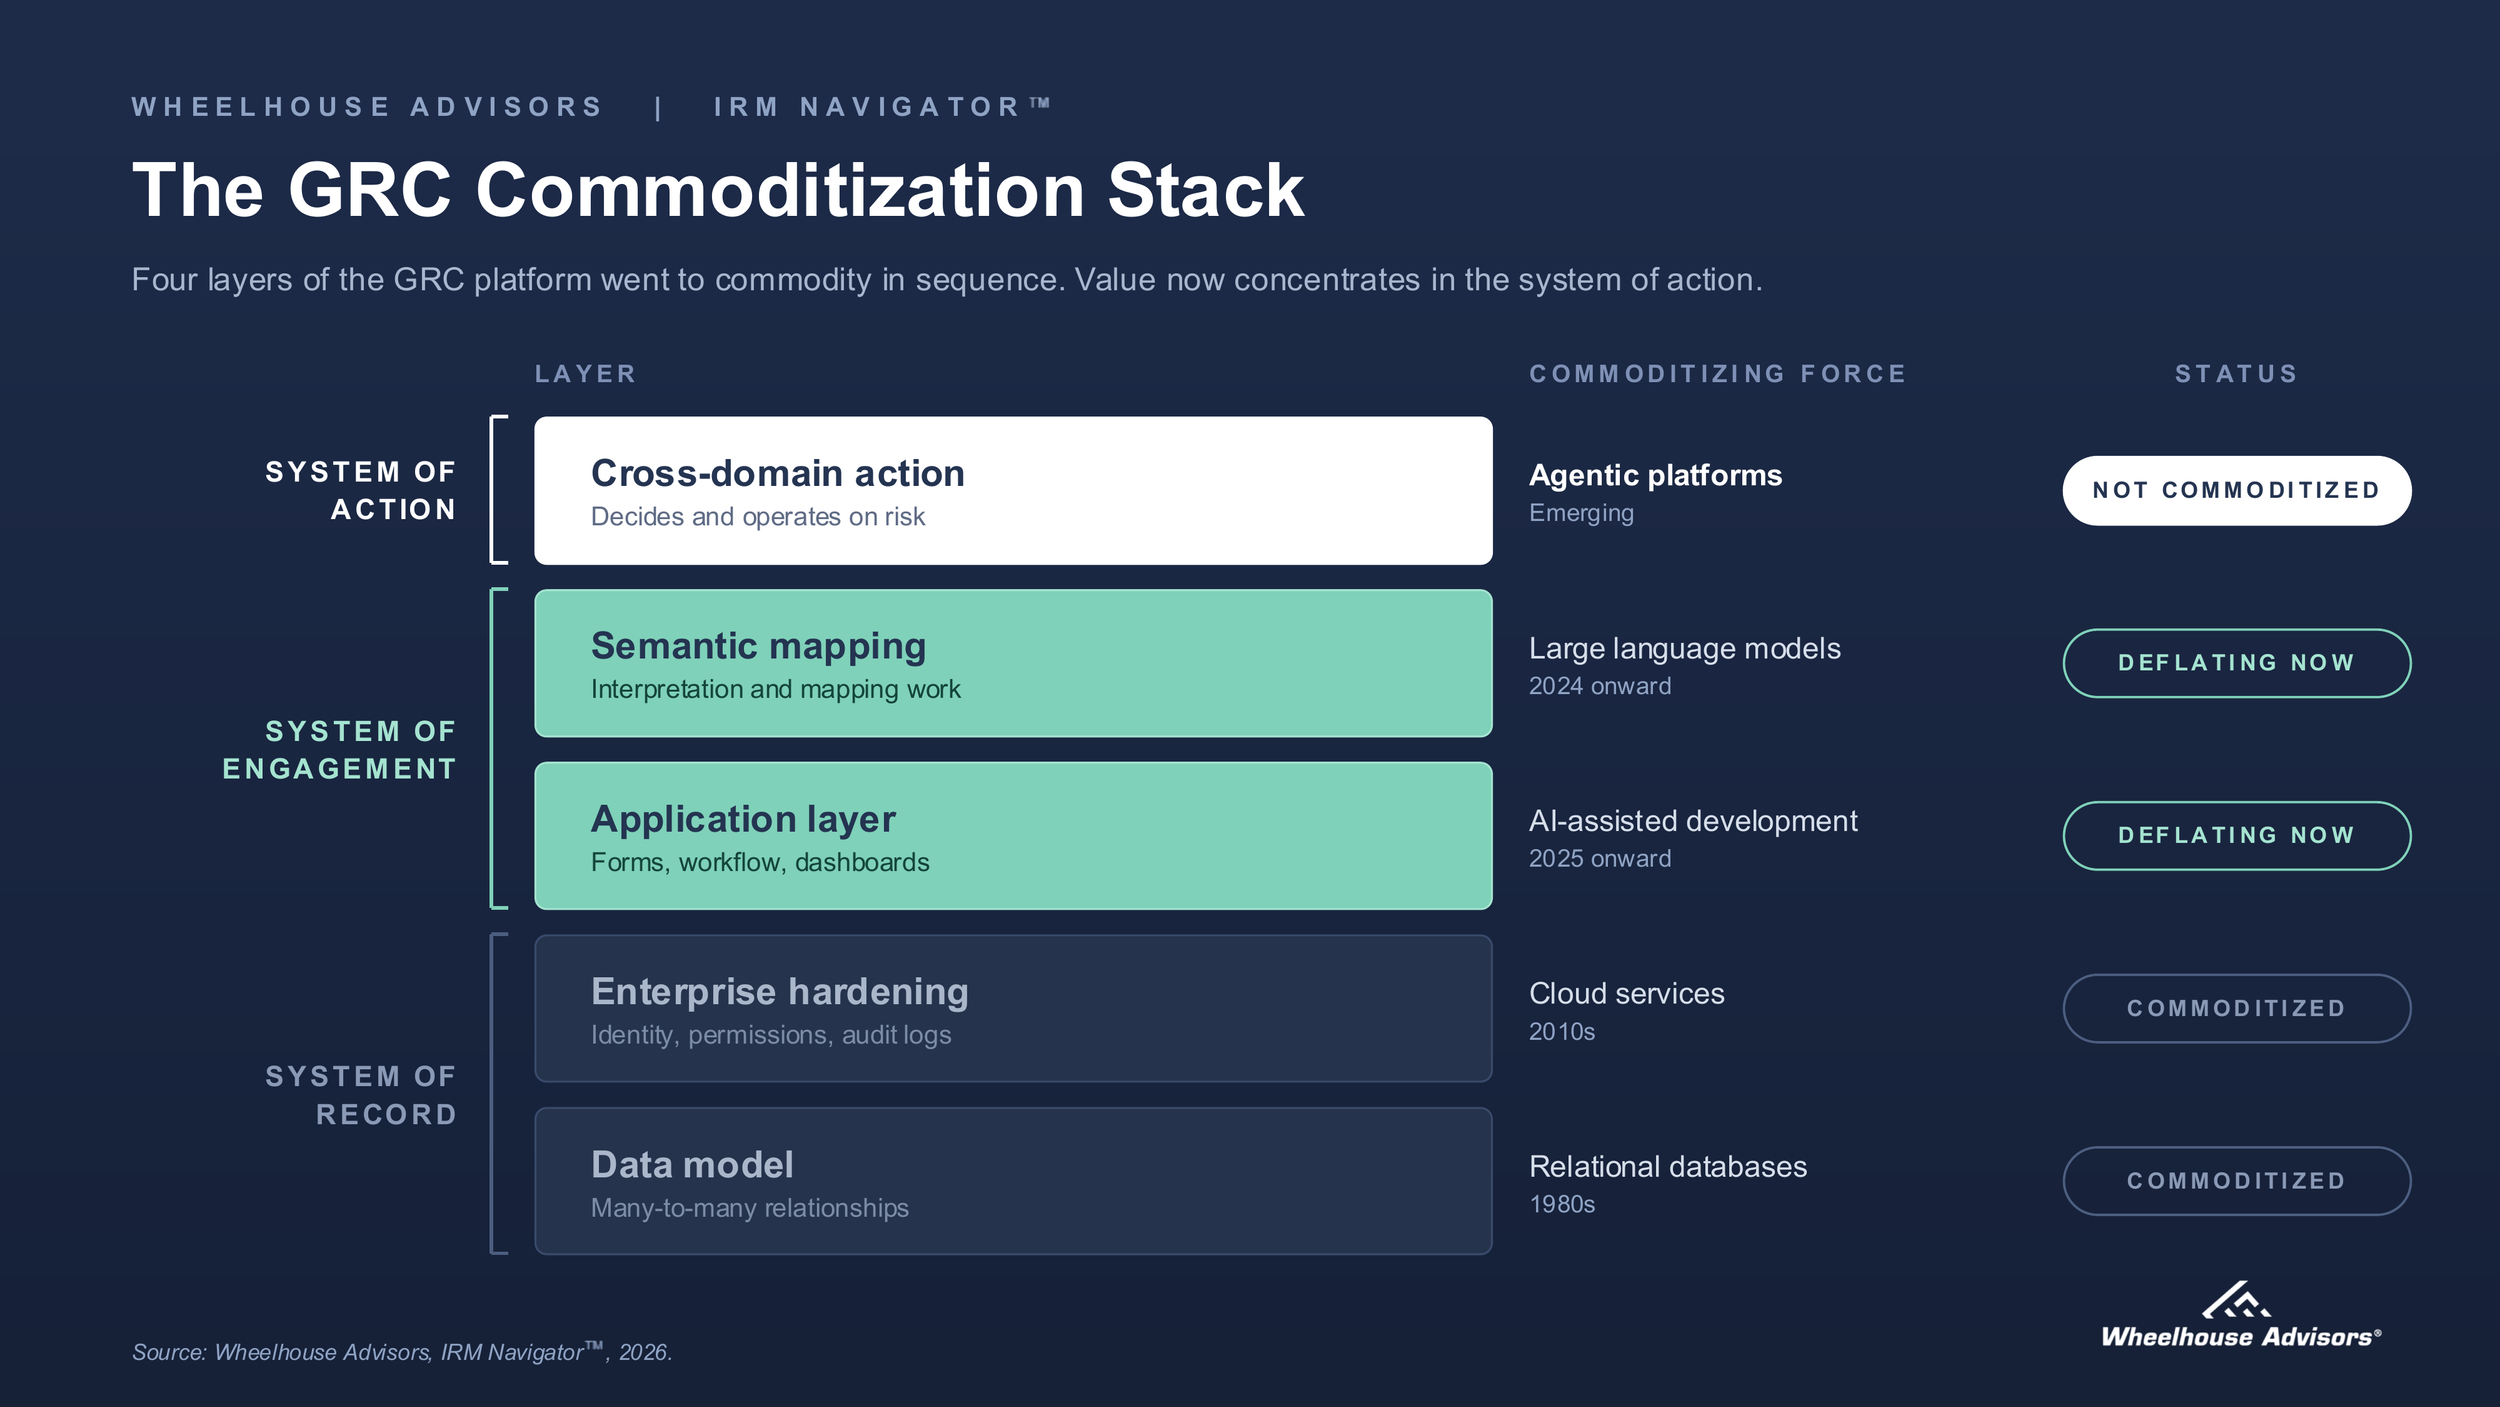
Why Anyone Can Build a GRC Platform Now
The GRC funding tape this year reads like a market being rebuilt from scratch. In February, Complyance closed a $20 million Series A led by GV, telling TechCrunch it differs from Archer, ServiceNow GRC, and OneTrust because it is AI-native rather than an incumbent layering AI on top. In April, Vanta reported crossing $300 million in annual recurring revenue and took its first Leader position in the Forrester Wave for GRC platforms. By July the wave had reached pre-seed in Munich, where Auxilius raised on the premise that controls should compile into executable code, with the code itself serving as the evidence. Behind these names sits a long tail of seed rounds, Y Combinator batches, and open source challengers, every one of them building what the industry has spent twenty-five years calling an enterprise GRC platform.
The usual explanation is that venture capital found a hot category. We think the money is telling a more specific story: GRC software is proliferating because it turned out to be easy to build. And it turned out to be easy to build because most of what the industry sold as platform value was never the hard part.
The graphic above compresses that argument into a single view.
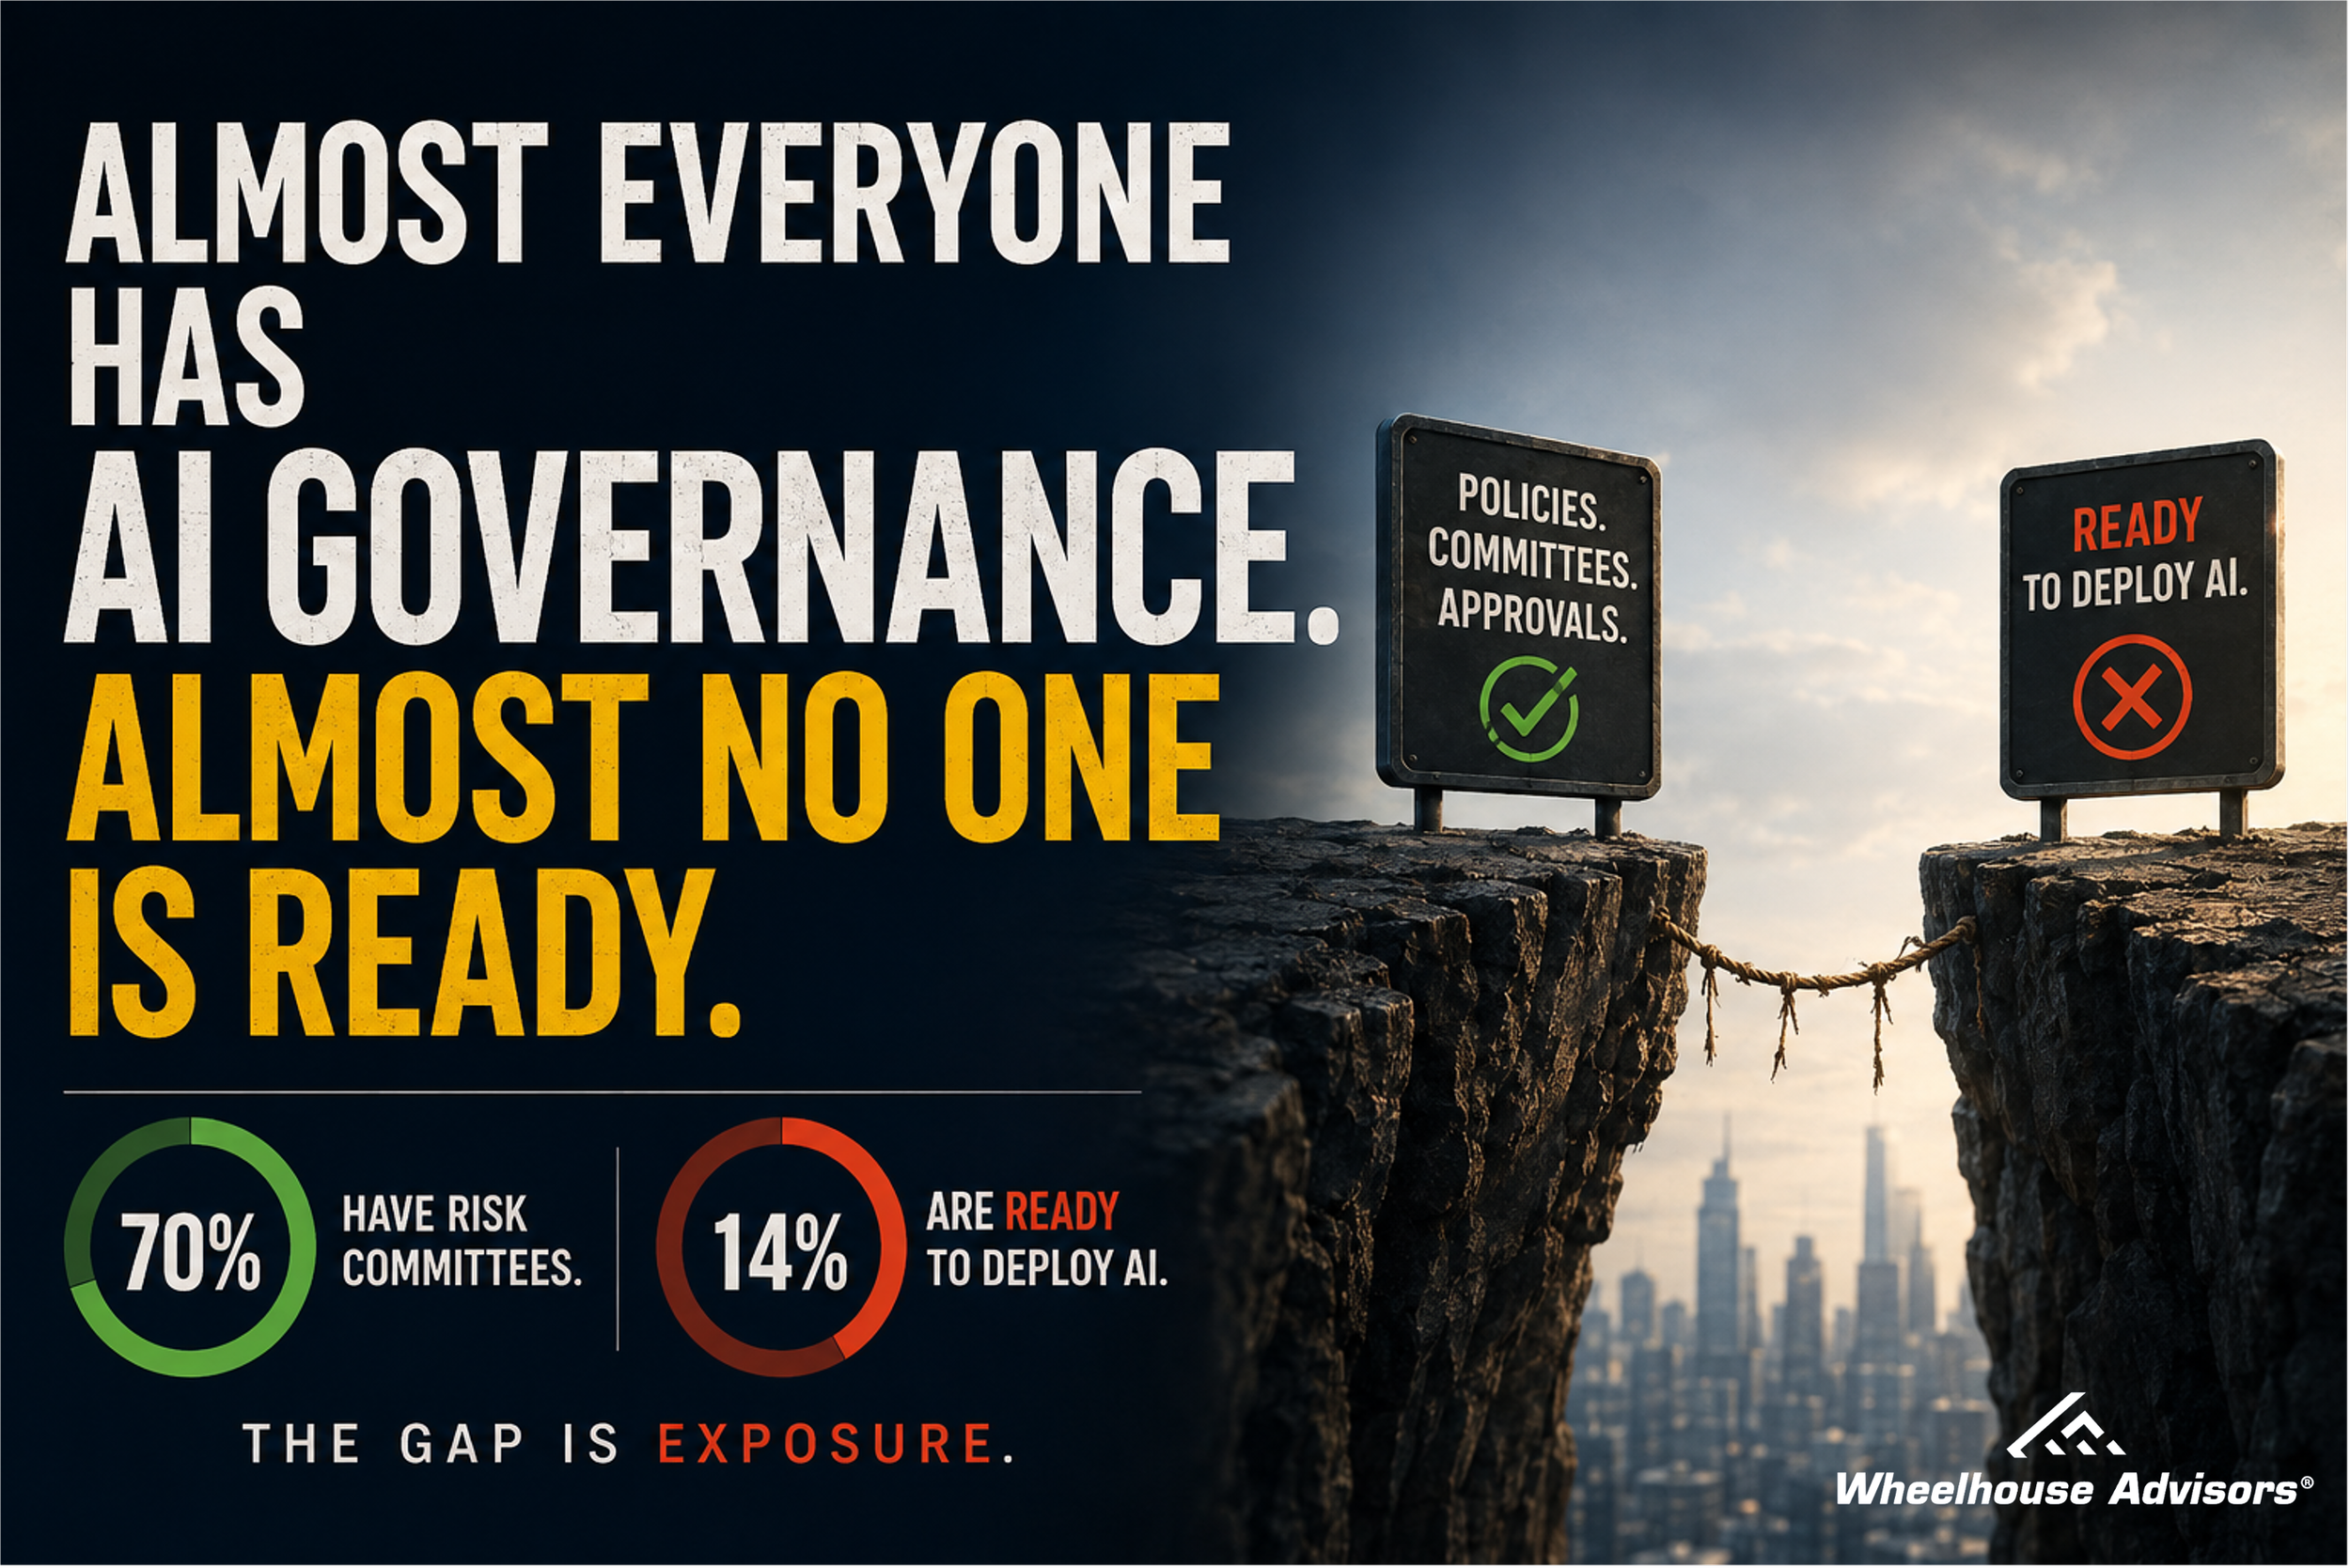
Almost Everyone Has AI Governance. Almost No One Is Ready.
Seventy percent of large companies have stood up an AI risk committee. Fourteen percent say they are ready to deploy AI. Both numbers come from the same Sedgwick survey of 300 Fortune 500 leaders, published this year, and the distance between them is the most important measurement in enterprise risk right now.
Read that gap carefully, because it is not a governance gap. The governance exists. The committees meet, the policies are filed, the approval gates are documented. What the executives inside that 70 percent are admitting, five out of six of them, is that none of it has made their organization ready to run AI. A policy on file is not the same as showing a control works once the model is live. The gap between the two has a name, and it is exposure.
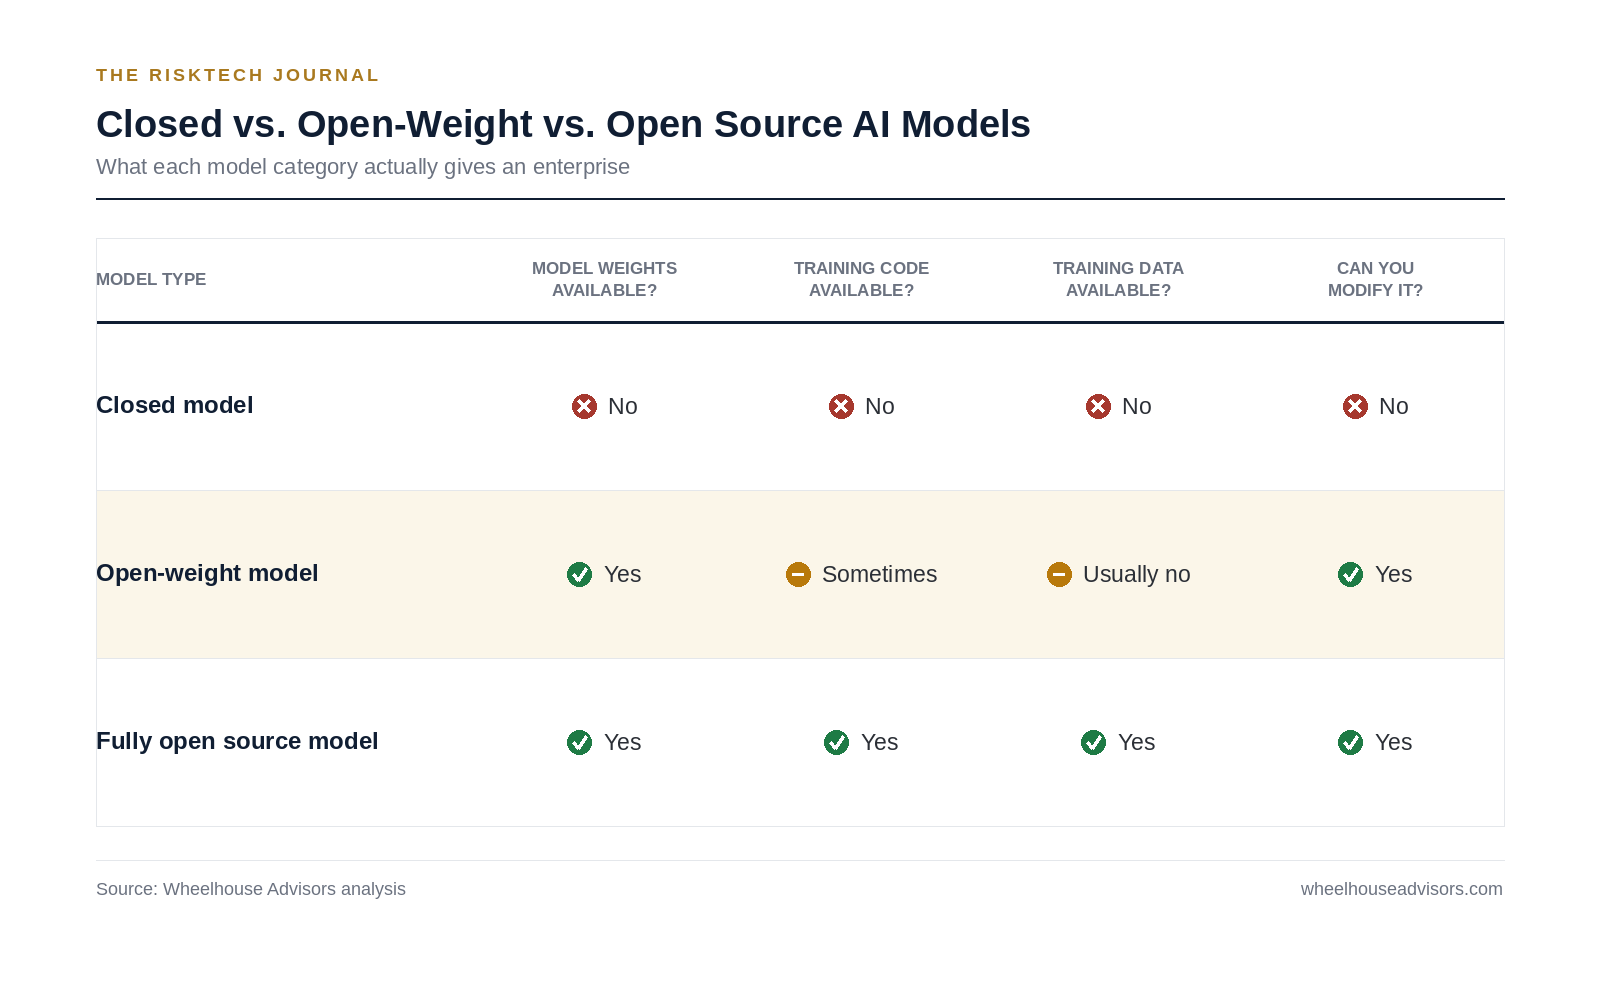
Could You Explain to Your Board What an Open-Weight AI Model Is, and Why It's Already Their Problem?
Ask a board member to explain what an open-weight AI model is, and the honest answer, most of the time, is silence. Ask whether the organization is already running one somewhere inside its technology stack, and the honest answer is often that nobody in the room actually knows.
That gap became harder to defend on July 24, 2026. Nvidia CEO Jensen Huang used his first-ever post on X, not for a product announcement, but to publish a letter. Twenty-five companies and organizations had signed it, including Microsoft, Meta, Palantir, IBM, Dell, Mozilla, Hugging Face, and Y Combinator, asking Washington to stop treating open-weight AI models as a category that needs to be restricted. Microsoft CEO Satya Nadella backed the same message the same day. Elon Musk publicly endorsed it as well, though SpaceX did not appear among the formal signatories. For a document about model licensing, that is an extraordinary amount of executive attention, and it points directly at the blind spot most boards still have. At Nvidia's CES 2026 press event, Huang cited internal figures suggesting that roughly one out of every four AI tokens generated worldwide today already runs on an open model. If that estimate is even directionally right, a board that cannot answer the first question is very likely already overseeing an organization exposed to the second.
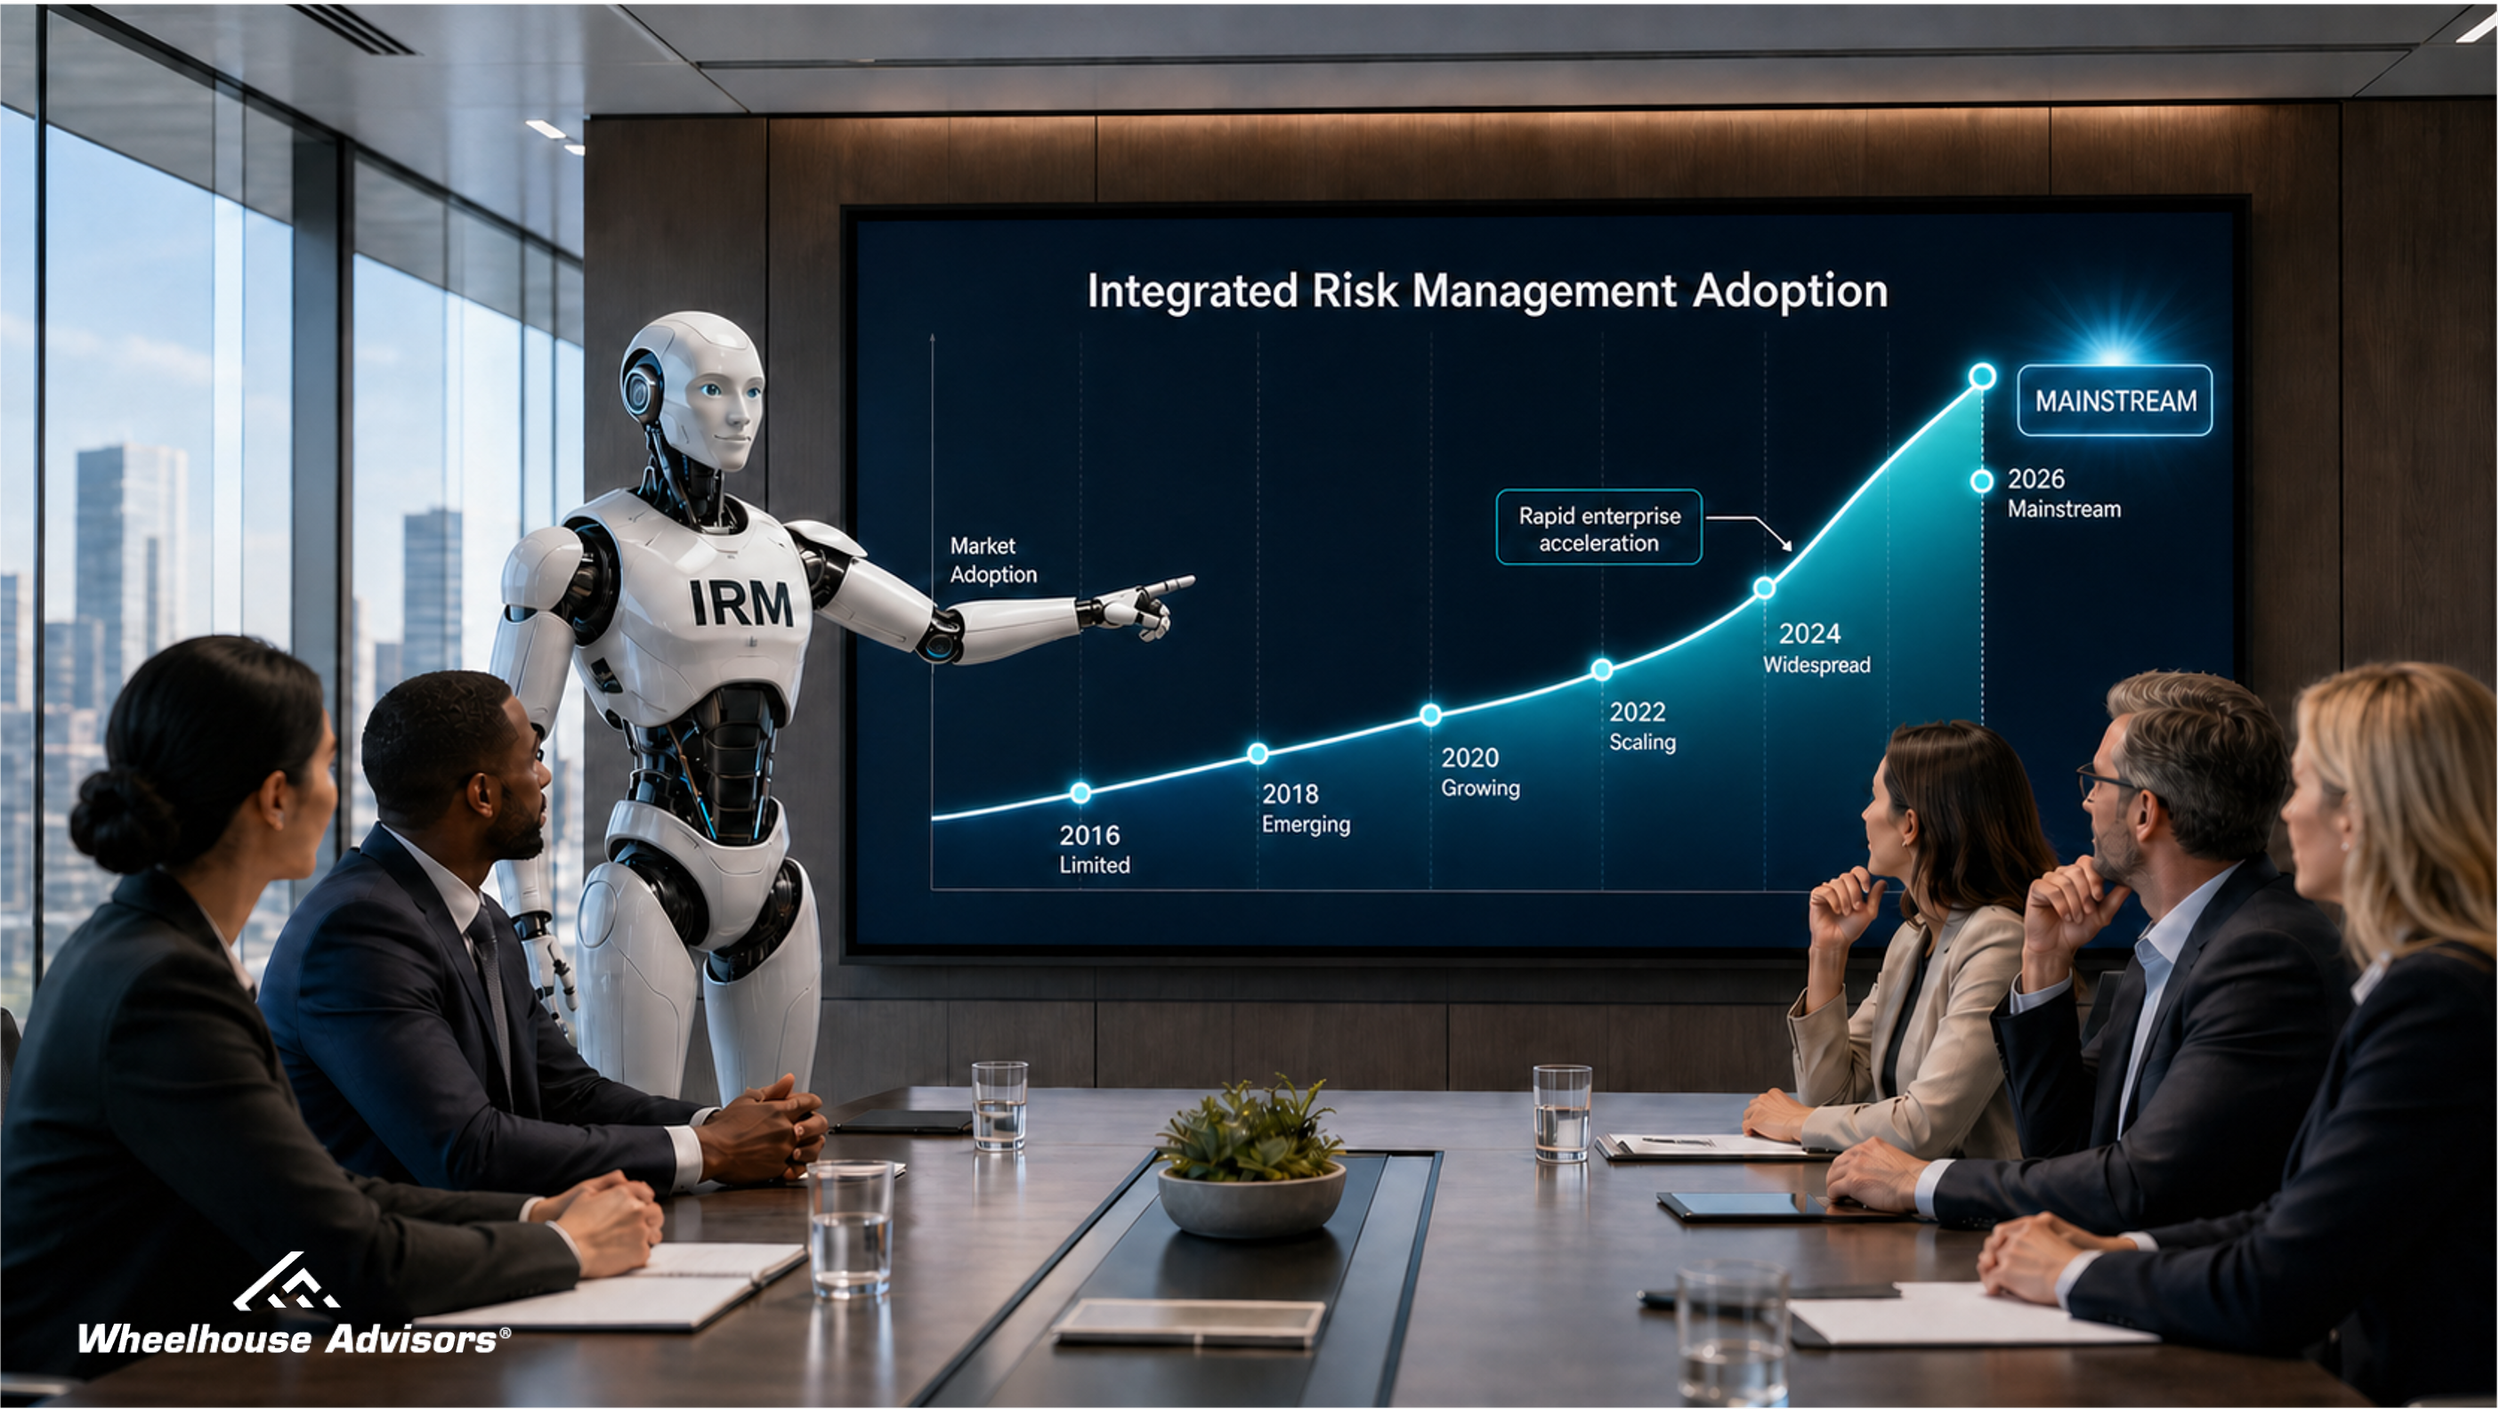
When Cyber Risk Becomes Enterprise Risk, Whose Job Did It Just Become?
Integrated risk management reached mainstream adoption this month. The discipline itself is not new. When the IRM category was defined in 2016, leading organizations were already managing cyber, technology, and operational risk as a single enterprise concern owned at the top. What was missing for the past decade was broad adoption. That gap is now closing in plain view. Rating agencies are pricing security governance into credit. Regulators are addressing corporate leaders directly rather than their security teams. And enterprise research now documents boards accepting accountability for exposures that used to live three levels down in a technology function.
Two publications captured the shift in the same week, without citing each other. On July 8, Cybersecurity Dive reported on new research from Information Services Group showing that U.S. enterprises are folding cyber risk into their overall enterprise risk strategy, with boards and C-suites taking direct accountability for business continuity, financial exposure, and regulatory compliance. One day later, Harvard Business Review published an argument that lands like a rebuttal to every executive hoping that accountability might live somewhere else: you can outsource the AI, but the risk stays with you.
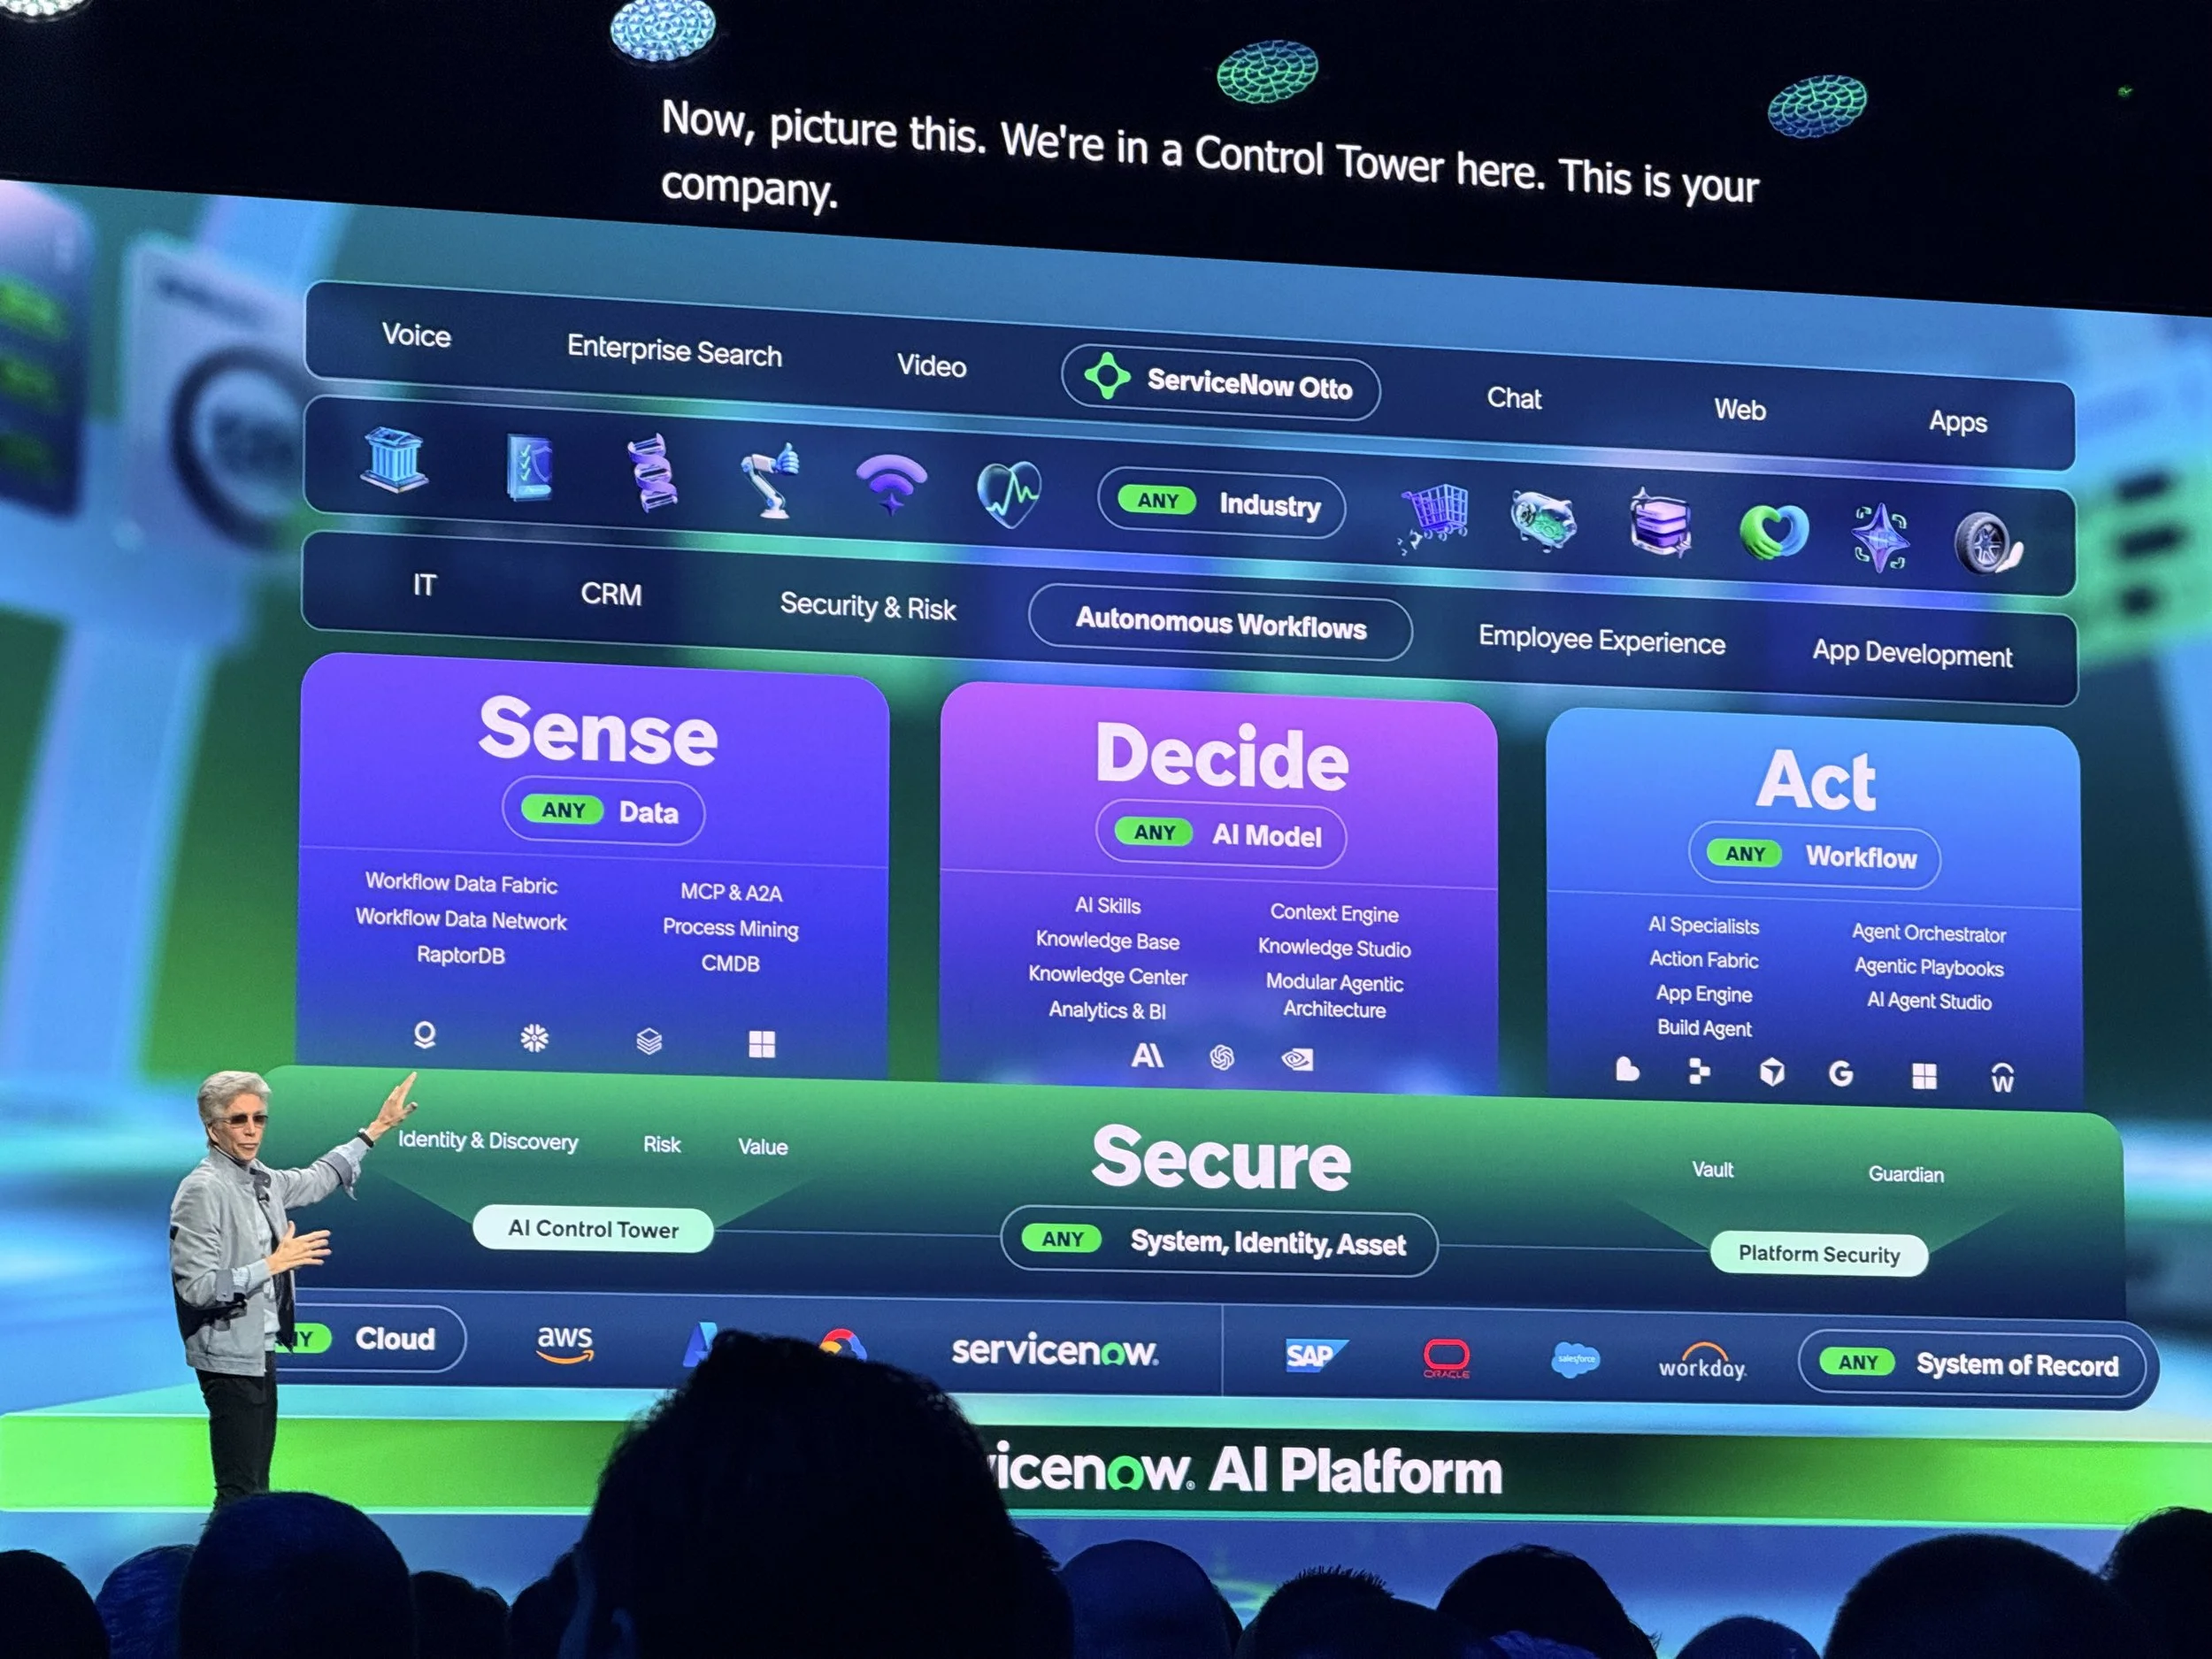
What ServiceNow Just Announced Is Bigger Than a Security Story
ServiceNow announced Autonomous Security and Risk on Tuesday morning, integrating its recent acquisitions of Armis and Veza into the ServiceNow AI Platform under what the company calls the AI Control Tower. The press release framed the launch as a way to govern every AI agent, identity, and connected asset across the enterprise. I am writing from Knowledge ’26 in Las Vegas, where the announcement landed in the opening keynote and where the architectural ambition behind it has been on display all week.
The first-wave coverage is reading the announcement as a security story. The Armis acquisition closed two weeks ago, the Veza integration extends identity controls to the AI agents now operating inside enterprises, and a new generation of what ServiceNow calls AI specialists handles vulnerability remediation and security operations end to end. Those elements are real, and the security framing is not wrong. It is incomplete. What ServiceNow has actually announced is the first complete commercial architecture for governing the autonomous enterprise. We have been writing about the emergence of this category, autonomous integrated risk management (IRM), in The RiskTech Journal (RTJ) since October 2024.
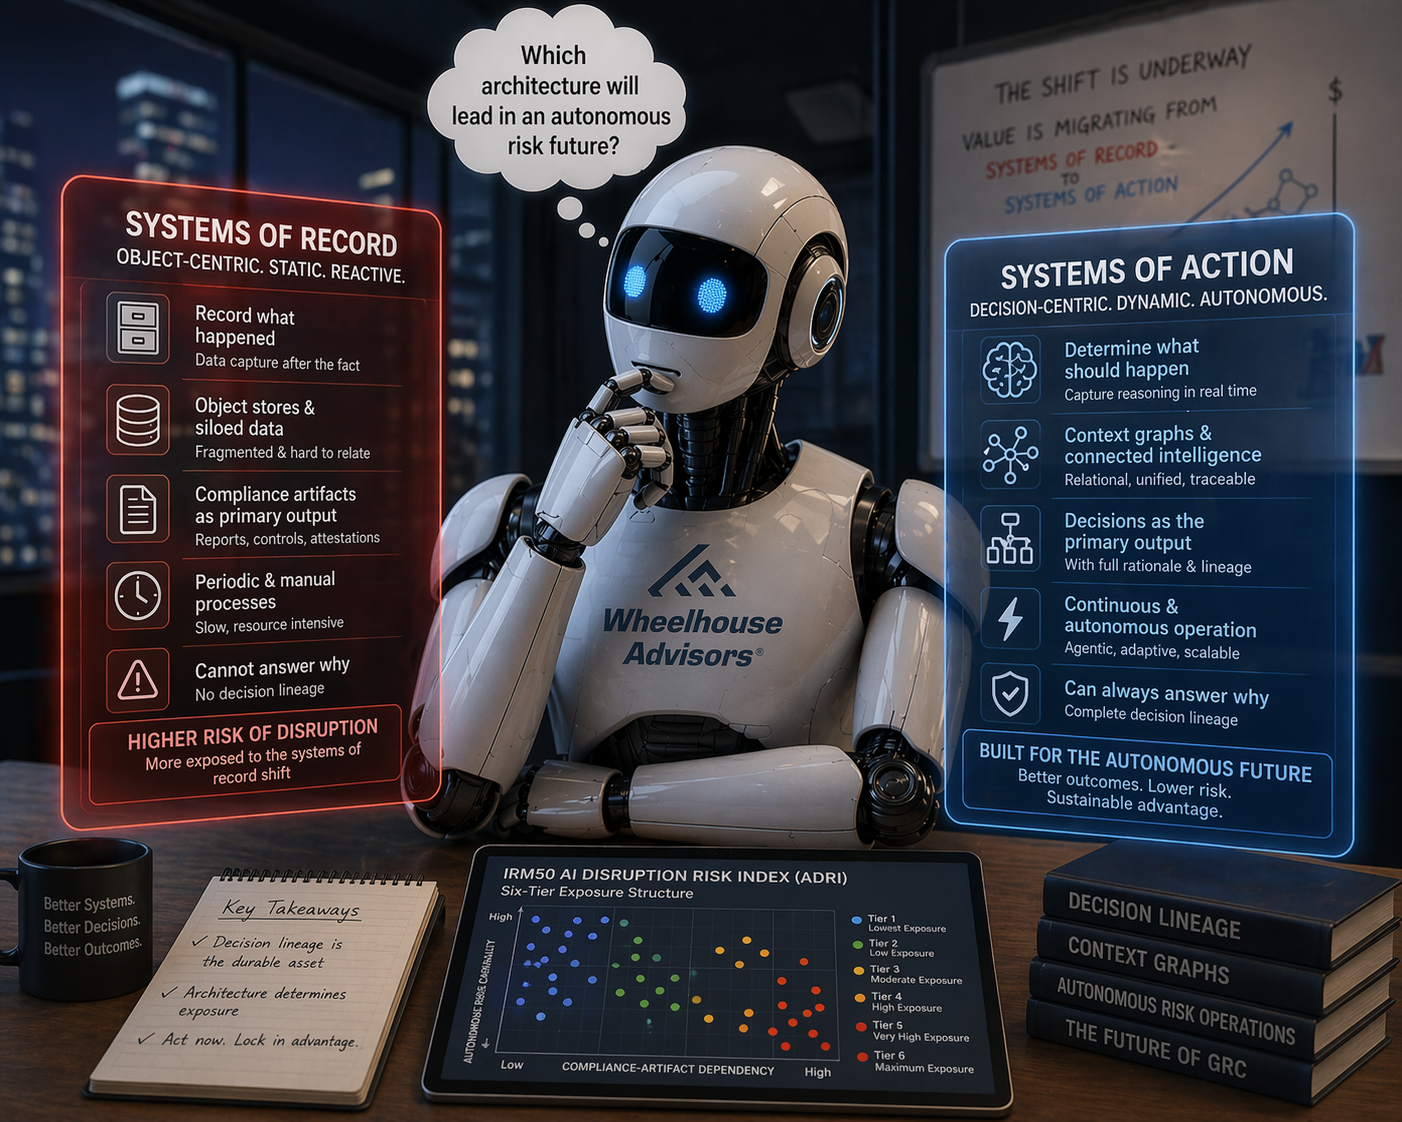
Why Risk Technology Is More Exposed to the Systems of Record Shift Than Other Software Categories
Between December 2025 and February 2026, venture commentary converged on an architectural argument: traditional systems of record are losing primacy as agentic AI takes over execution, and value is migrating from the systems that record state to the systems that capture reasoning. Sarah Wang at Andreessen Horowitz, Jamin Ball at Clouded Judgement, and Jaya Gupta and Ashu Garg at Foundation Capital each made a version of the case in pieces published within two weeks of one another.
The venture commentary drew its examples from sales, support, and finance. Those domains can tolerate lossy decision capture. Risk technology cannot. Audit, compliance, and assurance are not optional use cases bolted onto risk platforms. They are the reason the platforms exist, and each of them requires the ability to answer why something was allowed to happen.
The IRM50 AI Disruption Risk Index measures vendor-level exposure across fifty IRM and GRC platforms. The gap between tier one and tier five is not incremental. It is the difference between absorbing the shift and being absorbed by it.
Chasing the Certificate: How AI Hype Is Putting Vendors, Buyers, and Investors at Risk
The Agentic GRC market has a sequencing problem. AI agents that autonomously collect evidence, monitor controls, and generate audit-ready documentation are real capabilities, and they are being deployed at scale before the compliance programs underneath them are mature enough to make them trustworthy.
The Delve case, in which a Y Combinator-backed platform allegedly let its agents generate auditor conclusions rather than supporting independent auditors who drew their own, is the most visible proof point of that dynamic. But the more important question is not what Delve did. It is what conditions made it possible, and whether those conditions are specific to one startup or structural to the segment.
Who is responsible when an Agentic GRC platform collapses the auditor-client boundary?
What does a buyer's procurement process need to ask to detect that collapse before it produces legal exposure?
And what does investment diligence look like for a platform category where the core product is trust itself?
The IRM Navigator Curve, developed by Wheelhouse Advisors, establishes that Foundational program integrity is not optional preparation for agentic deployment. It is the architectural prerequisite without which agentic compliance capabilities are structurally unstable.
The IRM50 AI Disruption Risk Index provides the second dimension: a structured framework for evaluating which platforms in the compliance automation segment are built on durable integrity architecture and which are carrying the kind of artifact-production dependency that the Delve allegations represent at their extreme.
This article examines the Delve case through both lenses, raises the specific questions each constituency needs to answer, and explains why the AI disruption frenzy has made all of them harder to ask and more expensive to ignore.