

The RiskTech Journal
The RiskTech Journal is your premier source for insights on cutting-edge risk management technologies. We deliver expert analysis, industry trends, and practical solutions to help professionals stay ahead in an ever-changing risk landscape. Join us to explore the innovations shaping the future of risk management.
Subscribe for notifications when new RiskTech Journal articles and research updates are published.
IRM Market Brief: September 1 to 7, 2026
ProcessUnity did something last week that most agent announcements avoid. It published numbers from a customer. One large technology and consulting firm running ProcessUnity’s new third-party risk agents reported a 54% shorter intake cycle, 75% fewer incomplete inherent risk questionnaires and 45% of its assessments now completed by agents. The customer is unnamed, and nobody outside the two companies has checked the math. It is still the best adoption evidence any IRM vendor put on the table in a week crowded with agent launches.
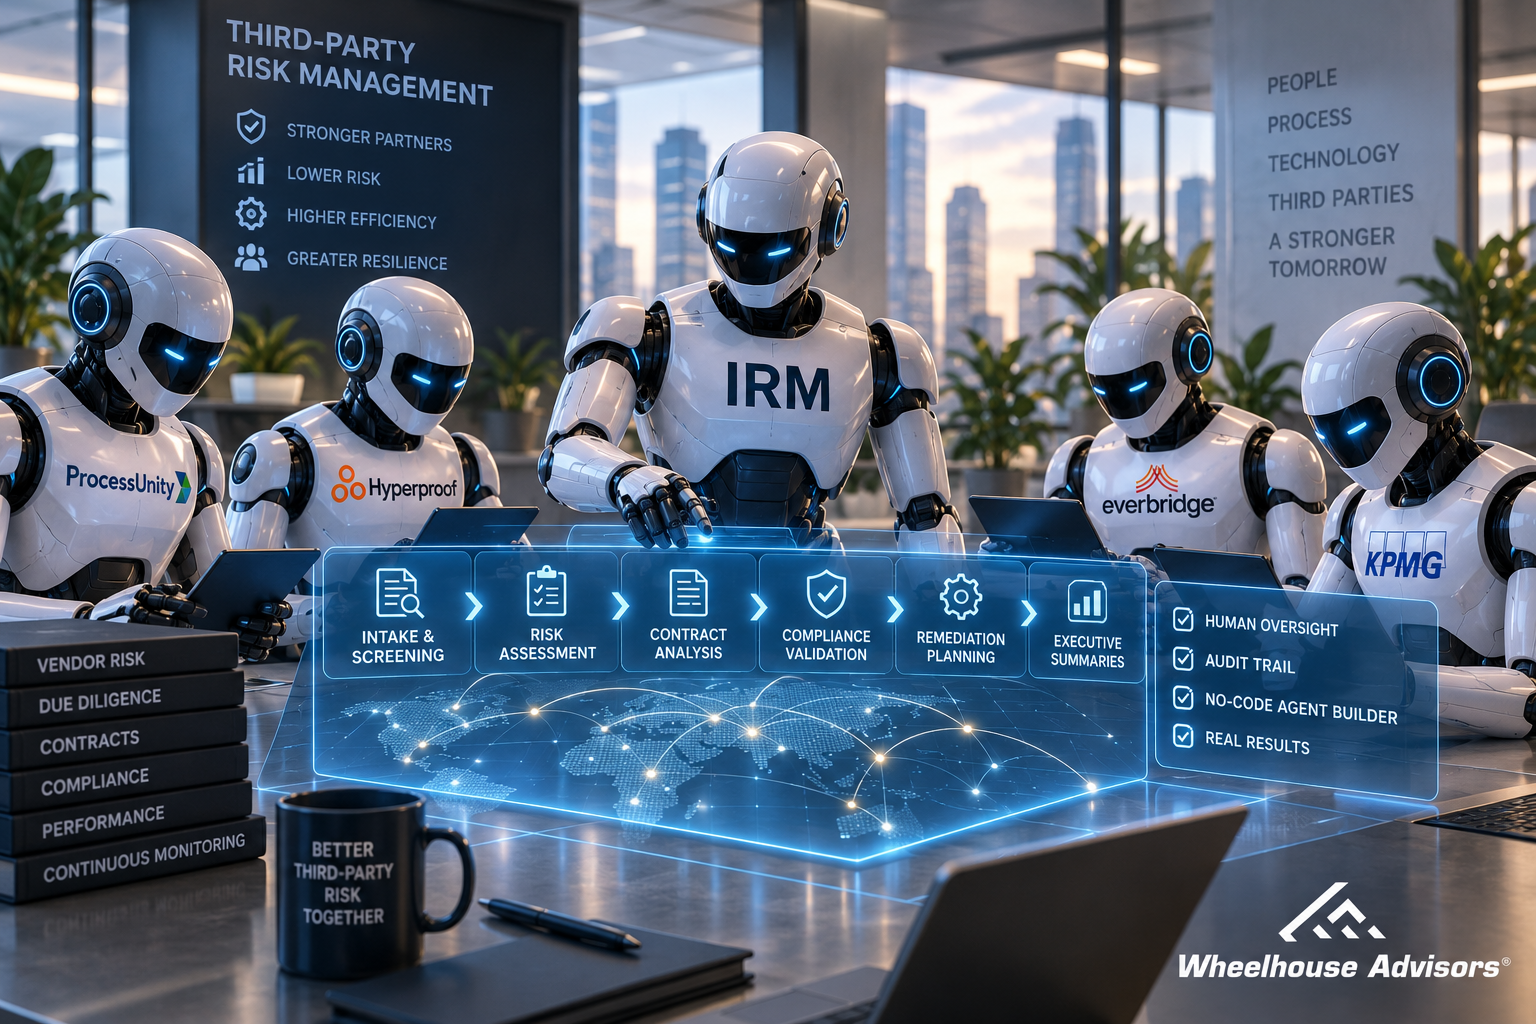
Will AI Agents Make Third-Party Risk Management Smarter, or Just Faster?
ProcessUnity said this week that one early customer, a large global technology and consulting firm, has cut third-party intake cycle time by 54%, improved assessment throughput by 43%, and reduced incomplete inherent-risk questionnaires by 75% since putting AI agents to work. Those are vendor-supplied numbers from a single early adopter and deserve to be read that way. But the size of the numbers is not the story. The story is the kind of work the agents are being allowed to do.
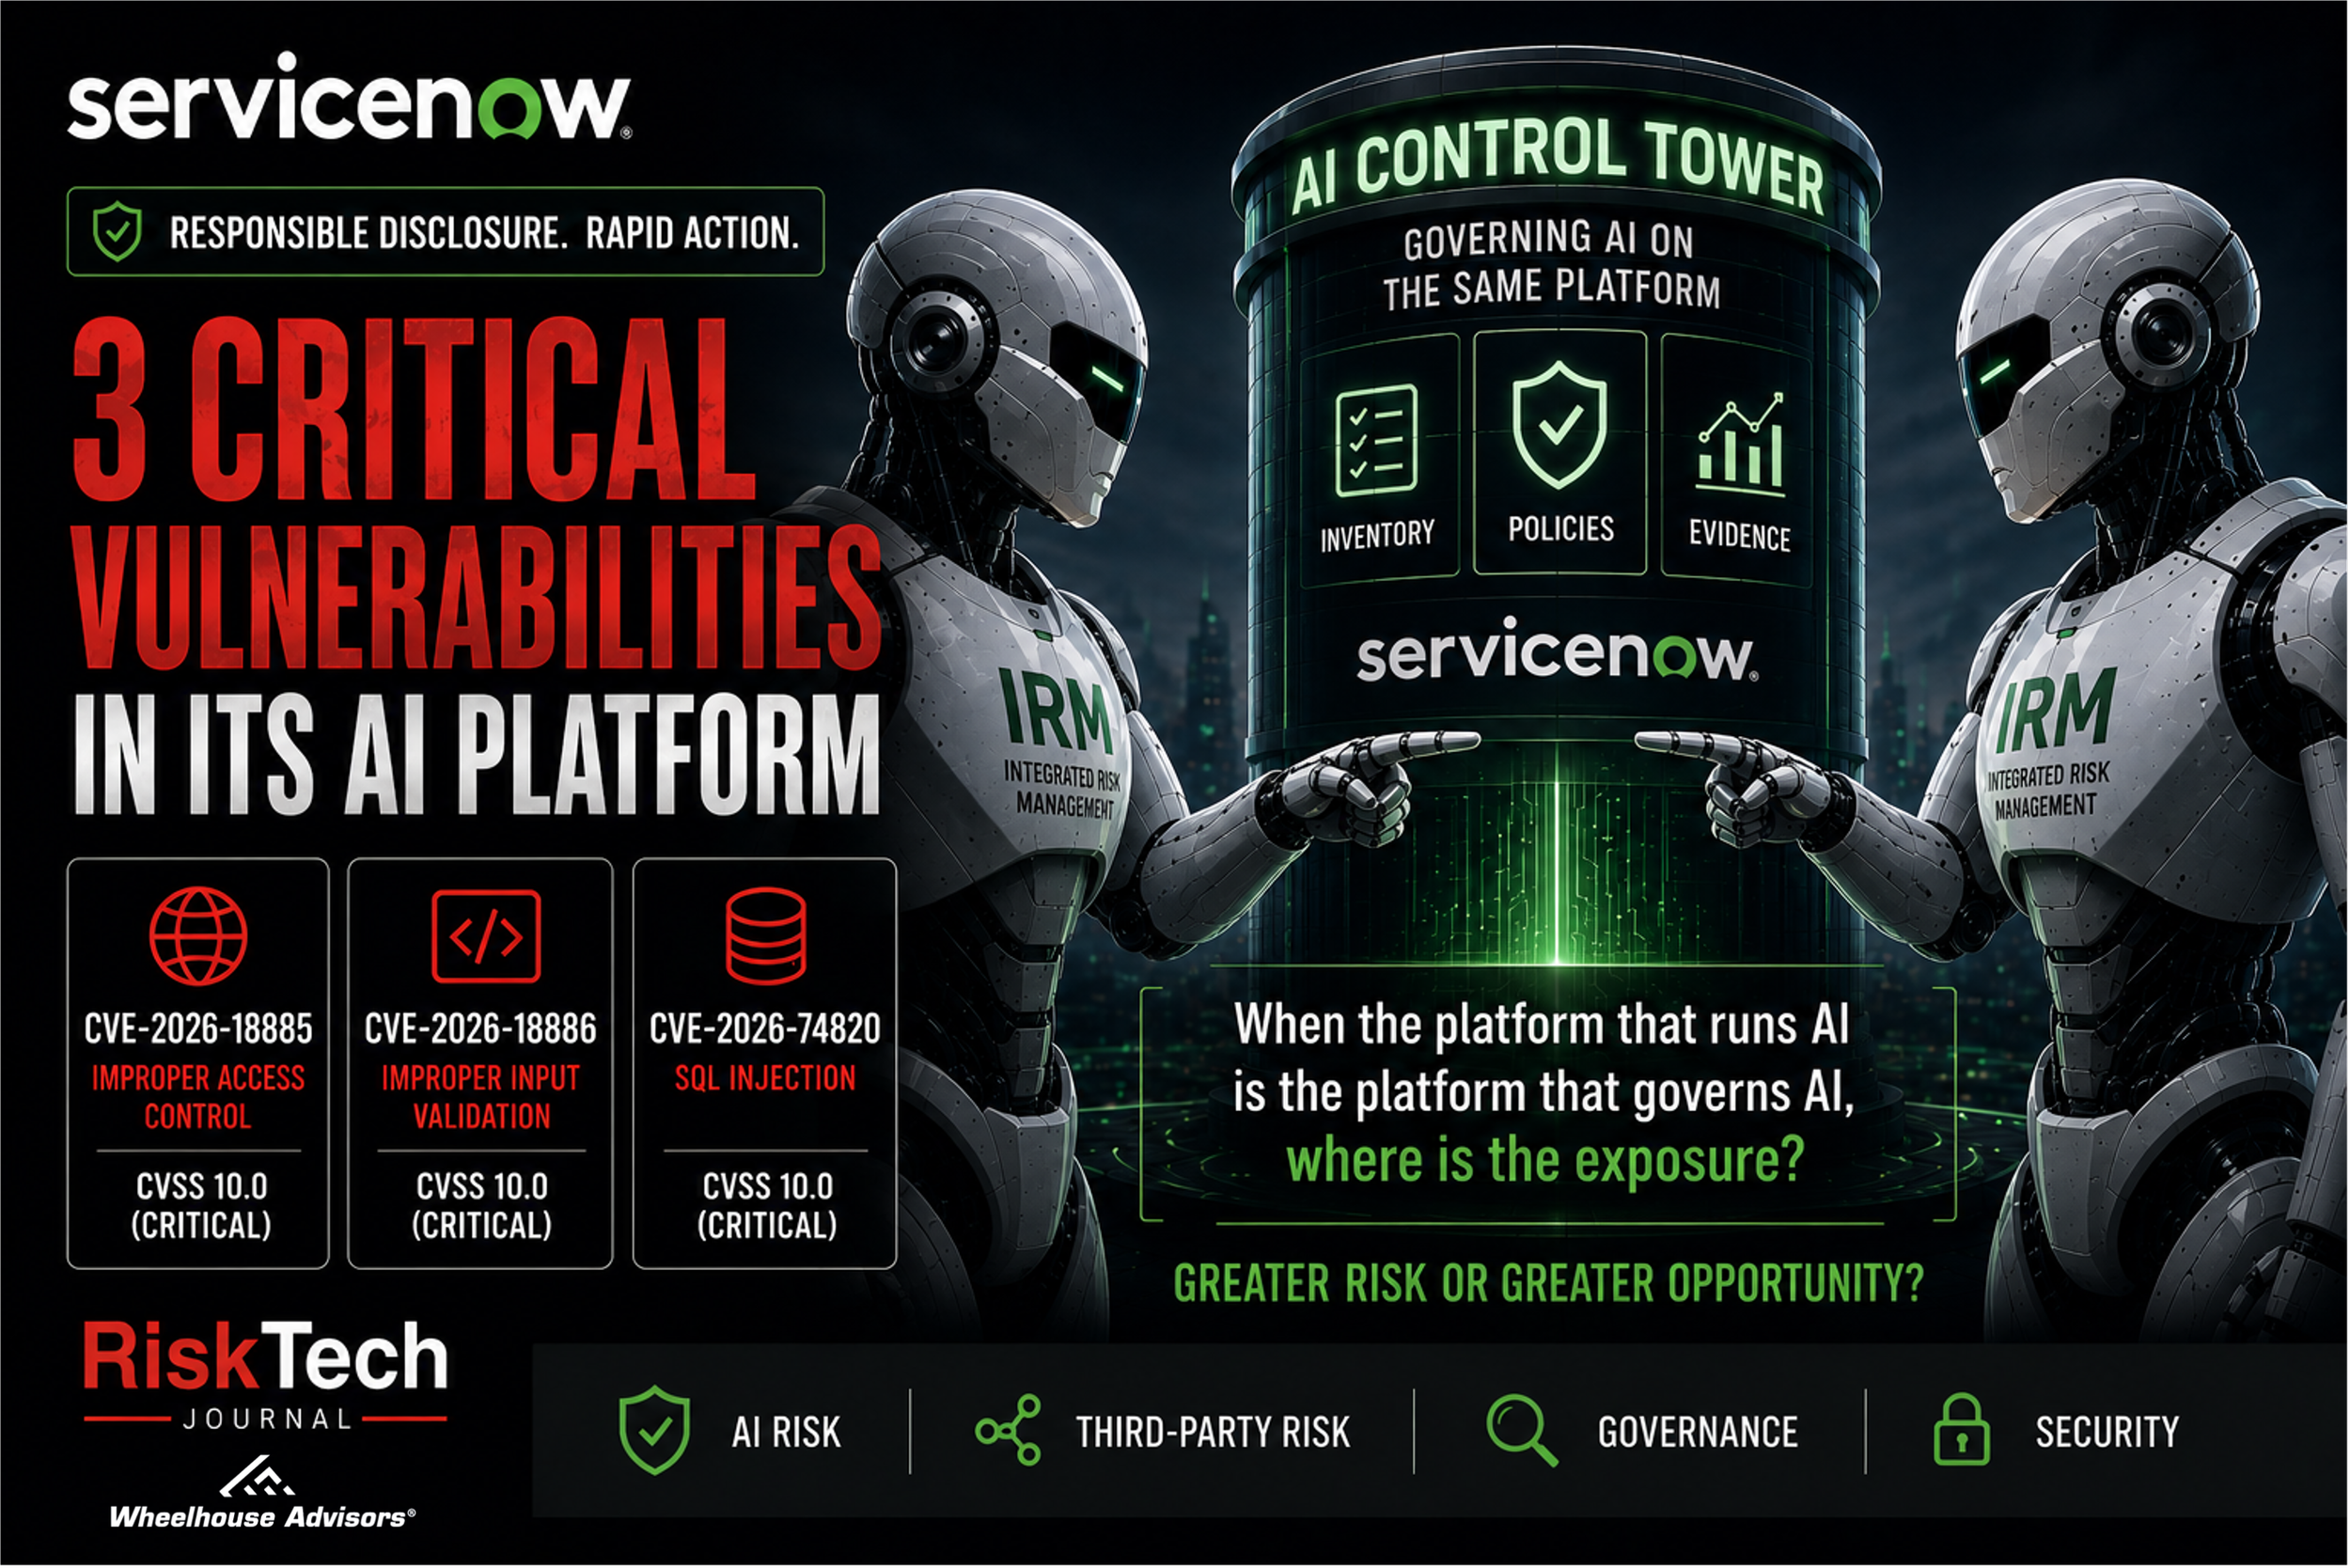
When ServiceNow Discloses Three Worst-Case Vulnerabilities, Whose Exposure Is It?
ServiceNow disclosed three vulnerabilities on August 27 that each carry the worst possible severity rating. The industry scores software flaws on a 0-to-10 scale called CVSS, and anything above 9 counts as critical. A 10.0 is the ceiling. It means an attacker can reach the flaw over the internet, needs no password and no help from a user, and can take full control of the affected system. ServiceNow assigned the maximum score to all three flaws itself, and it disclosed a fourth, rated 8.7, in the same advisory.
ServiceNow says it is not aware of the flaws being exploited, and no public attack code had surfaced as of Friday morning. Instances hosted by ServiceNow have already been patched. Customers and partners who run ServiceNow in their own environments have been told to confirm they are on a fixed release.
Most security teams will read that and reach for the patch checklist. That is the right first move. It is not the whole job.
DORA's Wide Net: More Than Just Cybersecurity for Financial Services
The recent release of draft technical standards for the European Union’s Digital Operational Resilience Act (DORA) paints a clearer picture of its sweeping reach. While many associate DORA with cybersecurity for financial institutions, it casts a wider net, encompassing third-party providers and demanding a stronger integrated risk management approach. Let's unpack the key takeaways for businesses navigating this evolving landscape, incorporating insights from various sources.

7 Ways to Master Third-Party Risk Management in Today's Complex Business Landscape
As the founder and CEO of Wheelhouse Advisors, my mission is to help organizations navigate the evolving digital landscape and adapt their third-party risk management strategies accordingly. This article will provide an updated and comprehensive guide to third-party risk management, highlighting its critical role in integrated risk management (IRM) and exploring key insights and best practices.