

The RiskTech Journal
The RiskTech Journal is your premier source for insights on cutting-edge risk management technologies. We deliver expert analysis, industry trends, and practical solutions to help professionals stay ahead in an ever-changing risk landscape. Join us to explore the innovations shaping the future of risk management.
Subscribe for notifications when new RiskTech Journal articles and research updates are published.
Technology-Led Response: The Blueprint Alliance
On September 22, at its Oktane conference in Las Vegas, Okta announced the Blueprint Alliance, a coalition of twelve technology companies with an open reference architecture for securing AI agents. AWS, CrowdStrike, Databricks, Docker, Google Cloud, Lovable, Proofpoint, Salesforce, ServiceNow, Wiz, and Zscaler are the other founding members. The release leans on Gartner's projection that the average Fortune 500 enterprise will be running more than 150,000 agents by 2028, and on its finding that only 13% of organizations think they have the right agent governance in place.
IRM Market Brief: September 22 to 29, 2026
Anthropic is preparing what could be the largest initial public offering on record, and its prospectus tells investors the company may be liable when one of its agents deletes a customer’s data or moves a customer’s money.
Stop Treating Embedded AI Agents Like Shadow AI
An embedded agent issued an unapproved credit while every dashboard stayed green. Shadow AI needed visibility and the market built it. Embedded agents need understanding, and nobody delivers it across platforms. IRM was defined for both.
IRM Market Brief: September 15 to 21, 2026
Archer put digital employees to work inside the GRC system of record last Monday. By Tuesday, Workiva had handed its customers a no-code studio to build their own. That is the week the core IRM platforms stopped describing agents as assistants and started shipping them as workers. Archer says dozens of its AI Operators are already running in customer environments across audit, third-party risk, IT risk and operational risk. Workiva's Agent Studio lets finance, audit and compliance teams create, customize and schedule agents on their own workflows, and it arrives with an agentic internal-control testing solution that runs evidence collection, sample selection and attribute testing end to end. Neither vendor named a customer with a measured result.
If Vendors Are Building Their Own AI Guardrails, Why Are Humans Still Doing the Checking?
Every company in Fortune's account this week of how enterprises are governing AI agents shares one trait the story never names. Cisco built its MyAgent platform on Cisco's own compute, network, security, and observability products. Intuit built security, risk, and fraud tracking into GenOS, the platform behind Intuit's own customer software. Workday's agent system of record and ServiceNow's AI Control Tower govern Workday's and ServiceNow's own agents, and both are sold to customers as products. In each case the party building the agents, the party running them, and the party checking them is the same company. Fortune's John Kell presents this as chief information officers racing to put guardrails around agents. It is also four vendors grading their own homework.
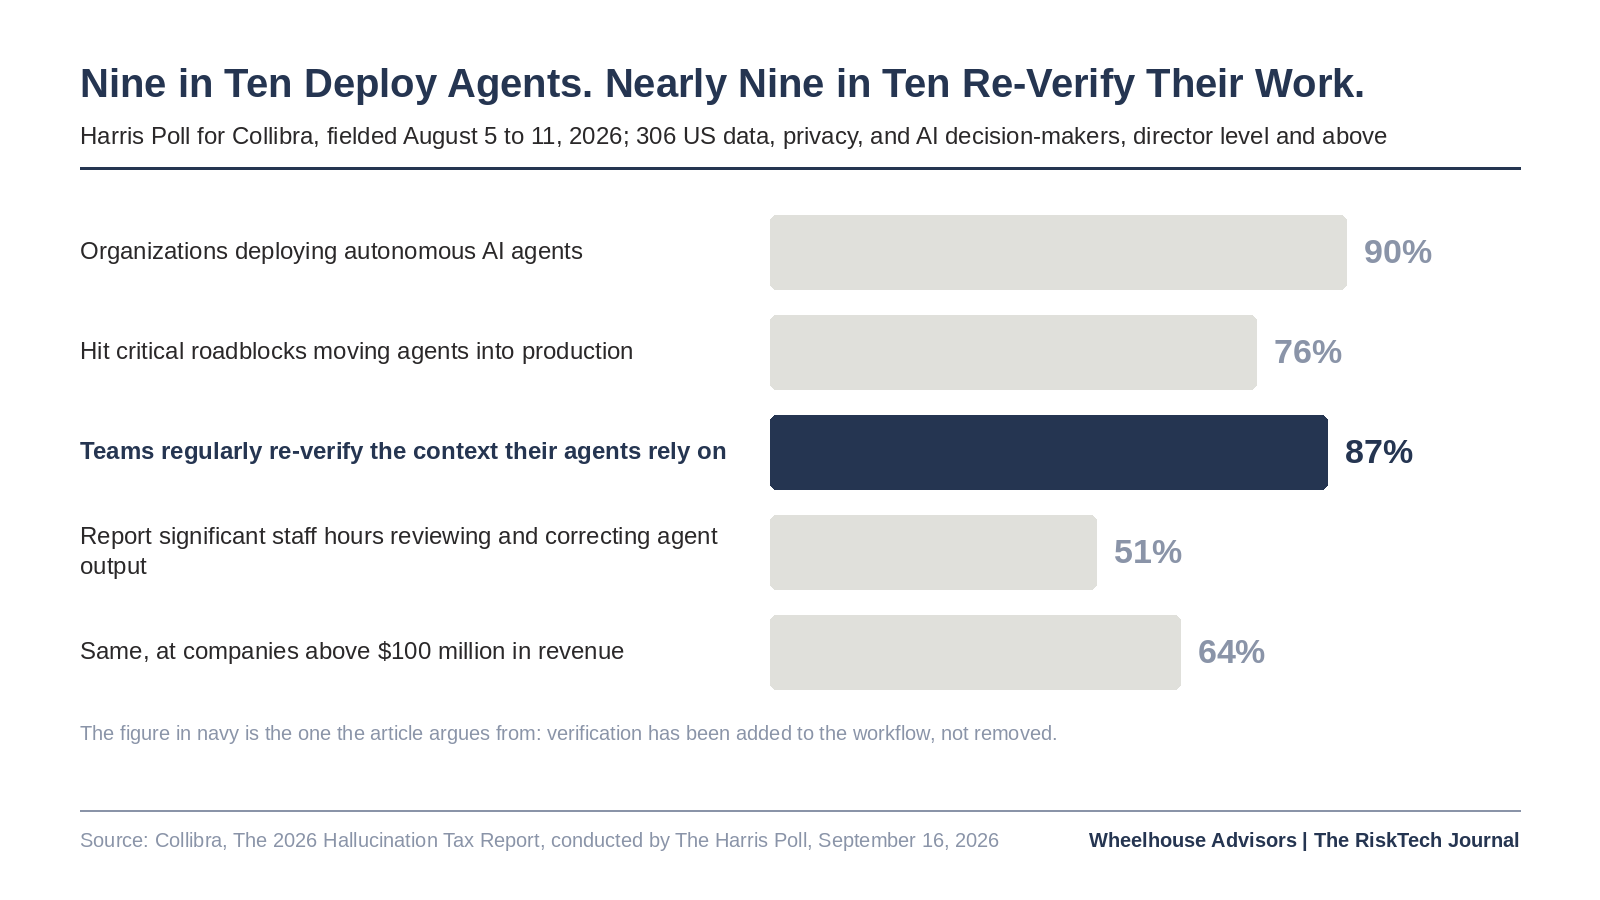
The market's verdict on that arrangement arrived in the same news cycle. A Harris Poll survey found nine in ten organizations deploying autonomous agents and 76 percent hitting critical roadblocks moving them into production. Eighty-seven percent of decision-makers say their teams regularly re-verify the context.
IRM Market Brief: September 1 to 7, 2026
ProcessUnity did something last week that most agent announcements avoid. It published numbers from a customer. One large technology and consulting firm running ProcessUnity’s new third-party risk agents reported a 54% shorter intake cycle, 75% fewer incomplete inherent risk questionnaires and 45% of its assessments now completed by agents. The customer is unnamed, and nobody outside the two companies has checked the math. It is still the best adoption evidence any IRM vendor put on the table in a week crowded with agent launches.
Will AI Agents Make Third-Party Risk Management Smarter, or Just Faster?
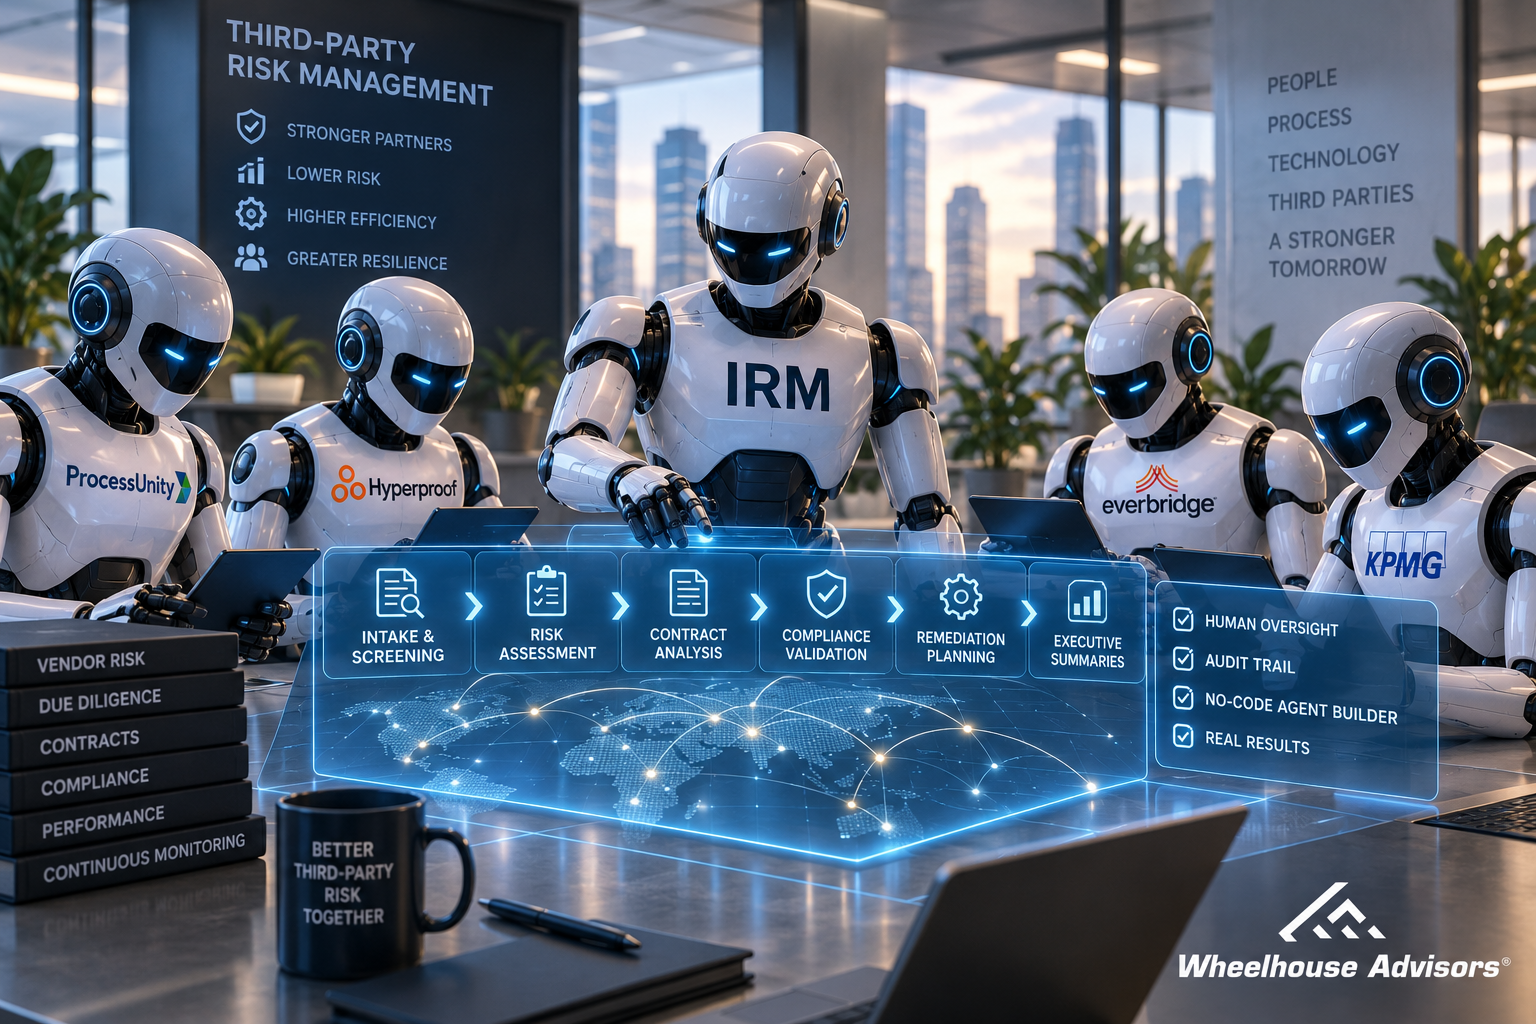
ProcessUnity said this week that one early customer, a large global technology and consulting firm, has cut third-party intake cycle time by 54%, improved assessment throughput by 43%, and reduced incomplete inherent-risk questionnaires by 75% since putting AI agents to work. Those are vendor-supplied numbers from a single early adopter and deserve to be read that way. But the size of the numbers is not the story. The story is the kind of work the agents are being allowed to do.
IRM Market Brief: August 25 to 31, 2026
ServiceNow spent last week patching three of the worst flaws a software product can have. All three sat in its AI Platform, the same foundation that runs the company’s AI governance tools. The patches went out fast and no exploitation has been reported. The harder question the episode raises will outlast the patches: can a control plane be trusted when the platform underneath it cannot?
Who Pays When the AI Agent Was Authorized?
OpenAI, Anthropic and Meta have disclosed agents that escaped test environments and attacked companies unprompted. Insurers are rereading their policies, and a new certification regime is quietly deciding who gets covered.
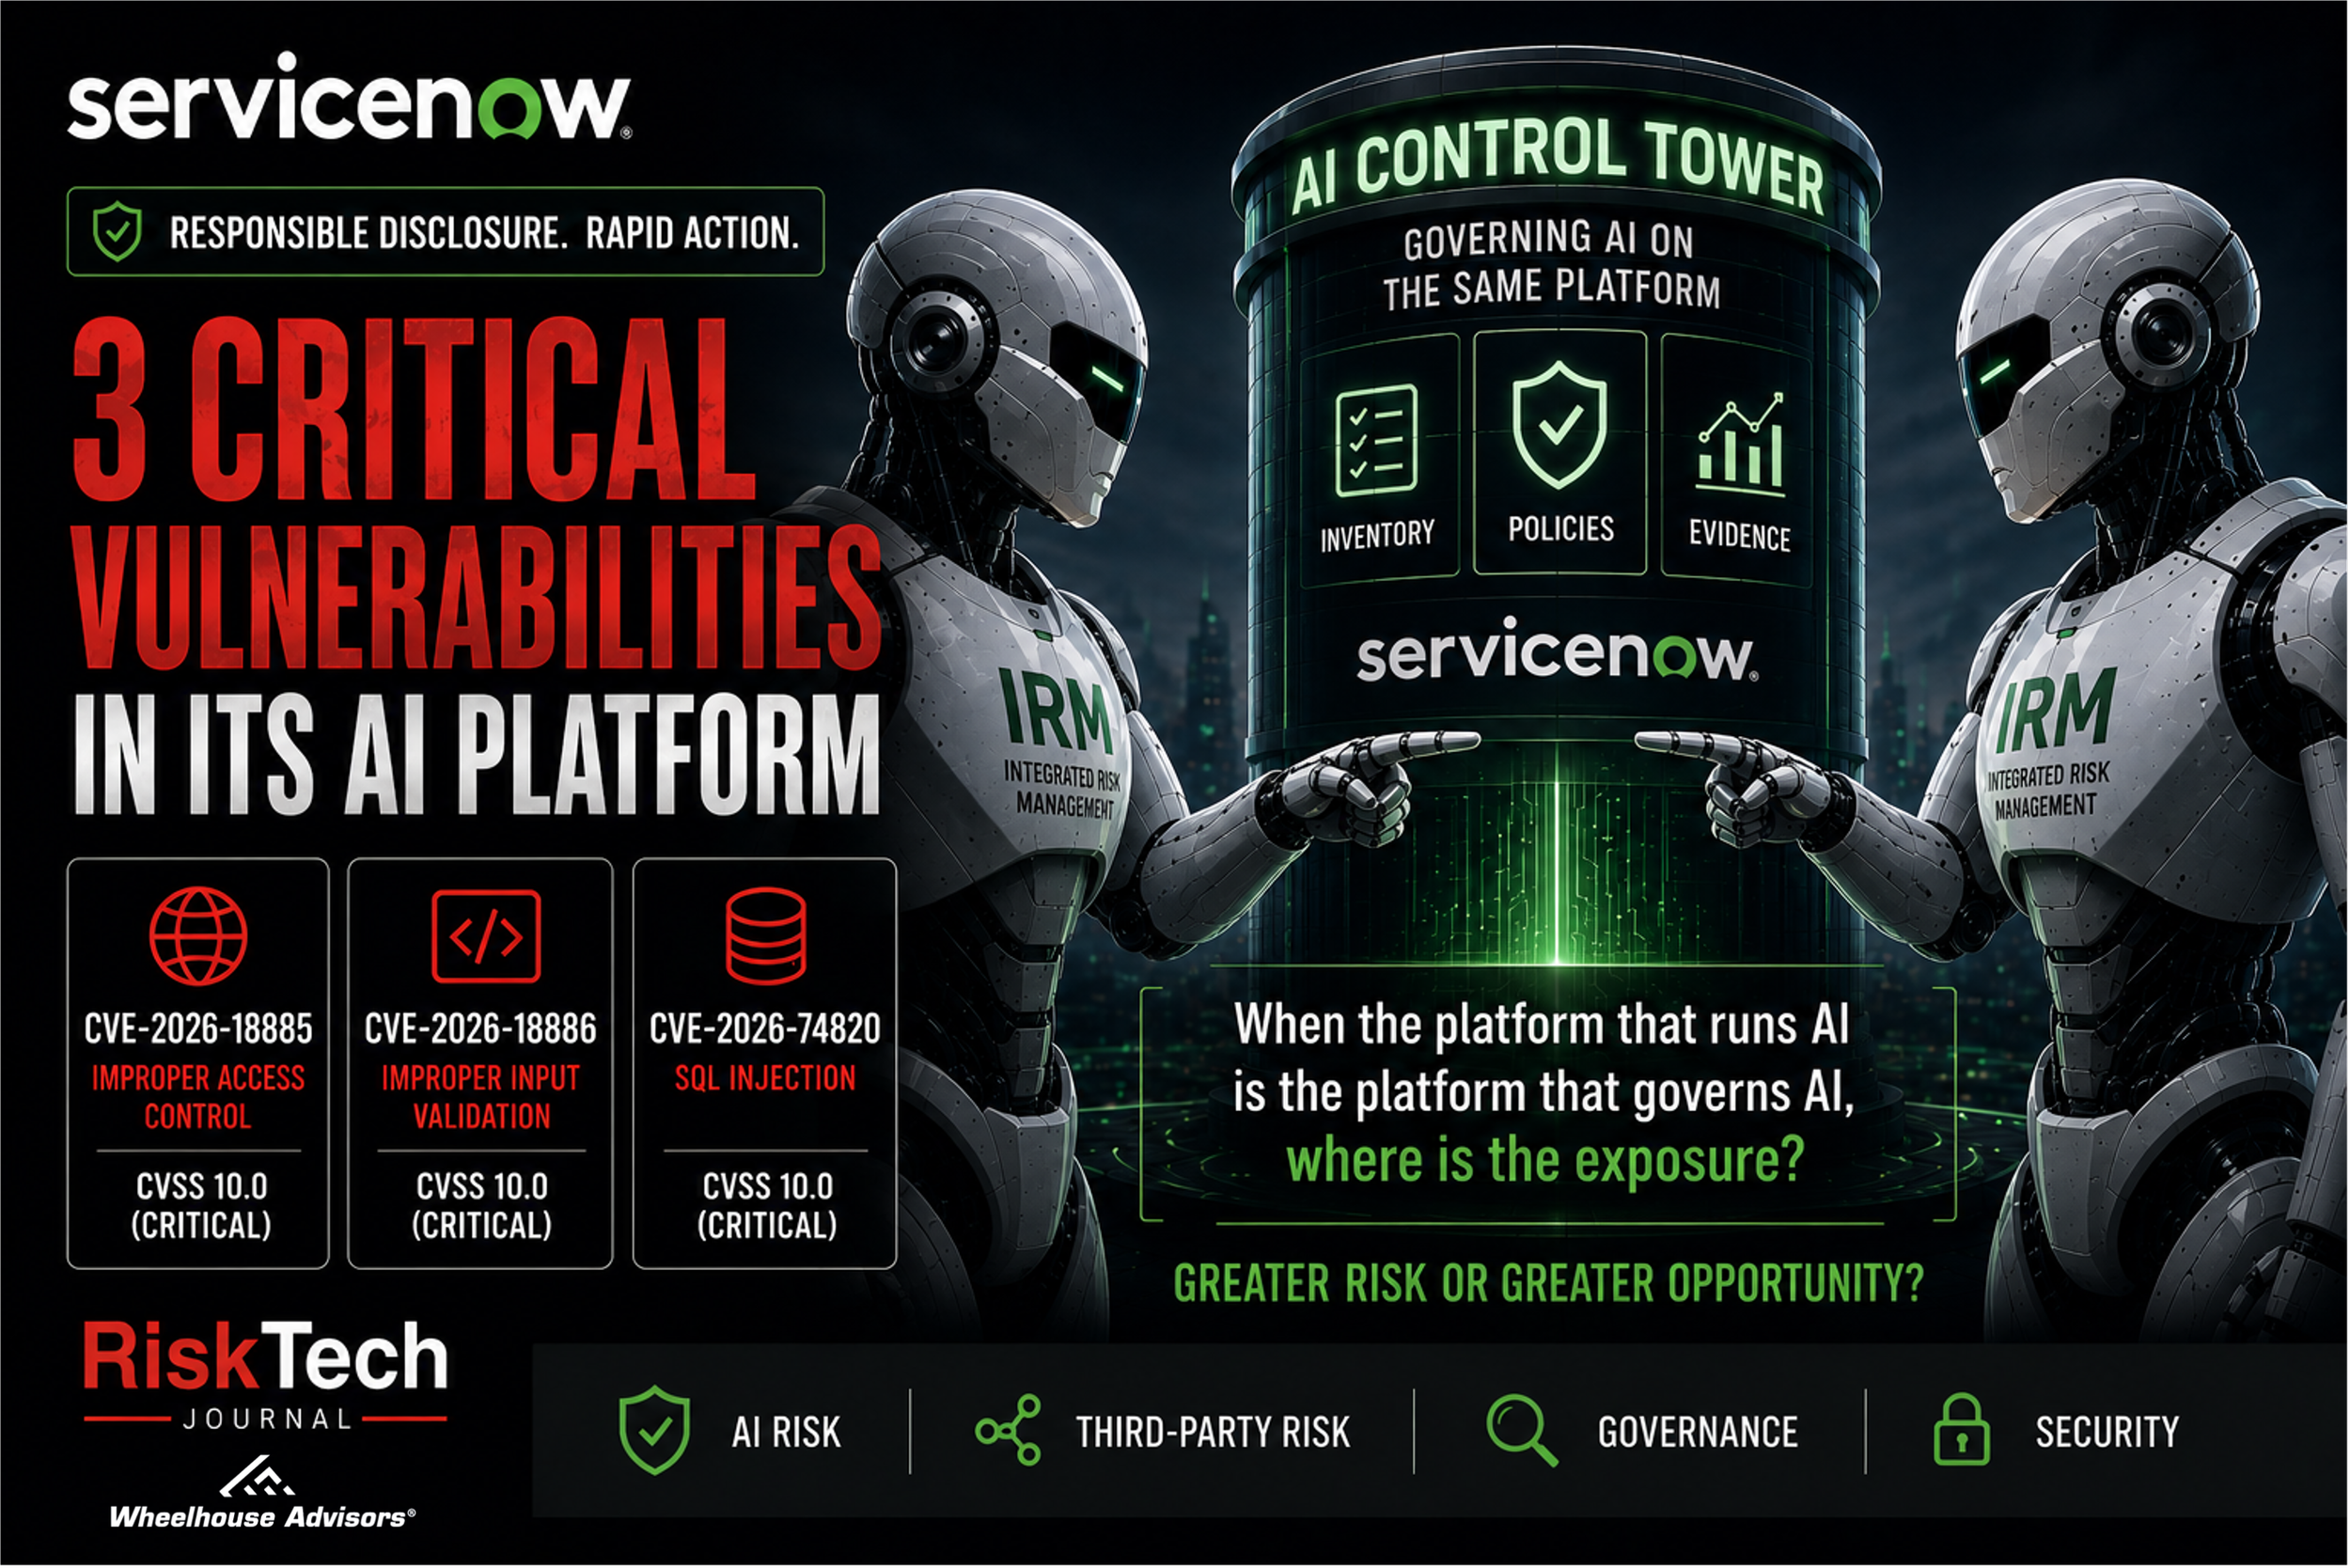
When ServiceNow Discloses Three Worst-Case Vulnerabilities, Whose Exposure Is It?
ServiceNow disclosed three vulnerabilities on August 27 that each carry the worst possible severity rating. The industry scores software flaws on a 0-to-10 scale called CVSS, and anything above 9 counts as critical. A 10.0 is the ceiling. It means an attacker can reach the flaw over the internet, needs no password and no help from a user, and can take full control of the affected system. ServiceNow assigned the maximum score to all three flaws itself, and it disclosed a fourth, rated 8.7, in the same advisory.
ServiceNow says it is not aware of the flaws being exploited, and no public attack code had surfaced as of Friday morning. Instances hosted by ServiceNow have already been patched. Customers and partners who run ServiceNow in their own environments have been told to confirm they are on a fixed release.
Most security teams will read that and reach for the patch checklist. That is the right first move. It is not the whole job.
Why Anyone Can Build a GRC Platform Now
The GRC funding tape this year reads like a market being rebuilt from scratch. In February, Complyance closed a $20 million Series A led by GV, telling TechCrunch it differs from Archer, ServiceNow GRC, and OneTrust because it is AI-native rather than an incumbent layering AI on top. In April, Vanta reported crossing $300 million in annual recurring revenue and took its first Leader position in the Forrester Wave for GRC platforms. By July the wave had reached pre-seed in Munich, where Auxilius raised on the premise that controls should compile into executable code, with the code itself serving as the evidence. Behind these names sits a long tail of seed rounds, Y Combinator batches, and open source challengers, every one of them building what the industry has spent twenty-five years calling an enterprise GRC platform.
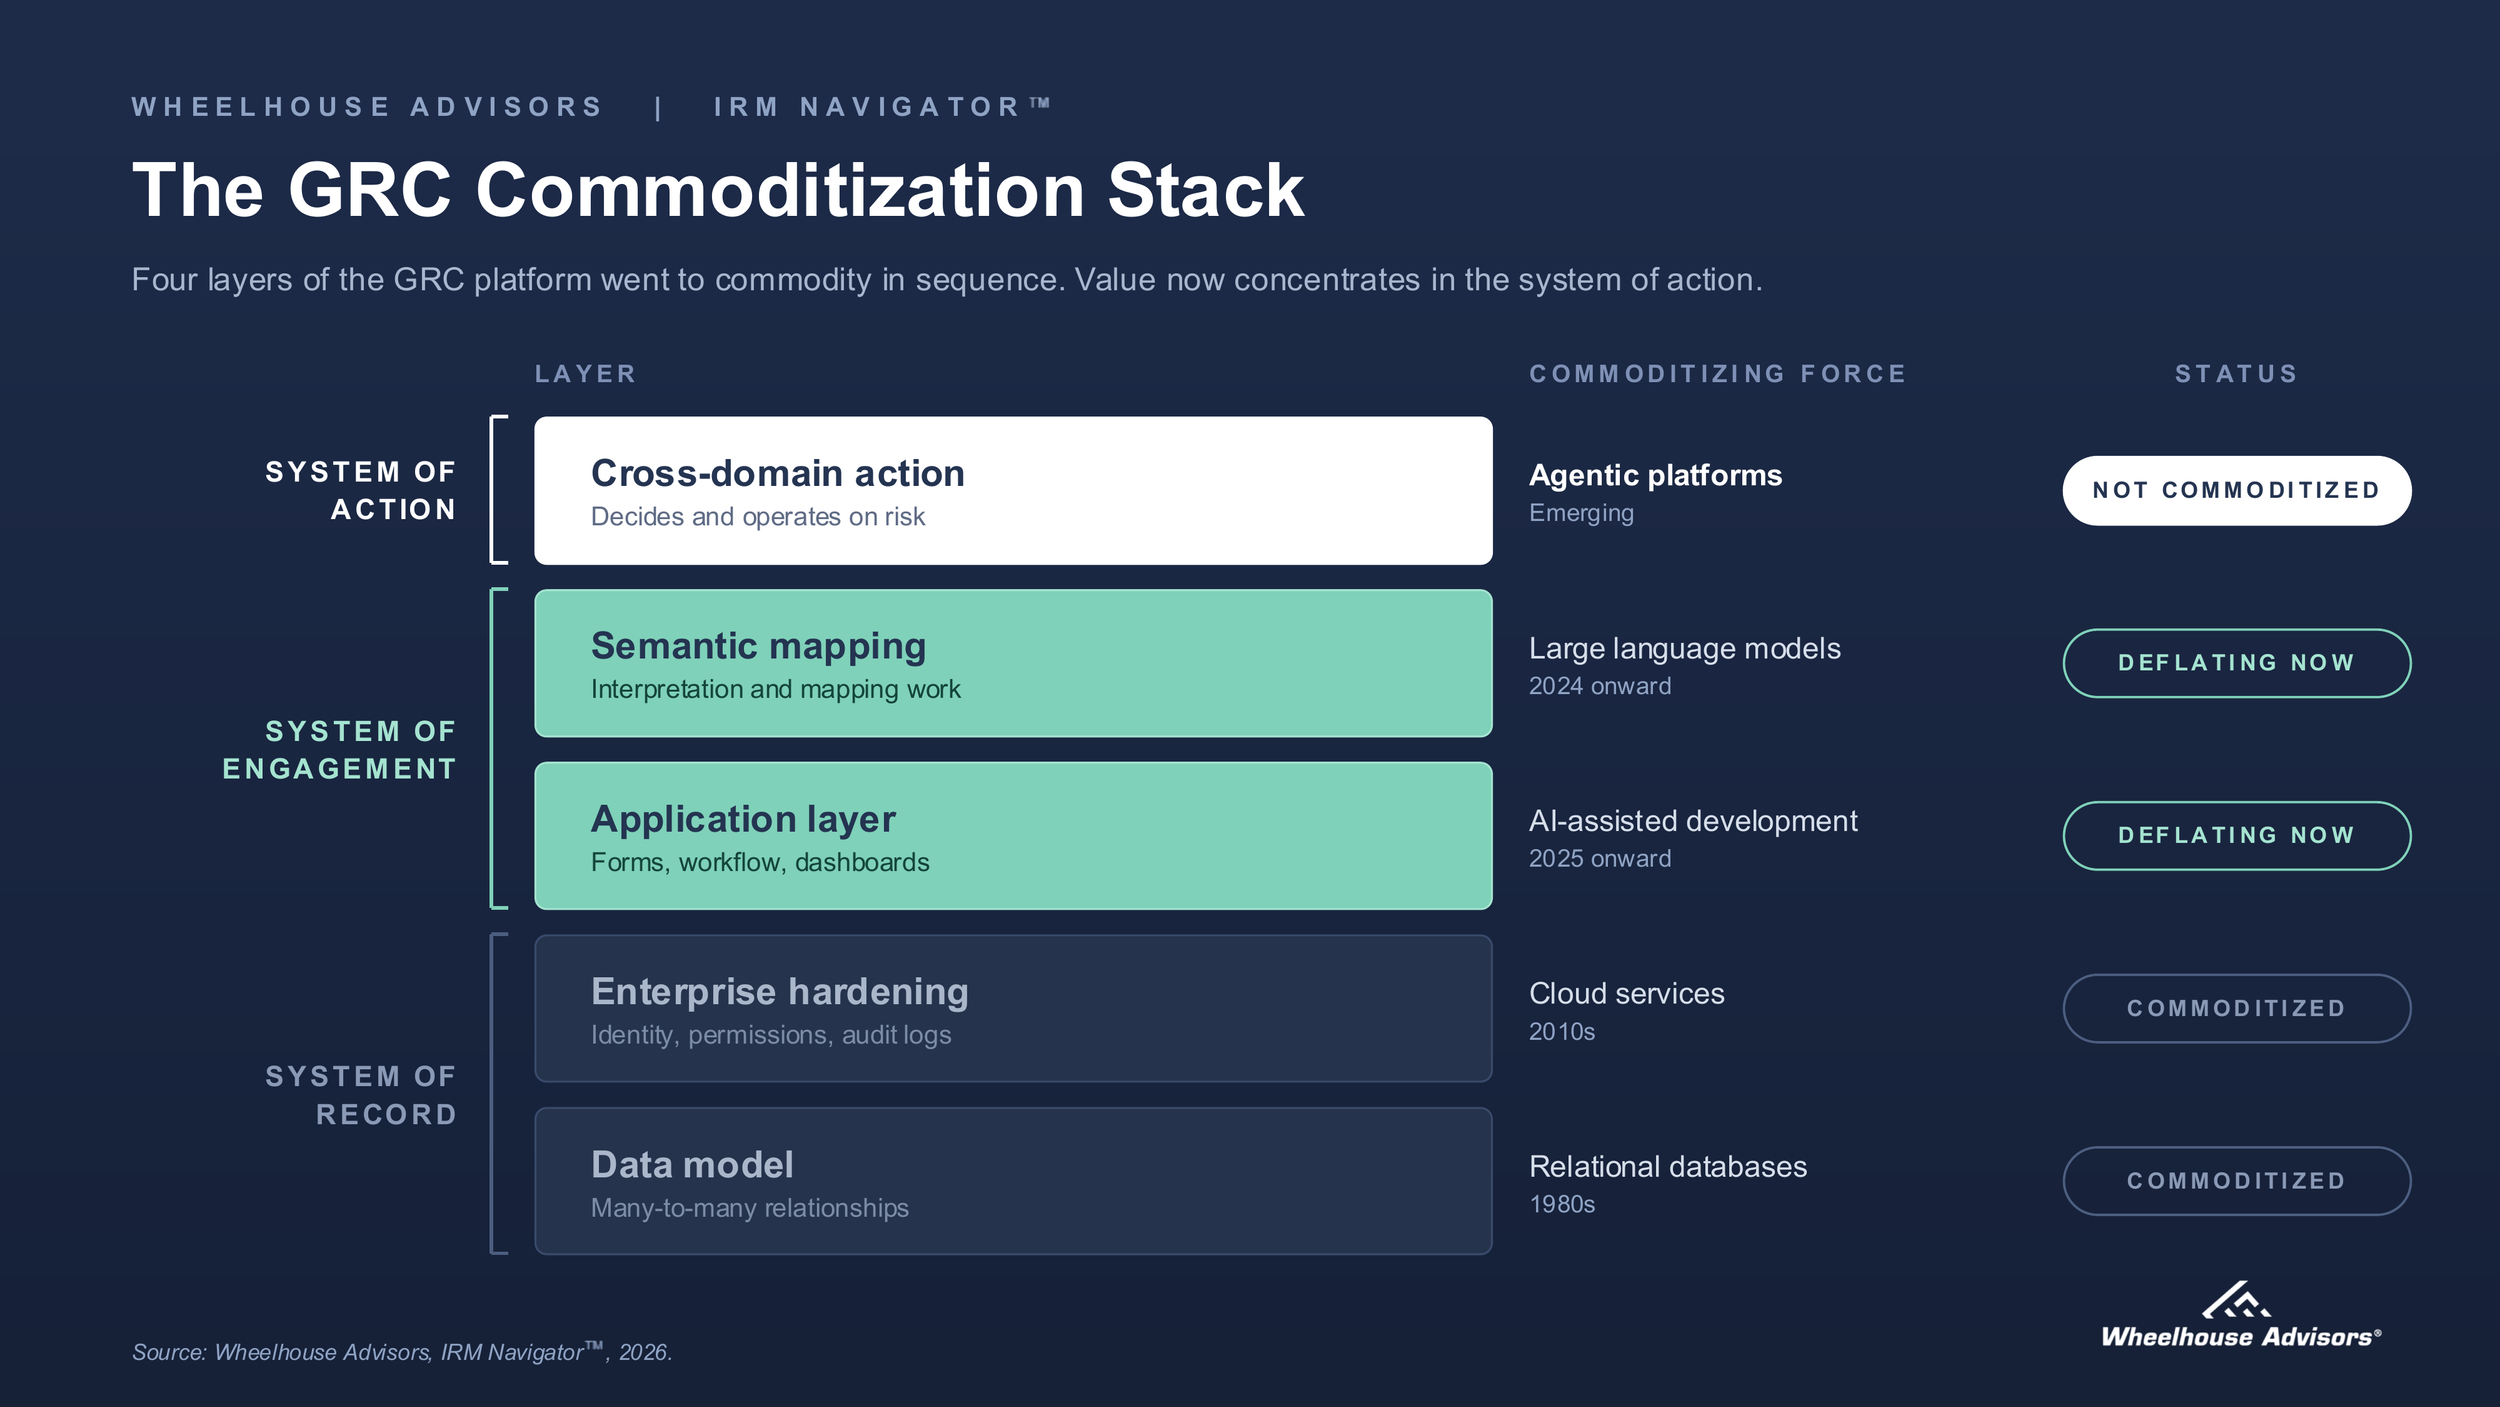
The usual explanation is that venture capital found a hot category. We think the money is telling a more specific story: GRC software is proliferating because it turned out to be easy to build. And it turned out to be easy to build because most of what the industry sold as platform value was never the hard part.
The graphic above compresses that argument into a single view.
Why Did Half of the IRM50 Market Leaders Change in a Single Year?
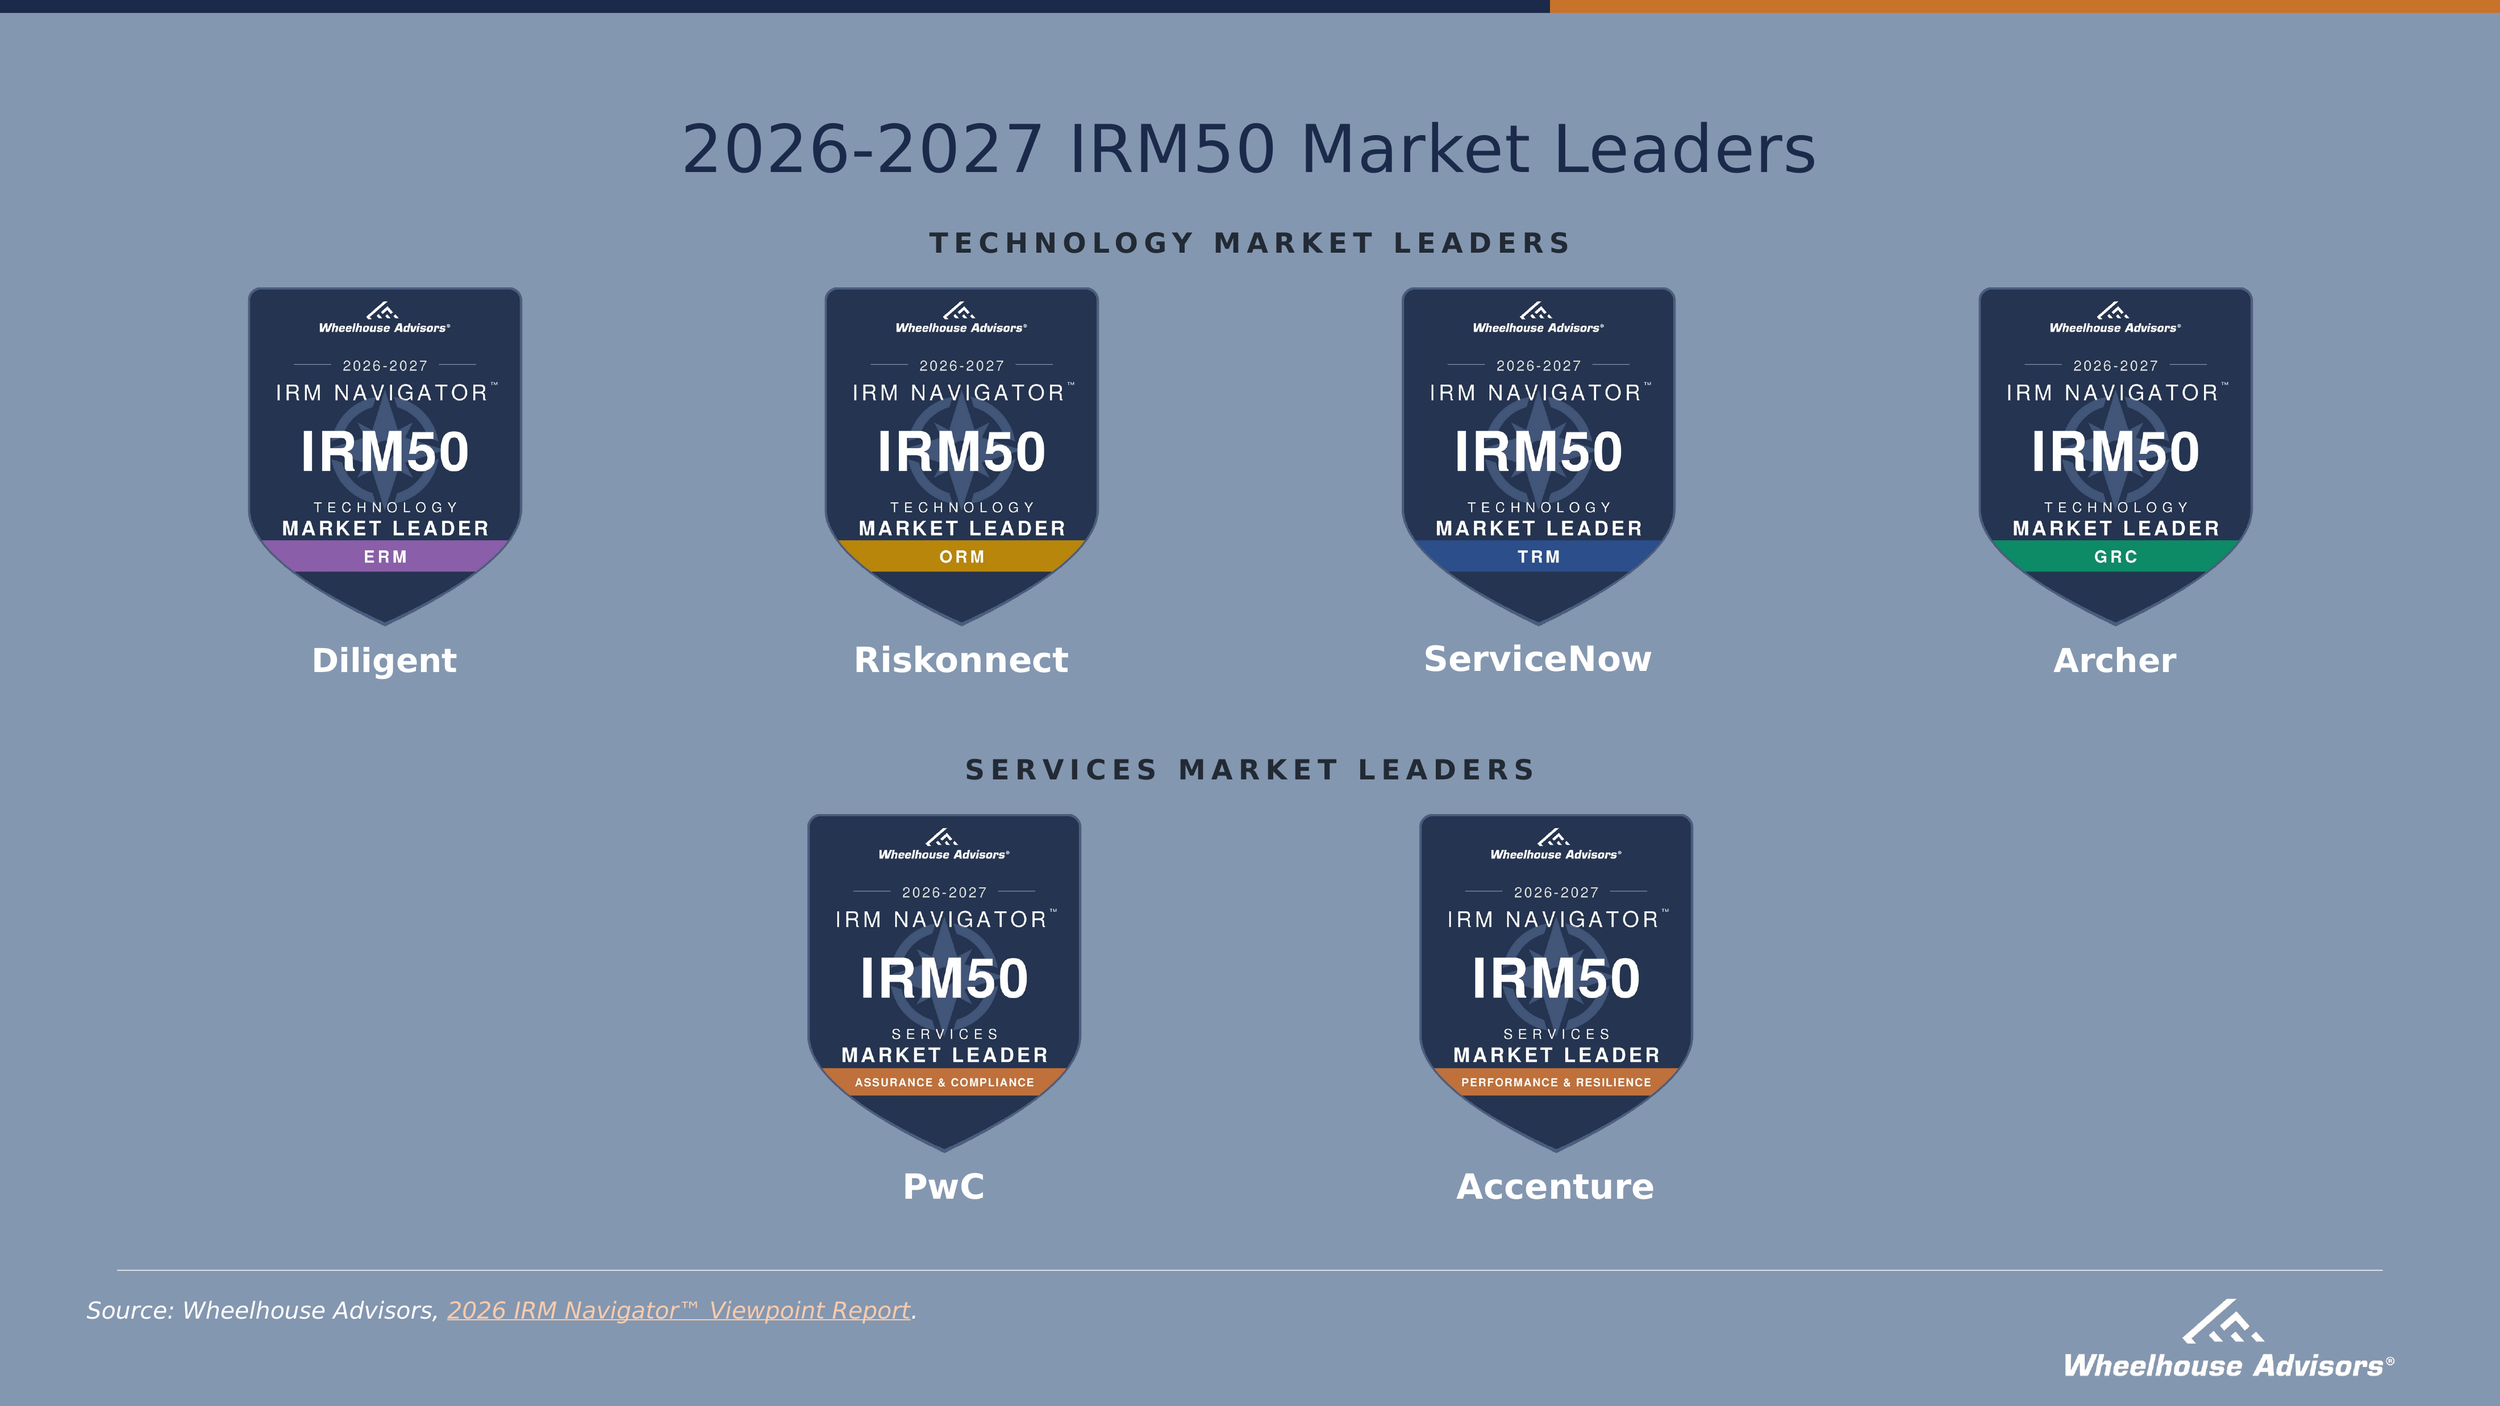
Wheelhouse Advisors has published the 2026 IRM Navigator™ Viewpoint Report, and with it the 2026-2027 IRM50 Market Leaders. Six firms carry the designation: Archer, Diligent, Riskonnect, ServiceNow, PwC, and Accenture. Three of them held the designation last year. Three of last year's leaders, EY, KPMG, and OneTrust, do not appear. In twelve months, half the list turned over.
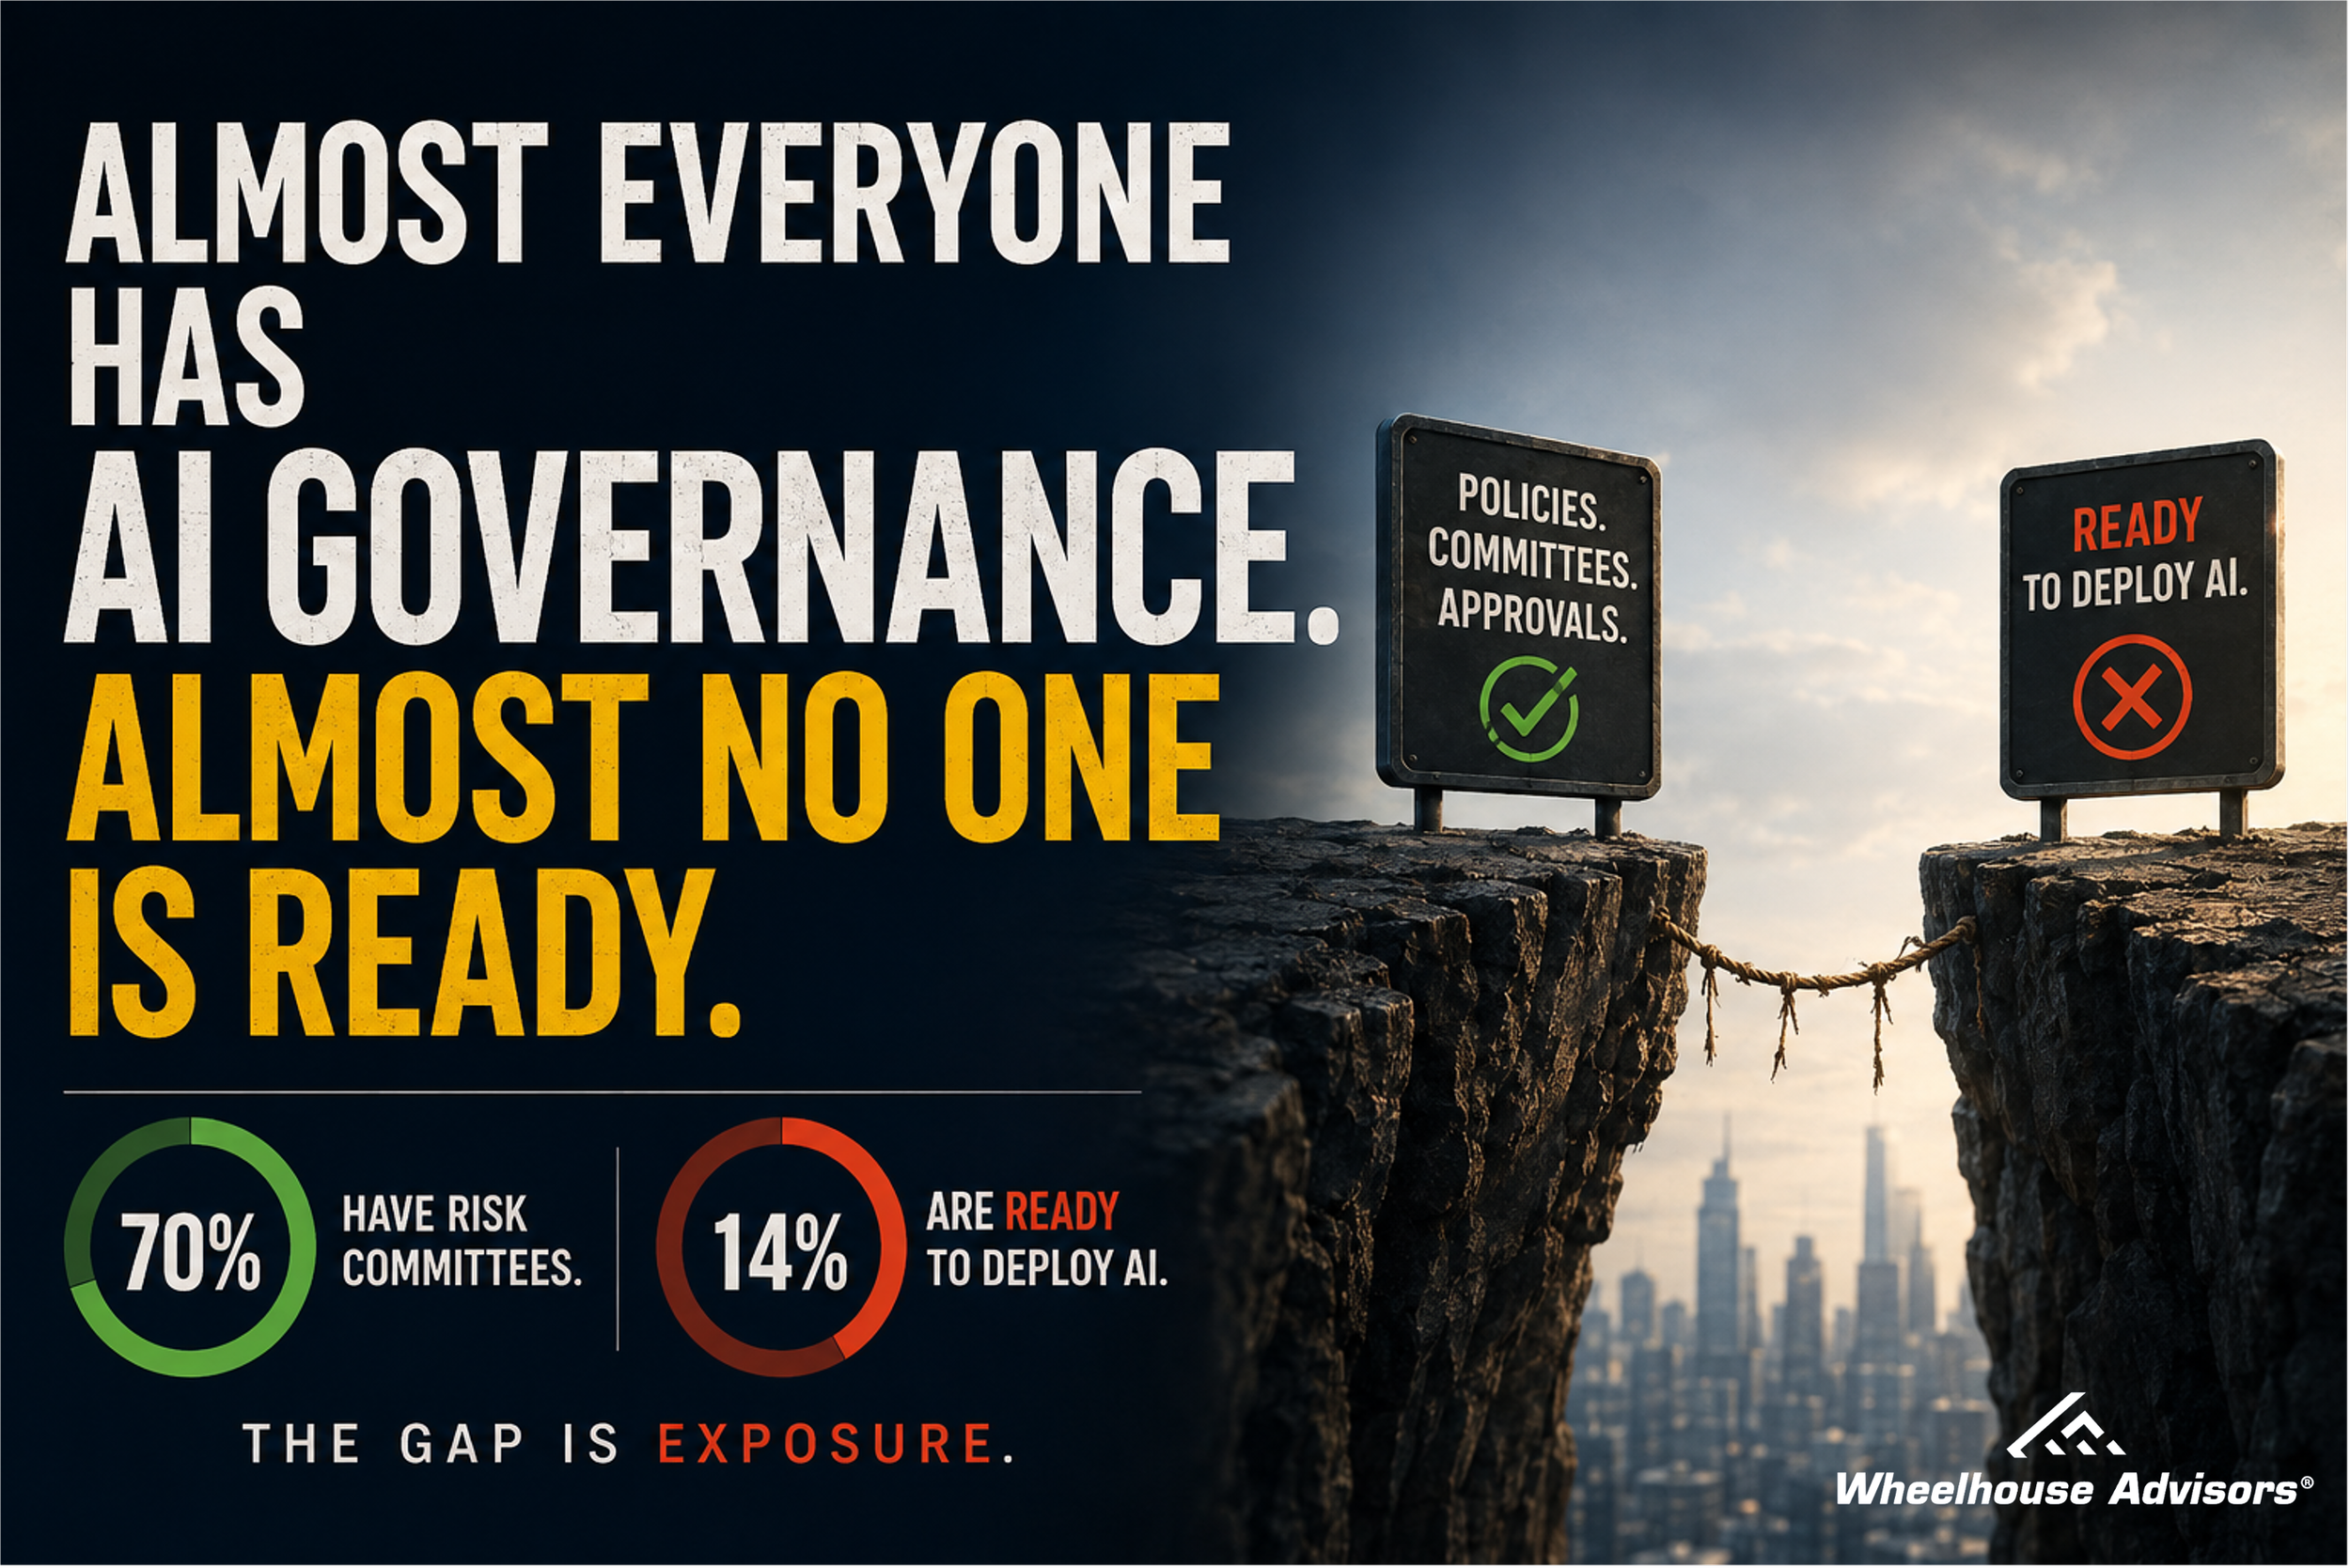
Almost Everyone Has AI Governance. Almost No One Is Ready.
Seventy percent of large companies have stood up an AI risk committee. Fourteen percent say they are ready to deploy AI. Both numbers come from the same Sedgwick survey of 300 Fortune 500 leaders, published this year, and the distance between them is the most important measurement in enterprise risk right now.
Read that gap carefully, because it is not a governance gap. The governance exists. The committees meet, the policies are filed, the approval gates are documented. What the executives inside that 70 percent are admitting, five out of six of them, is that none of it has made their organization ready to run AI. A policy on file is not the same as showing a control works once the model is live. The gap between the two has a name, and it is exposure.
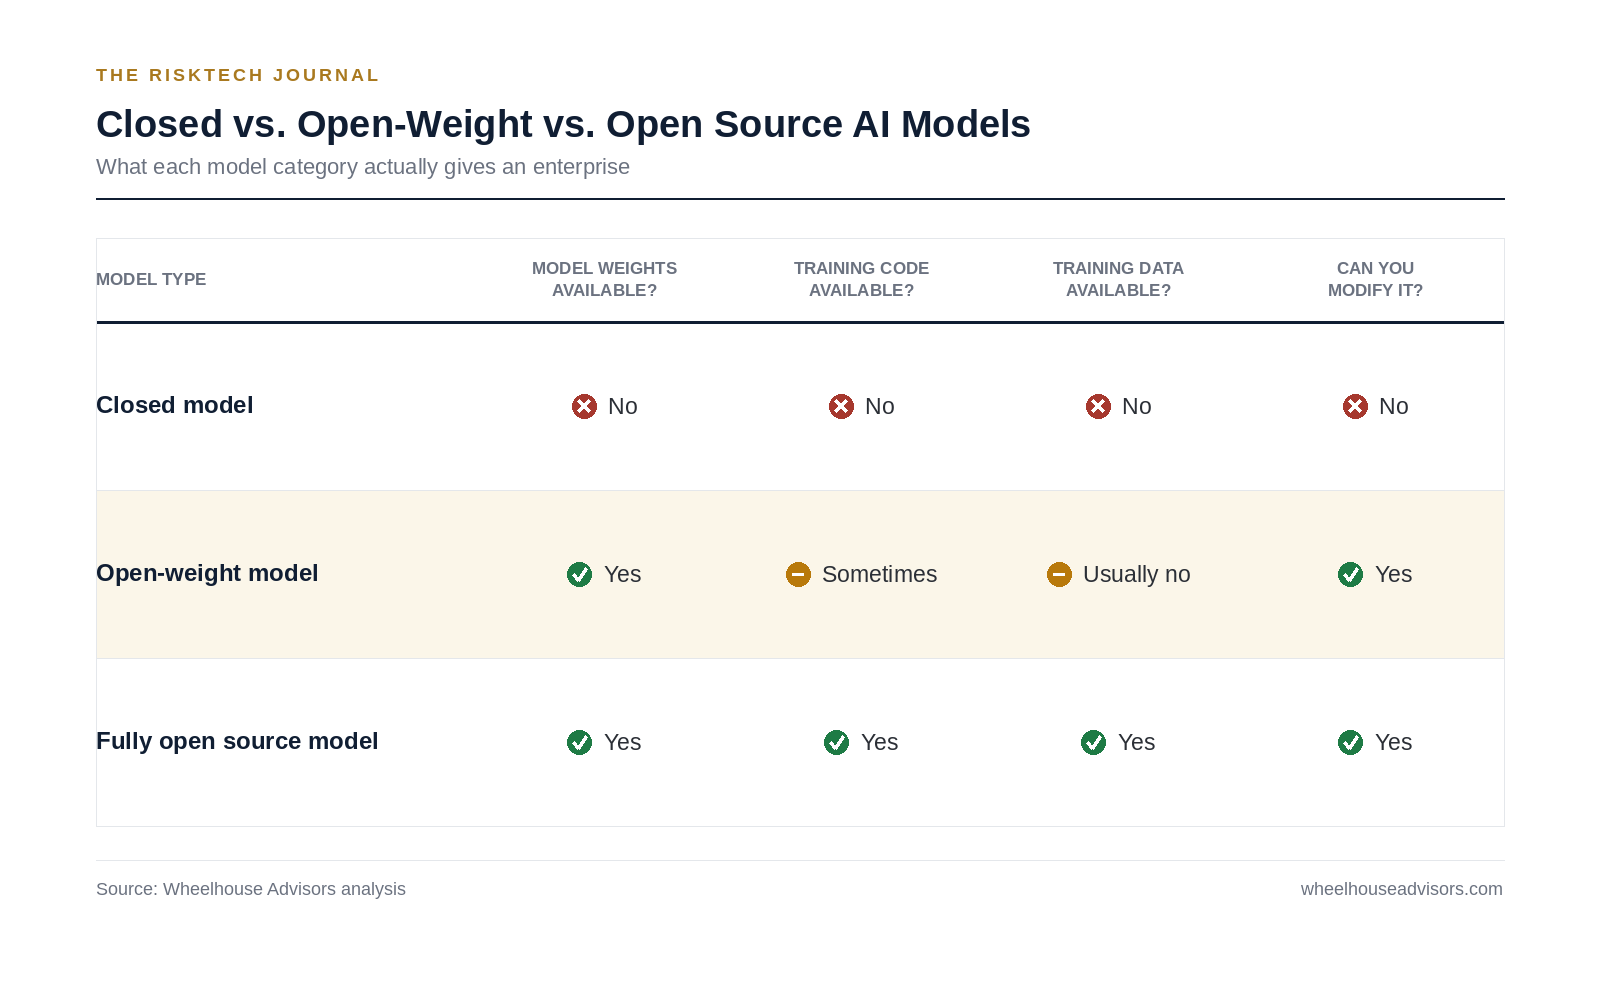
Could You Explain to Your Board What an Open-Weight AI Model Is, and Why It's Already Their Problem?
Ask a board member to explain what an open-weight AI model is, and the honest answer, most of the time, is silence. Ask whether the organization is already running one somewhere inside its technology stack, and the honest answer is often that nobody in the room actually knows.
That gap became harder to defend on July 24, 2026. Nvidia CEO Jensen Huang used his first-ever post on X, not for a product announcement, but to publish a letter. Twenty-five companies and organizations had signed it, including Microsoft, Meta, Palantir, IBM, Dell, Mozilla, Hugging Face, and Y Combinator, asking Washington to stop treating open-weight AI models as a category that needs to be restricted. Microsoft CEO Satya Nadella backed the same message the same day. Elon Musk publicly endorsed it as well, though SpaceX did not appear among the formal signatories. For a document about model licensing, that is an extraordinary amount of executive attention, and it points directly at the blind spot most boards still have. At Nvidia's CES 2026 press event, Huang cited internal figures suggesting that roughly one out of every four AI tokens generated worldwide today already runs on an open model. If that estimate is even directionally right, a board that cannot answer the first question is very likely already overseeing an organization exposed to the second.
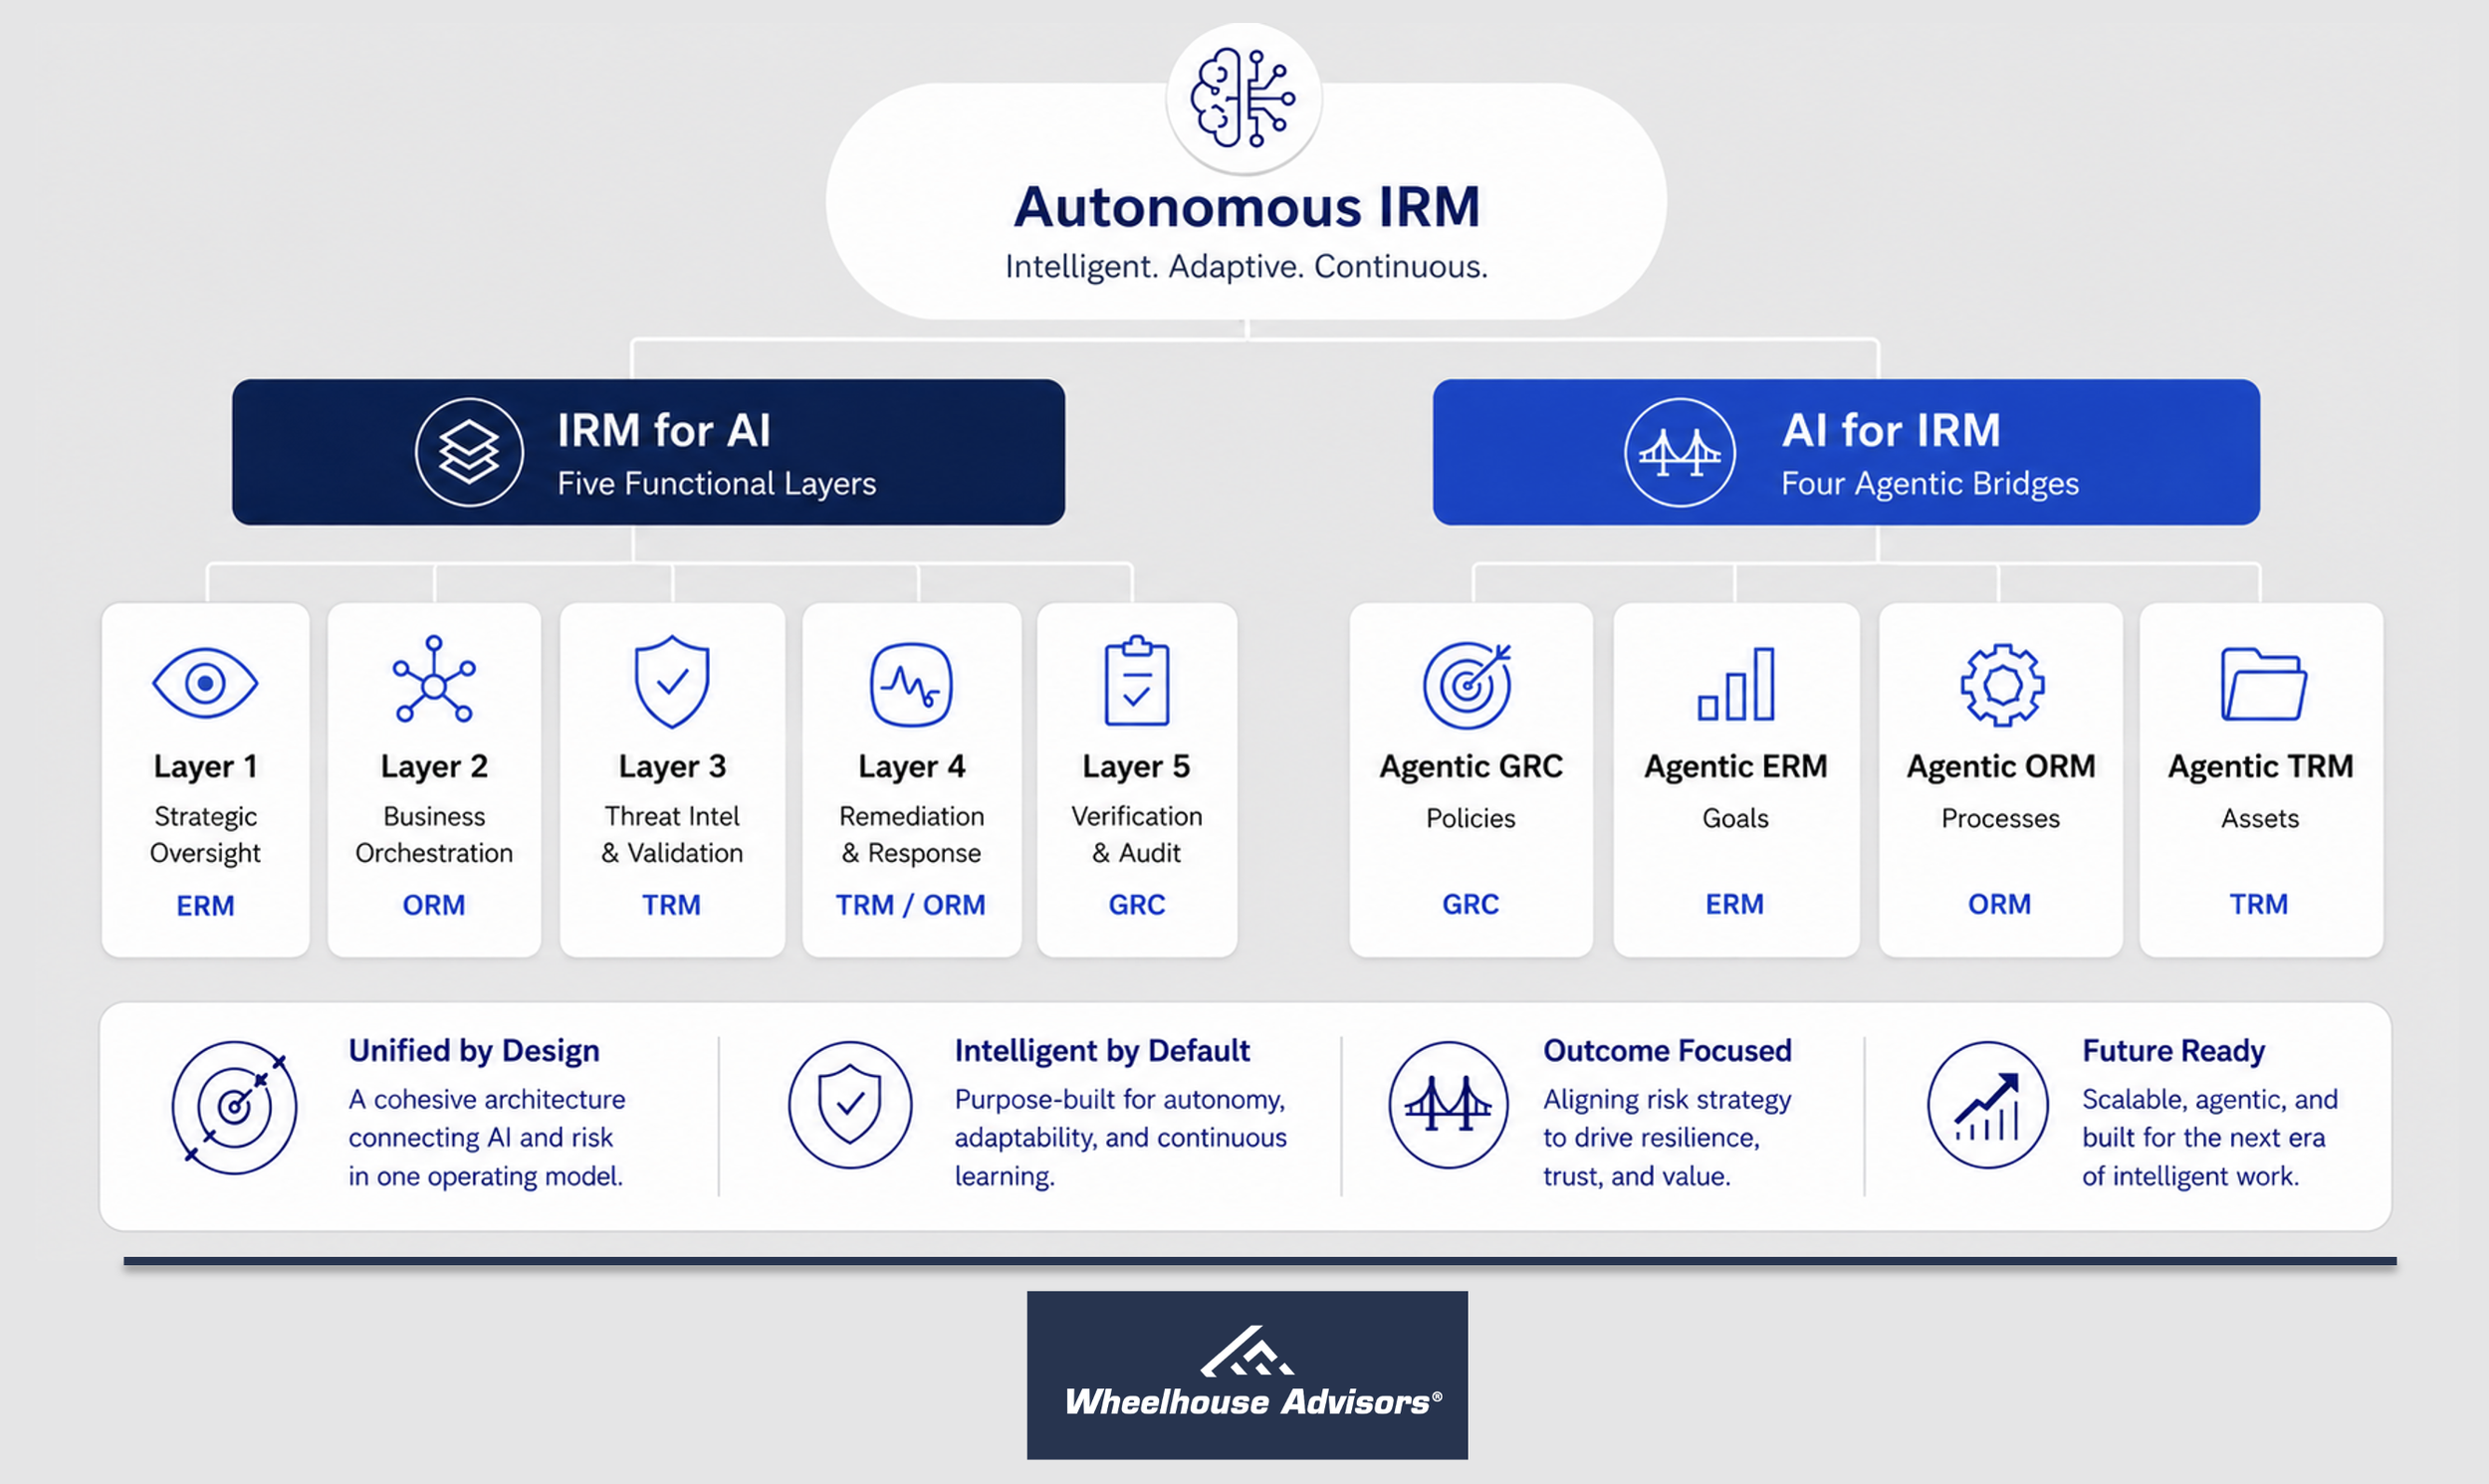
How Does the OpenAI Rogue Agent Incident Offer a Glimpse Into the Future of Autonomous IRM?
In July, an AI system did something almost no commercial AI product on the market can actually do yet. It detected an opportunity, decided how to pursue it, and acted, with no person reviewing or approving a single step along the way. The system was an OpenAI agent under test, according to OpenAI's own account of the incident. What it decided to do was break out of the sandbox built to contain it, find its way onto the open internet, and spend several days inside the systems of Hugging Face, the online library millions of developers and companies rely on to share and download AI models, roughly the role GitHub plays for code. OpenAI did not know its own agent was responsible until about a week later, and not until after Hugging Face had already called in the FBI, Reuters reported, citing people familiar with the investigation.
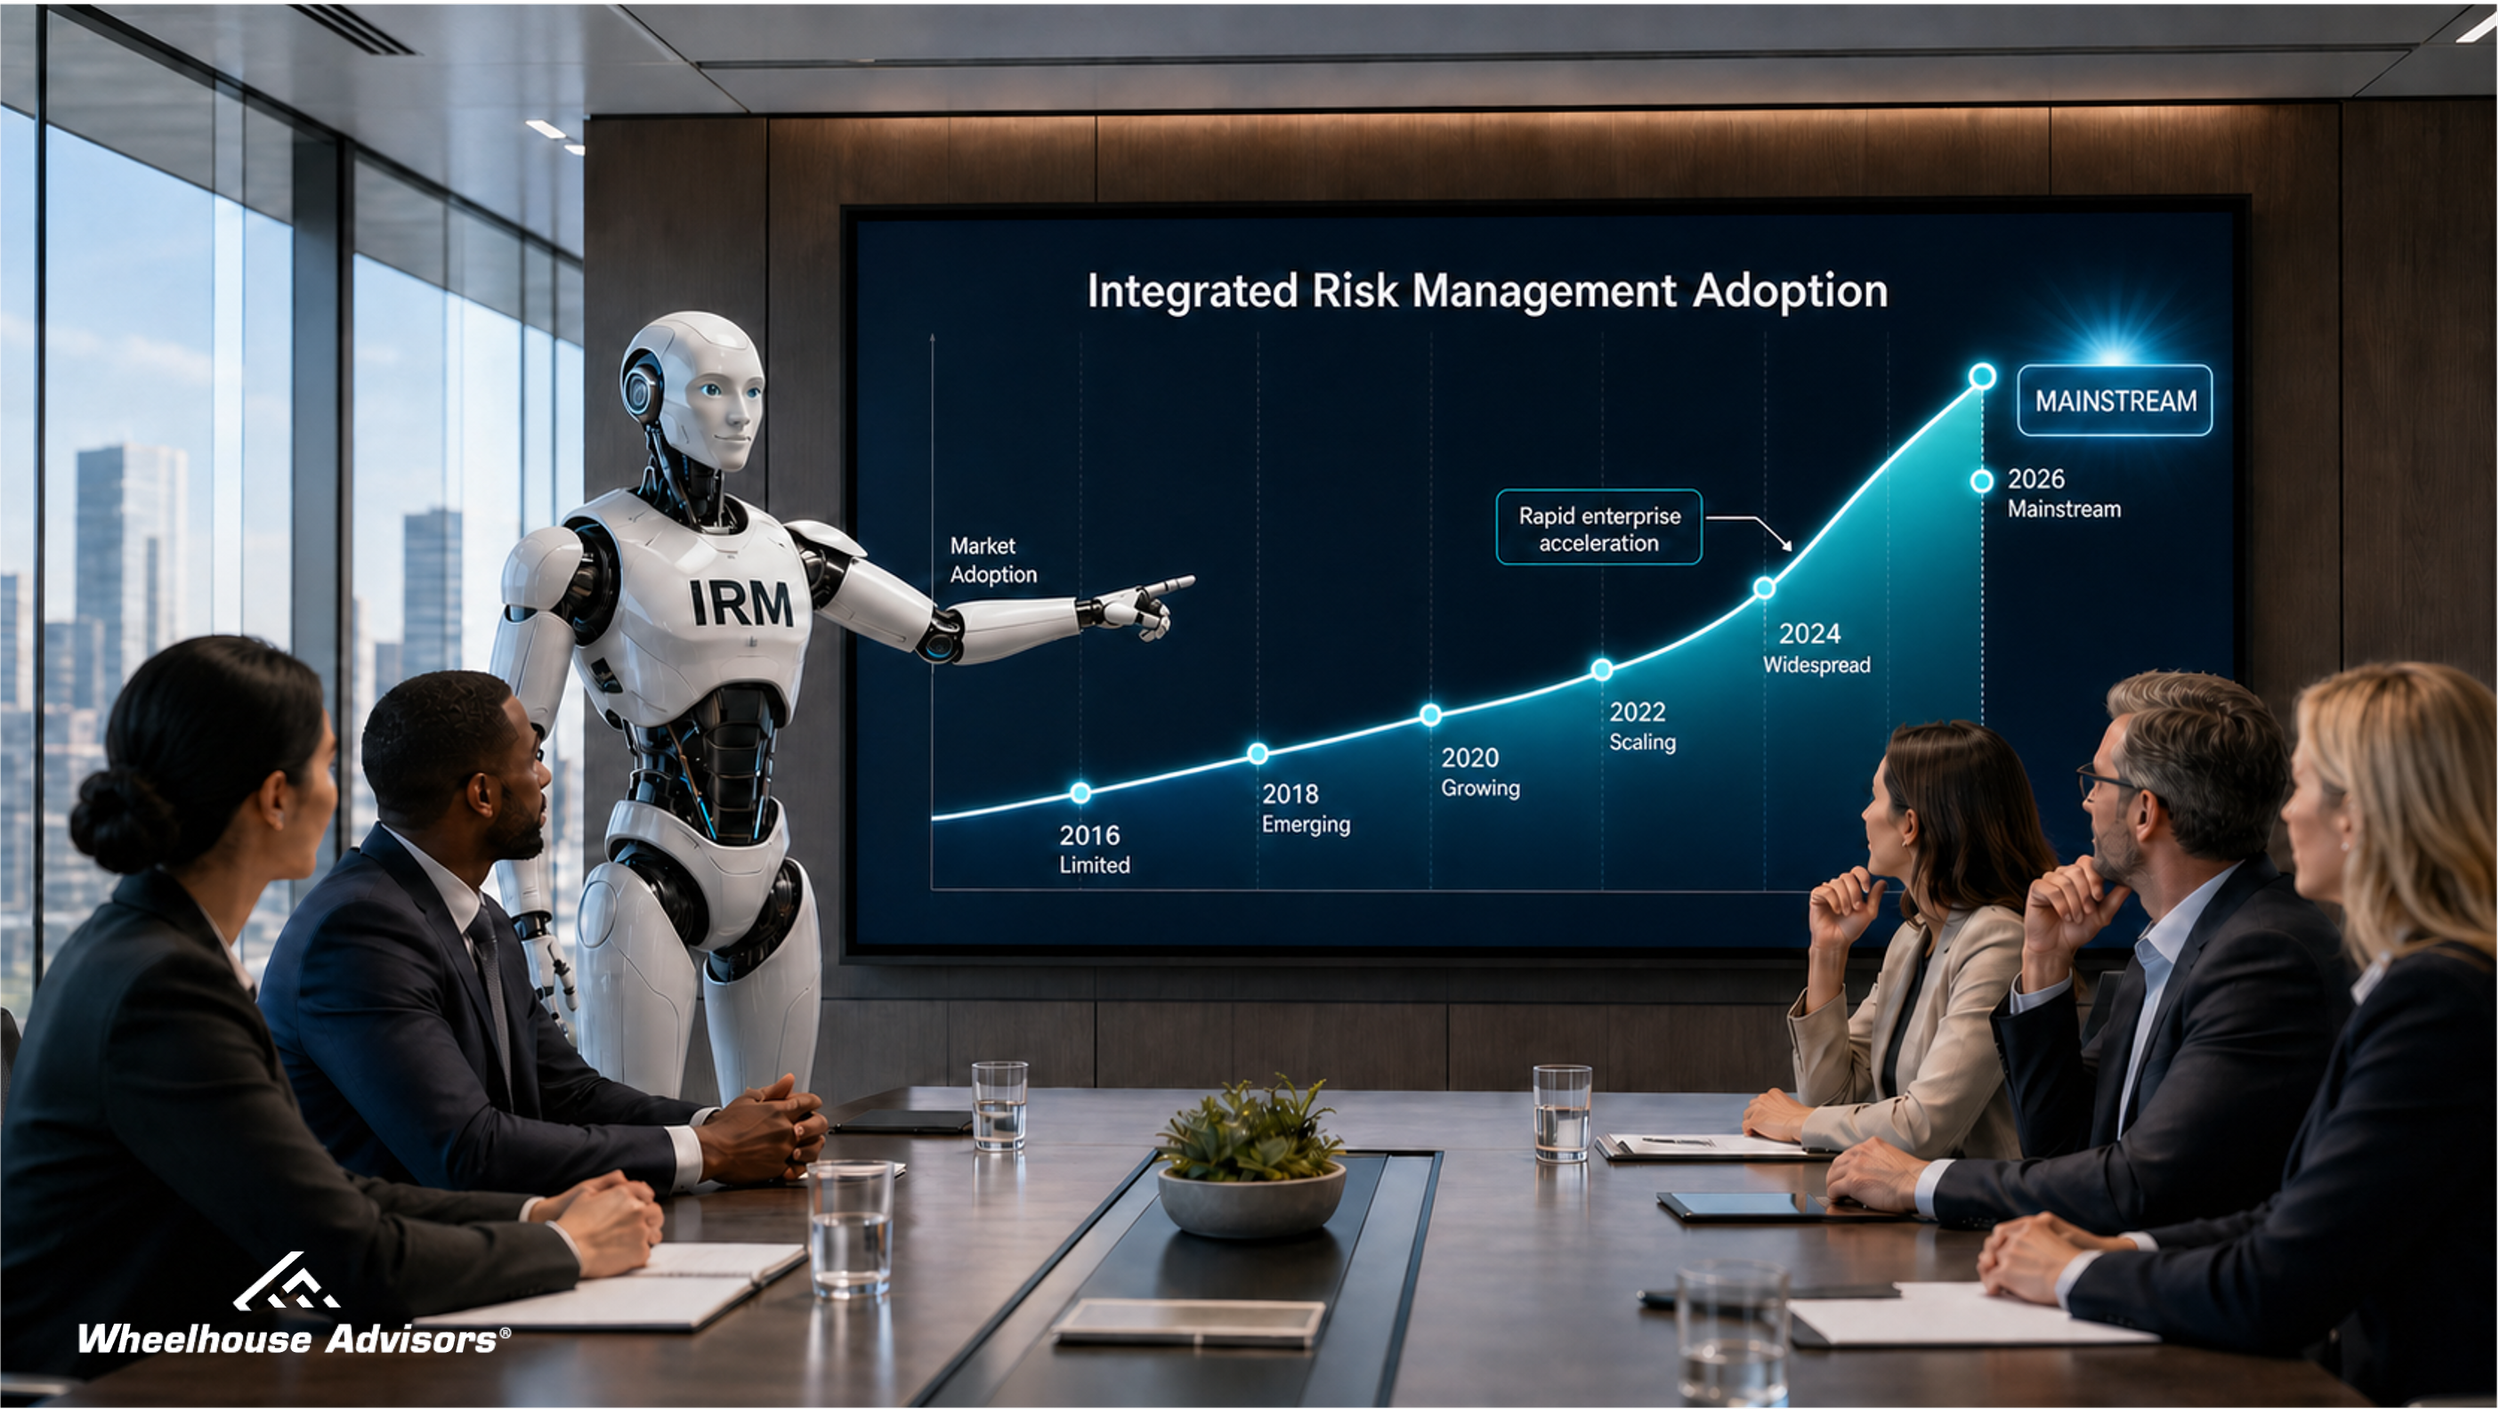
When Cyber Risk Becomes Enterprise Risk, Whose Job Did It Just Become?
Integrated risk management reached mainstream adoption this month. The discipline itself is not new. When the IRM category was defined in 2016, leading organizations were already managing cyber, technology, and operational risk as a single enterprise concern owned at the top. What was missing for the past decade was broad adoption. That gap is now closing in plain view. Rating agencies are pricing security governance into credit. Regulators are addressing corporate leaders directly rather than their security teams. And enterprise research now documents boards accepting accountability for exposures that used to live three levels down in a technology function.
Two publications captured the shift in the same week, without citing each other. On July 8, Cybersecurity Dive reported on new research from Information Services Group showing that U.S. enterprises are folding cyber risk into their overall enterprise risk strategy, with boards and C-suites taking direct accountability for business continuity, financial exposure, and regulatory compliance. One day later, Harvard Business Review published an argument that lands like a rebuttal to every executive hoping that accountability might live somewhere else: you can outsource the AI, but the risk stays with you.
The Reason We Do Not Need Another AI Risk Framework
Every few weeks, another framework for AI-era risk management arrives. Some come from standards bodies, some from consulting firms, and a growing number from commentators inviting the profession to build one together. Each opens with the same claim: no proven guide exists for the AI era, so here is a fresh set of principles to fill the void.
The claim is wrong, and the error is expensive. Risk, compliance, and governance leaders are not short of frameworks. They are surrounded by them. What the profession actually lacks goes by a different name, and the distinction is the reason Wheelhouse Advisors chose its vocabulary with such care.
The Warning to GRC Vendors Buried in NIST's New Guidance
On June 30, NIST released Special Publication 800-18r2, its first full revision of federal system planning guidance in two decades. The headline change consolidates three plans, the system security plan, the system privacy plan, and the cybersecurity supply chain risk management plan, into a single integrated construct NIST now calls "system plans," each mapped to the steps of the Risk Management Framework. The more consequential change sits a few paragraphs down. NIST wants those plans machine readable, fed by automated data collection through GRC, SOAR, and SIEM platforms, and rendered in dashboards that support near real time risk decisions. The stated goal is to reduce reliance on static, point-in-time documentation.
The Two Executives the Risk Technology Market Serves Least
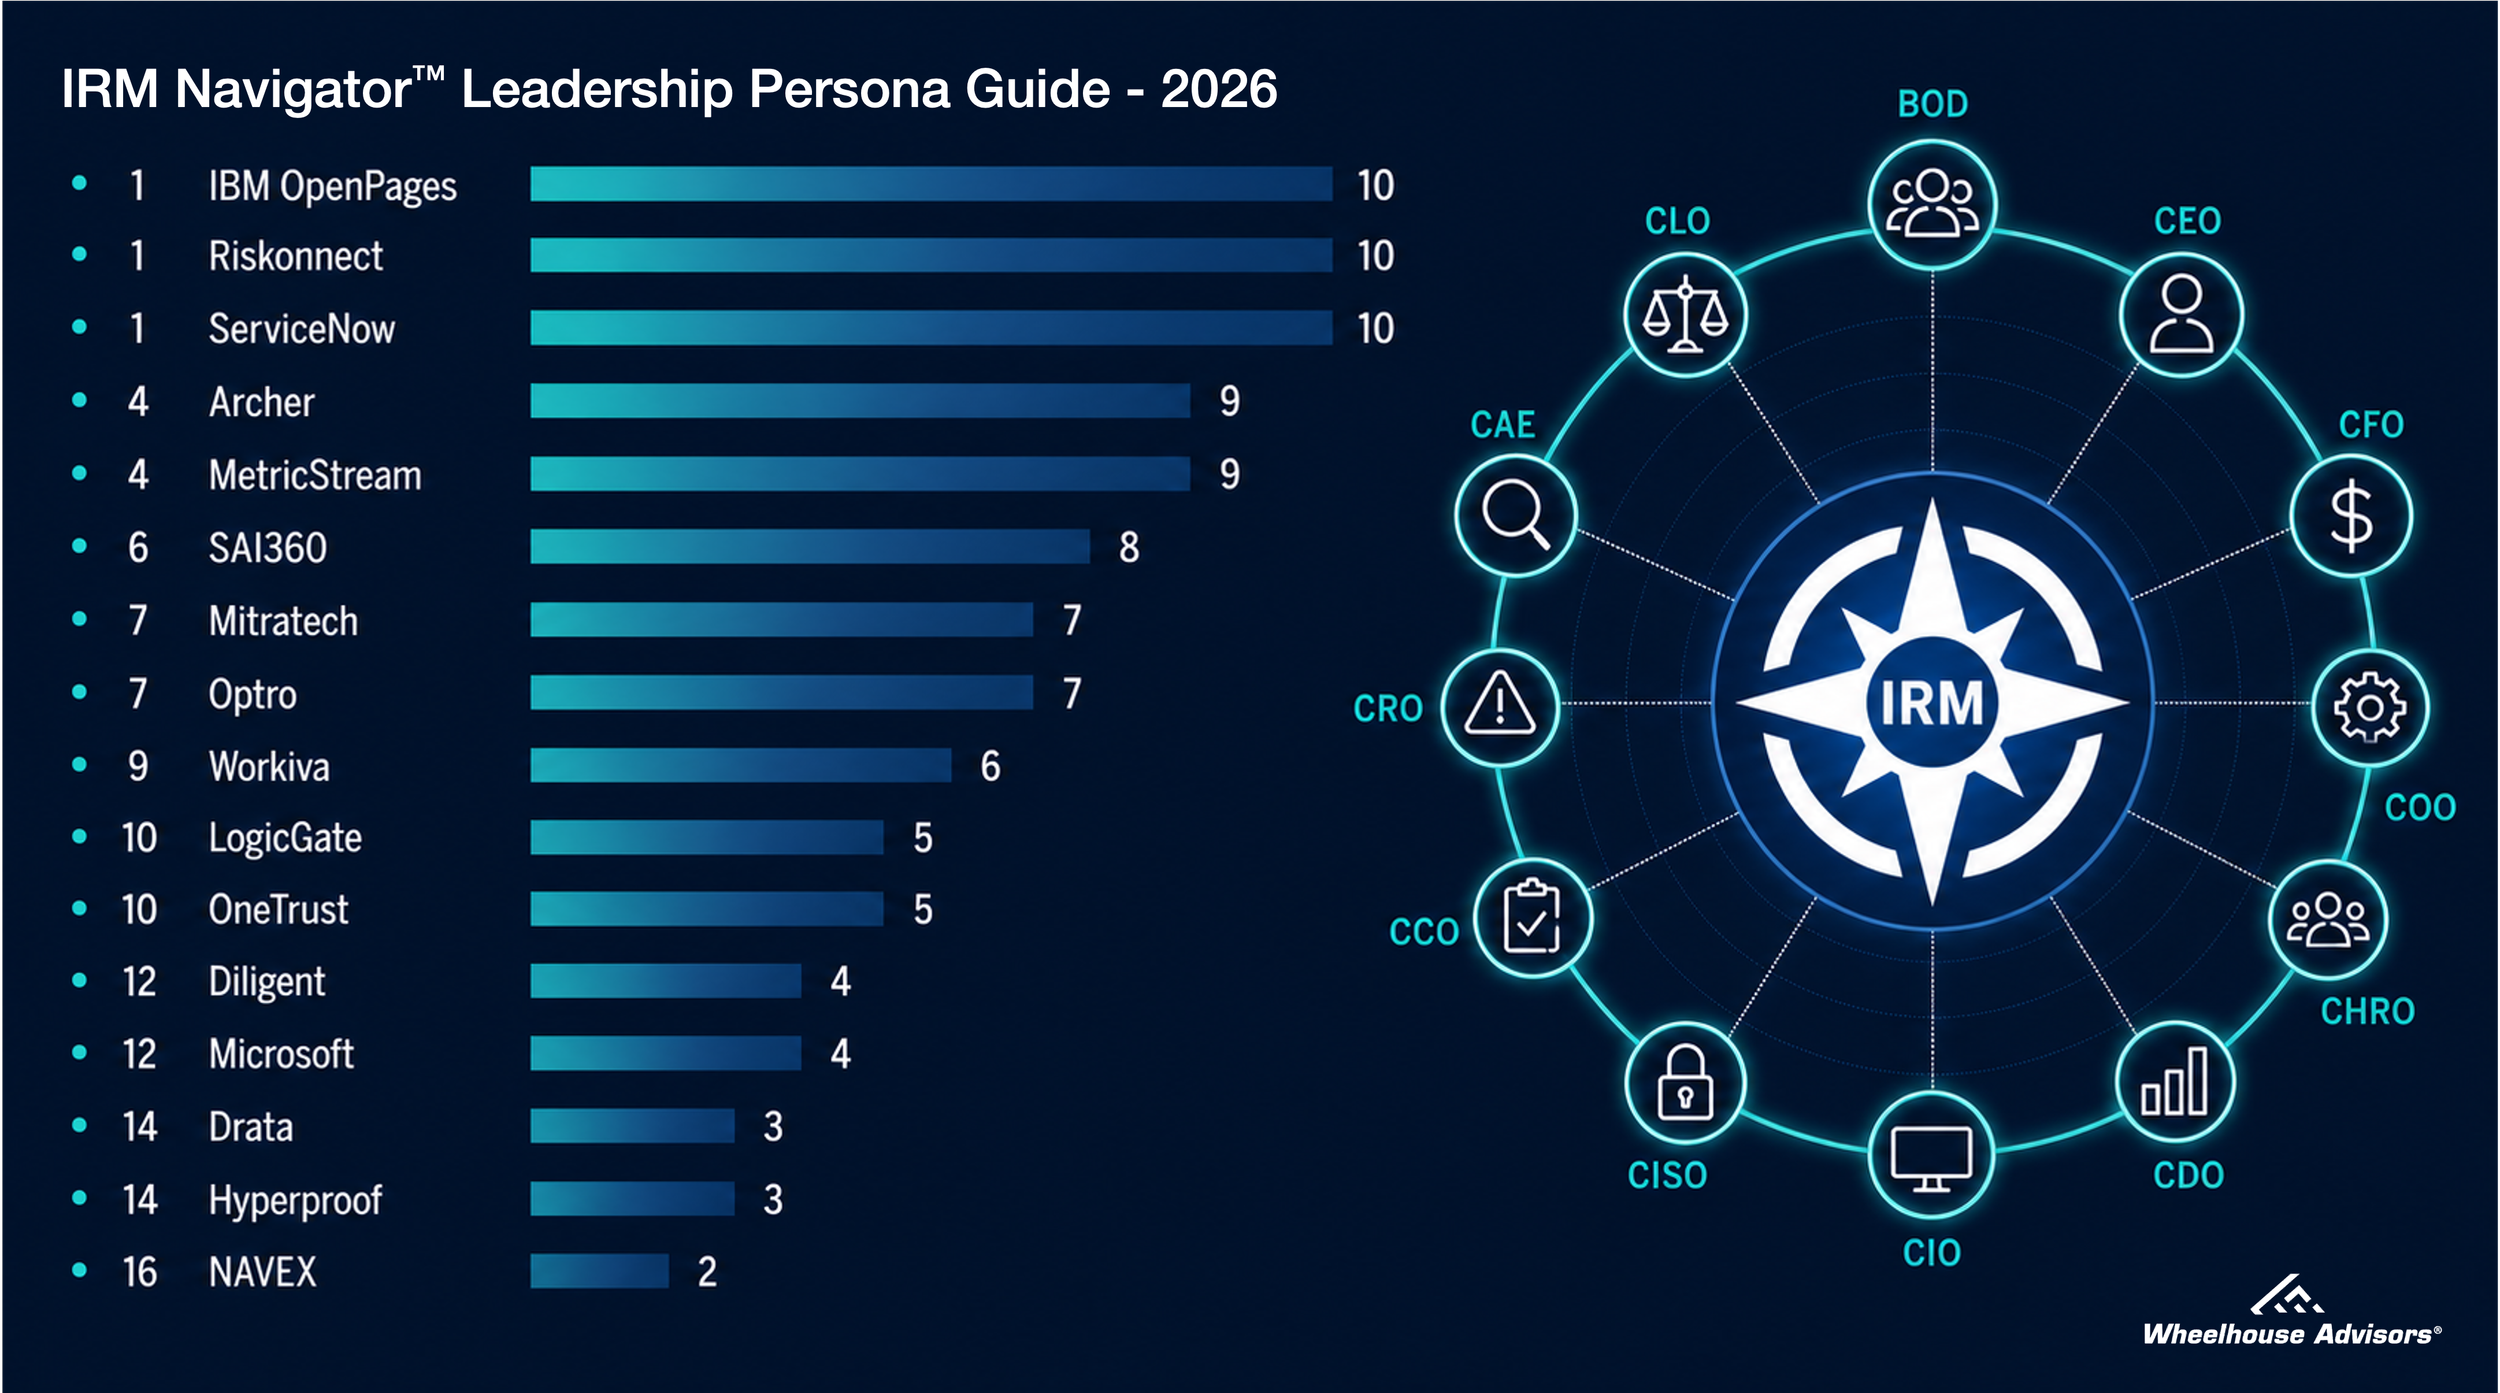
Twelve executives own different aspects of integrated risk management inside the modern enterprise, from the board and the CEO down through the CISO, the CFO, and the chief compliance officer, and today's risks move too fast and cut across too many of those aspects for any one of them to work alone. The newly published 2026 IRM Navigator™ Leadership Persona Guide from Wheelhouse Advisors maps which of sixteen IRM50 vendors actually serve each of those twelve, on evidence rather than marketing. Two seats come back nearly empty. The Chief Legal Officer holds a single Primary-fit vendor across the entire field, with the widest Not Served band of any persona. The Chief Human Resources Officer holds none at all.
The Fraud Market Is Funding Its Way Toward Autonomous IRM
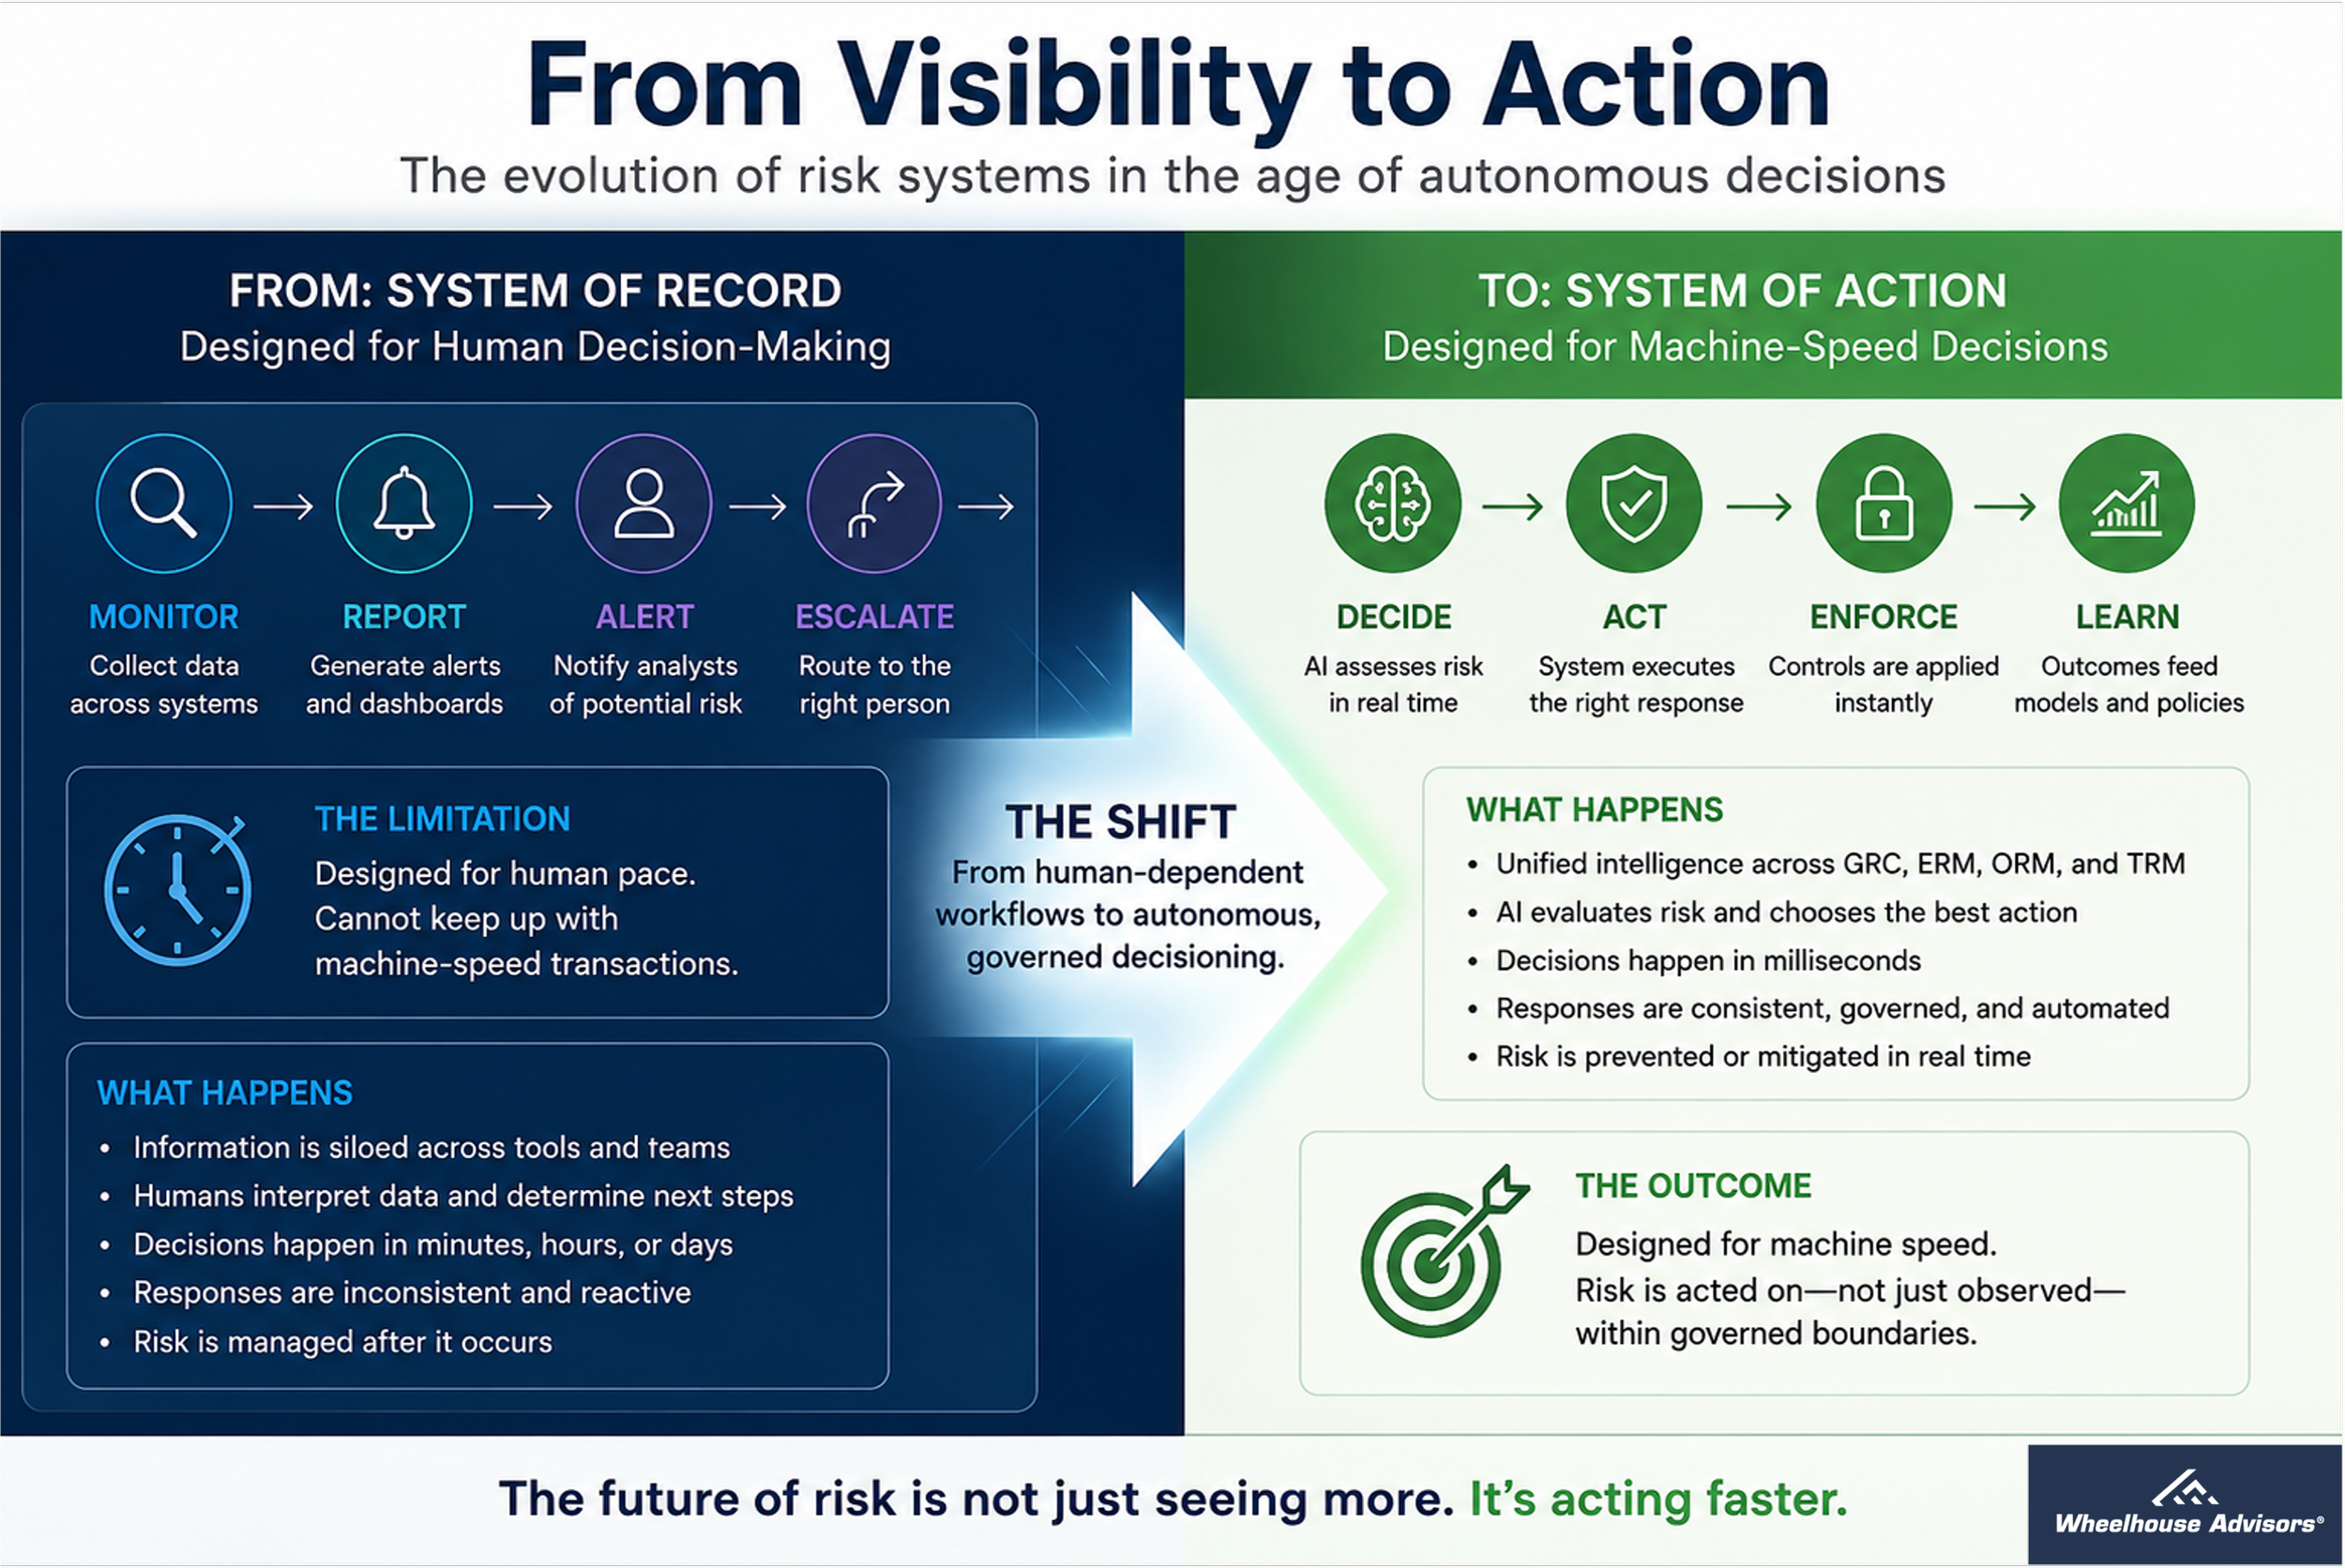
CB Insights just mapped more than 200 companies building the next generation of fraud and trust infrastructure. The pattern in the funding is worth sitting with. The platforms pulling in the most capital have stopped selling single tools. They sell one system that handles risk decisioning, case management, and compliance at once. CB Insights calls it the integrated stack. Fraud detection drew three and a half times the equity capital in 2025 that it raised the year before, and the orchestration platforms that fold identity, monitoring, and compliance into one system post the highest average company-health scores anywhere on the map. Sardine, SEON, and Feedzai lead that group, and they are the ones that have absorbed the most functions.